WO2010047367A1 - 移動通信方法及び交換局 - Google Patents
移動通信方法及び交換局 Download PDFInfo
- Publication number
- WO2010047367A1 WO2010047367A1 PCT/JP2009/068176 JP2009068176W WO2010047367A1 WO 2010047367 A1 WO2010047367 A1 WO 2010047367A1 JP 2009068176 W JP2009068176 W JP 2009068176W WO 2010047367 A1 WO2010047367 A1 WO 2010047367A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- radio access
- security processing
- protocol
- access scheme
- utra
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Images



Classifications
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/08—Access security
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/10—Integrity
- H04W12/106—Packet or message integrity
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/10—Integrity
- H04W12/108—Source integrity
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W36/00—Hand-off or reselection arrangements
- H04W36/0005—Control or signalling for completing the hand-off
- H04W36/0011—Control or signalling for completing the hand-off for data sessions of end-to-end connection
- H04W36/0033—Control or signalling for completing the hand-off for data sessions of end-to-end connection with transfer of context information
- H04W36/0038—Control or signalling for completing the hand-off for data sessions of end-to-end connection with transfer of context information of security context information
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W36/00—Hand-off or reselection arrangements
- H04W36/14—Reselecting a network or an air interface
- H04W36/144—Reselecting a network or an air interface over a different radio air interface technology
- H04W36/1443—Reselecting a network or an air interface over a different radio air interface technology between licensed networks
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L63/00—Network architectures or network communication protocols for network security
- H04L63/12—Applying verification of the received information
- H04L63/123—Applying verification of the received information received data contents, e.g. message integrity
-
- Y—GENERAL TAGGING OF NEW TECHNOLOGICAL DEVELOPMENTS; GENERAL TAGGING OF CROSS-SECTIONAL TECHNOLOGIES SPANNING OVER SEVERAL SECTIONS OF THE IPC; TECHNICAL SUBJECTS COVERED BY FORMER USPC CROSS-REFERENCE ART COLLECTIONS [XRACs] AND DIGESTS
- Y02—TECHNOLOGIES OR APPLICATIONS FOR MITIGATION OR ADAPTATION AGAINST CLIMATE CHANGE
- Y02D—CLIMATE CHANGE MITIGATION TECHNOLOGIES IN INFORMATION AND COMMUNICATION TECHNOLOGIES [ICT], I.E. INFORMATION AND COMMUNICATION TECHNOLOGIES AIMING AT THE REDUCTION OF THEIR OWN ENERGY USE
- Y02D30/00—Reducing energy consumption in communication networks
- Y02D30/70—Reducing energy consumption in communication networks in wireless communication networks
Definitions
- the present invention relates to a mobile communication method and a switching center.
- the mobile station UE performs handover between a cell subordinate to a UTRA radio base station and a cell subordinate to an E-UTRA radio base station.
- the mobile station UE is configured to perform different security processes for communication performed in a cell subordinate to a UTRA radio base station and communication performed in a cell subordinate to an E-UTRA radio base station. ing.
- An object of the present invention is to provide a mobile communication method and an exchange that can appropriately transfer information related to security processing from communication before handover to communication after handover in a procedure for performing handover to a cell. .
- a first feature of the present invention is a mobile communication method, in which a mobile station changes from a first cell under a radio base station of a first radio access scheme to a second cell under a radio base station of a second radio access scheme.
- the exchange station of the second radio access method selects a security processing algorithm of the first protocol used for communication with the mobile station, and the second radio Step B in which an access-system switching center generates a security processing parameter for the first protocol, and the second radio access-system switching station from the second radio access-system radio base station to the second radio (C) including a transparent container including a security processing algorithm of a second protocol used in communication between a radio base station of an access method and the mobile station.
- Receiving a handover request response message, and the second radio access scheme switching center sends the transparent container, the first protocol security processing algorithm, A step D of transmitting a first message including a security processing parameter of a first protocol; and the mobile station, in the first cell, the transparent container, the security processing algorithm of the first protocol, and the first protocol in the first cell.
- the security processing parameters of the second protocol using the security processing algorithm of the first protocol and the security processing parameters of the first protocol.
- Calculate Step F and the mobile station performs security processing in communication using the first protocol using the security processing algorithm of the first protocol and the security processing parameter of the first protocol in the second cell.
- Step G to be performed, and the mobile station uses the second protocol security processing algorithm and the second protocol security processing parameter in the second cell to perform security processing in communication using the second protocol. And the process H is performed.
- a message for a first protocol including a security processing algorithm for the first protocol and a security processing parameter for the first protocol is included in the transparent container. May be sent.
- the second radio access scheme switching center sends the first protocol security processing algorithm and the first radio access scheme switching center to the first radio access scheme switching station.
- a first protocol message including a security processing parameter for one protocol may be included in the first message and transmitted separately from the transparent container.
- the first radio access scheme switching center sends the received first protocol message to the first radio access scheme radio control station.
- a third protocol message used in communication between the mobile switching station and the mobile station, and a radio control station of the first radio access system from the mobile station of the first radio access system Radio control of the first radio access method is performed using the security processing algorithm of the first protocol and the security processing parameter of the first protocol included in the first protocol message included in the received third protocol message.
- a step of transmitting by including in a message for the fourth protocol used in communication between the station and the mobile station There.
- the second radio access scheme switching center sends the first protocol security processing algorithm and the first radio access scheme switching center to the first radio access scheme switching station.
- a security processing parameter for one protocol is included in the first message and transmitted separately from the transparent container, and the switching center for the first radio access scheme transmits the parameter for the first protocol separately from the transparent container.
- a first protocol message including a security processing algorithm and a security processing parameter of the first protocol is converted into a third protocol message used in communication between the exchange station of the first radio access method and the mobile station. You may further have the process of including and transmitting.
- the switching center of the second radio access method performs integrity protection processing using the security processing algorithm of the first protocol and the security processing parameter of the first protocol, Generating the first protocol message, and performing the integrity protection process using the received security processing algorithm of the first protocol and the security processing parameter of the first protocol by the mobile station, Inspecting whether or not the first protocol message has been tampered with, and if the mobile station determines that the first protocol message has been tampered with, for the radio control station of the first radio access scheme, The handover procedure It may further include the step of notifying that failed.
- the second feature of the present invention is that the mobile station performs handover from the first cell under the radio base station of the first radio access scheme to the second cell under the radio base station of the second radio access scheme.
- a switching station capable of functioning as a switching center of the second radio access method capable of performing a procedure, wherein a security processing algorithm of a first protocol used in communication with the mobile station in the procedure is
- a selection unit configured to select;
- a generation unit configured to generate a security processing parameter of the first protocol in the procedure; and a radio of the second radio access scheme in the procedure.
- An algorithm for security processing of the second protocol used in communication between the base station and the radio base station of the second radio access method and the mobile station A receiver configured to receive a handover request response message including a transparent container including a network, and in the procedure, for the exchange station of the first radio access scheme, the transparent container and the first protocol
- the gist of the present invention is to include a transmission unit configured to transmit a first message including a security processing algorithm and a security processing parameter of the first protocol.
- the mobile station performs handover from the first cell under the radio base station of the first radio access scheme to the second cell under the radio base station of the second radio access scheme.
- the procedure for performing it is possible to provide a mobile communication method and an exchange that can appropriately take over information related to security processing from communication before handover to communication after handover.
- FIG. 1 is an overall configuration diagram of a mobile communication system according to a first embodiment of the present invention.
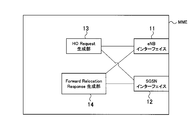
- FIG. 2 is a functional block diagram of the switching center according to the first embodiment of the present invention.
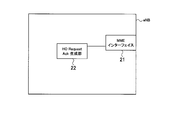
- FIG. 3 is a functional block diagram of the radio base station according to the first embodiment of the present invention.
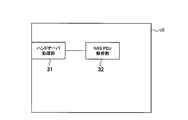
- FIG. 4 is a functional block diagram of the mobile station according to the first embodiment of the present invention.
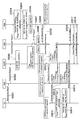
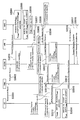
- FIG. 5 is a sequence diagram showing an operation example 1 of the mobile communication system according to the first embodiment of the present invention.
- FIG. 6 is a sequence diagram showing an operation example 2 of the mobile communication system according to the first embodiment of the present invention.
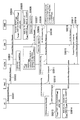
- FIG. 7 is a sequence diagram showing an operation example 3 of the mobile communication system according to the first embodiment of the present invention.
- FIG. 8 is a sequence diagram showing an operation example 4 of the mobile communication system according to the first embodiment of the present invention.
- FIG. 9 is a sequence diagram showing an operation example 5 of the mobile communication system according to the first embodiment of the present invention.
- the mobile communication system includes a switching center SGSN of a UTRA scheme (first radio access scheme), a radio control station RNC of a UTRA scheme, a radio base station NB of a UTRA scheme, An E-UTRA system (second radio access system) switching station MME and an E-UTRA system radio base station eNB are provided.
- a switching center SGSN of a UTRA scheme first radio access scheme
- a radio control station RNC of a UTRA scheme a radio base station NB of a UTRA scheme
- An E-UTRA system (second radio access system) switching station MME and an E-UTRA system radio base station eNB are provided.
- NAS Non Access Stratum, first protocol
- AS Access Stratum, second protocol
- NAS It is assumed that "AS (fourth protocol)” is used in communication between the UTRA radio control station RNC and the mobile station UE.
- the NAS message (first protocol message) transmitted and received between the E-UTRA exchange MME and the mobile station UE is expressed as “NAS PDU (E-UTRA)”, and the E-UTRA radio
- An AS message (second protocol message) transmitted / received between the base station eNB and the mobile station UE is expressed as “AS PDU (E-UTRA)”, and between the UTRA exchange SGSN and the mobile station UE.
- the NAS message (third protocol message) transmitted / received in is expressed as “NAS PDU (UTRA)”
- the AS message (for fourth protocol) transmitted / received between the UTRA radio control station RNC and the mobile station UE Message) is expressed as “AS PDU (UTRA)”.
- the E-UTRA switching center MME includes an eNB interface 11, an SGSN interface 12, a HO Request generator 13, and a Forward Relocation Response generator 14.
- the eNB interface 11 is an interface with the E-UTRA radio base station eNB.
- the eNB interface 11 terminates “S1-Application Protocol” in order to perform communication with the E-UTRA radio base station eNB.
- the eNB interface 11 is configured so that the mobile station UE performs handover from the first cell under the UTRA radio base station NB to the second cell under the E-UTRA radio base station eNB.
- “HO Request (S1 message)” is transmitted to the E-UTRA radio base station eNB, or “HO Request Ack (S1 message)” is received from the E-UTRA radio base station eNB Is configured to do.
- HO Request Ack (S1 message) is a handover request response message including a transparent container “RRCConnectionReconfig” including an AS security processing algorithm of the E-UTRA method.
- AS security processing includes ciphering processing and integrity protection processing.
- the AS ciphering process is a process of encrypting the AS message using the security processing parameter on the originating side and decrypting the AS message using the security processing parameter on the called side.
- the integrity protection processing of the AS is performed by calculating a MAC (Message Authentication Code, for example, 32-bit length) using the AS message and the security processing parameter on the transmission side, and assigning it to the AS message.
- MAC Message Authentication Code, for example, 32-bit length
- NULL NULL
- AES Arithmetic Authentication Standard
- Snow3G AS integrity protection processing algorithms
- the SGSN interface 12 is an interface with a UTRA exchange SGSN.
- the SGSN interface 12 is configured so that the mobile station UE performs a handover from the first cell under the UTRA radio base station NB to the second cell under the E-UTRA radio base station eNB. It is configured to transmit “Forward Relocation Response (first message)” to the UTRA switching center SGSN and to receive “Forward Relocation Request” from the UTRA switching center SGSN.
- the HO Request generator 13 is configured to generate the above-mentioned “HO Request (S1 message)”.
- the HO Request generator 13 selects an NAS security algorithm for the E-UTRA method, and sets the NAS security processing parameters. Configured to generate.
- the HO Request generator 13 selects an E-UTRA NAS security processing algorithm in accordance with “UE security capabilities (mobile station UE security processing capability)” included in the “Forward Relocation Request”. May be.
- such NAS security processing includes ciphering processing and integrity protection processing.
- the NAS ciphering process is a process in which the originating side encrypts the NAS message using the security processing parameter, and the receiving side decrypts the NAS message using the security processing parameter.
- the integrity protection processing of the NAS is performed by calculating the MAC (for example, 32 bits length) using the NAS message and the security processing parameter on the transmission side and attaching it to the NAS message, and on the reception side, the NAS message and the security processing. This is a process for inspecting the presence / absence of falsification in the NAS message using the parameters for use and MAC.
- NAS NAS
- AES Access Security
- Snow3G NAS integrity protection processing algorithms
- the Forward Relocation Response generating unit 14 is configured to generate the above-mentioned “Forward Relocation Response”.
- the Forward Relocation Response generating unit 14 includes a “Forward Relocation” including a transparent container “RRCConnectionReconfig”, an E-UTRA NAS security processing algorithm, and an E-UTRA NAS security processing parameter. “Response” is generated.
- the Forward Relocation Response generator 14 generates an “NAS PDU (E-UTRA method)” including an E-UTRA NAS security processing algorithm and an E-UTRA NAS security processing parameter as a transparent container “ It may be configured to transmit “Forward Relocation Response” in a state included in “RRCConnectionReconfig” (see FIG. 5 described later).
- the radio base station eNB of the E-UTRA scheme is configured to include the “NAS PDU (E-UTRA scheme)” in the transparent container “RRCConnectionReconfig”.
- the Forward Relocation Response generation unit 14 generates “NAS PDU (E-UTRA method)” including an E-UTRA NAS security processing algorithm and an E-UTRA NAS security processing parameter as a transparent container “ Apart from “RRCConnectionReconfig”, it may be configured to be included in “Forward Relocation Response” (see FIGS. 6 and 7 described later).
- the Forward Relocation Response generation unit 14 provides the NAS processing PDU (E-UTRA method) with the E-UTRA NAS security processing algorithm and the E-UTRA NAS security processing parameter. It may be configured to perform the integrity protection processing used.
- the Forward Relocation Response generator 14 includes the E-UTRA NAS security processing algorithm and the E-UTRA NAS security processing parameter in the “Forward Relocation Response” separately from the transparent container “RRCConnectionReconfig”. It may be configured to be included as an information element visible on the SGSN interface 12 (see FIG. 8 described later).
- the E-UTRA radio base station eNB includes an MME interface 21 and a HO Request Ack generation unit 22.
- the MME interface 21 is an interface with an E-UTRA exchange MME.
- the MME interface 21 terminates “S1-Application Protocol” in order to communicate with the E-UTRA exchange MME.
- the MME interface 21 is configured so that the mobile station UE performs a handover from the first cell under the UTRA radio base station NB to the second cell under the E-UTRA radio base station eNB.
- the HO Request Ack generation unit 22 is configured to generate the above-described “HO Request Ack (S1 message)”.
- the HO Request Ack generation unit 22 selects an E-UTRA AS security processing algorithm when generating the above-described “HO Request Ack (S1 message)”, and the E-UTRA method It is configured to generate AS security processing parameters.
- the HO Request Ack generating unit 22 performs the AS security processing of the E-UTRA method according to “UE EPS security capabilities (security processing capability of the mobile station UE)” included in the “HO Request (S1 message)”. You may select the algorithm for use.
- the HO Request Ack generation unit 22 selects the E-UTRA method from the E-UTRA AS security algorithms specified by “allowed AS algorithm” included in the “HO Request (S1 message)”.
- the AS security processing algorithm may be selected.
- the mobile station UE includes a handover processing unit 31 and a NAS PDU analysis unit 32.
- the handover processing unit 31 is requested in a procedure for the mobile station UE to perform a handover from the first cell under the UTRA radio base station NB to the second cell under the E-UTRA radio base station eNB. Is configured to perform processing.
- the handover processing unit 31 uses the E-UTRA NAS security processing algorithm and the E-UTRA NAS security processing parameter to calculate the E-UTRA AS security processing parameter. It is configured.
- the handover processing unit 31 uses the E-UTRA NAS in the handover destination cell by using the E-UTRA NAS security processing algorithm and the E-UTRA NAS security processing parameter.
- Security processing in communication is performed, and security processing in communication using AS of E-UTRA scheme is performed using an algorithm for AS security processing of E-UTRA scheme and security processing parameters of AS of E-UTRA scheme. It is configured.
- the NAS PDU analysis unit 32 performs the integrity protection process using the received E-UTRA NAS security processing algorithm and the E-UTRA NAS security processing parameter, thereby receiving the received “NAS PDU (E -UTRA system) ”is inspected for tampering.
- the handover processing unit 31 uses the handover source radio access device (for example, radio control station RNC or It is configured to notify the switching center SGSN) that the above-described handover procedure has failed.
- the handover source radio access device for example, radio control station RNC or It is configured to notify the switching center SGSN
- Operation examples 1 to 4 of the mobile communication system according to the first embodiment of the present invention will be described with reference to FIGS. Specifically, a procedure for the mobile station UE to perform handover from the first cell under the UTRA radio base station NB to the second cell under the E-UTRA radio base station eNB will be described.
- step S1001 the mobile station UE in communication in the first cell under the UTRA radio base station NB transmits “Measurement Report” to the UTRA radio control station RNC. .
- step S1002 the UTRA radio control station RNC transmits "Relocation Request" to the UTRA exchange SGSN.
- step S1003 the UTRA switching center SGSN transmits “Forward Relocation Request” to the E-UTRA switching center MME.
- Such “UE security capabilities” includes “UE EPS security capabilities” indicating the security processing capability of the mobile station UE in the E-UTRA scheme.
- the “UE security capabilities” may include an information element indicating the security processing capability of the mobile station UE in the UTRA scheme or other radio access schemes.
- step S1004 the E-UTRA switching center MME generates “NONE MME ”.
- “NANCE MME ” is a 32 bit long randomly selected bit string.
- E-UTRA switching center MME generates “K ASME ” by (Equation 1).
- K ASME KDF (CK
- step S ⁇ b> 1005 the E-UTRA switching center MME sets “NAS DL COUNT” and “NAS UL COUNT” to “0”, and then generates “K eNB ” according to (Equation 3).
- NAS DL COUNT is the sequence number of the NAS message of the E-UTRA scheme in the downlink
- NAS UL COUNT is the sequence number of the NAS message of the E-UTRA scheme in the uplink.
- K eNB KDF (K ASME , NAS UL COUNT) (Equation 3)
- the E-UTRA-based switching center MME selects an E-UTRA-based NAS security algorithm in accordance with “UE EPS security capabilities”.
- step S1007 the E-UTRA-based exchange MME transmits “HO Request (S1 message)” to the E-UTRA-based radio base station eNB.
- HO Request (S1 message) includes “K eNB” or “allowed A AS algorithms” and “UE EPS security capabilities”. “HO Request (S1 message)” may not include “allowed AS algorithms”.
- HO Request (S1 message) includes “NAS PDU (E-UTRA system)” including “eKSI”, “NONE MME ”, and “selected NAS algorithm” as transparent containers.
- selected NAS algorithm indicates the security processing algorithm of the NAS of the E-UTRA method selected in step S1006.
- step S1008 the E-UTRA radio base station eNB determines whether the E-UTRA AS security processing algorithm specified by “allowed AS algorithms” is based on “UE EPS security capabilities”. One E-UTRA AS security processing algorithm is selected.
- an E-UTRA AS ciphering processing algorithm and an E-UTRA AS integrity protection processing algorithm are selected.
- step S1009 the E-UTRA radio base station eNB transmits "HO Request Ack (S1 message)" to the E-UTRA exchange MME.
- the “HO Request Ack (S1 message)” includes a transparent container “RRCConnectionReconfig”.
- RRCConnectionReconfig In the transparent container “RRCConnectionReconfig”, “selected AS algorithm”, “eKSI” and “NONE MME ” “NAS PDU” including “NAS algorithm”.
- selected AS algorithm indicates the security processing algorithm of the AS of the E-UTRA method selected in step S1008.
- step S1010 the E-UTRA switching center MME transmits a “Forward Relocation Response” including the transparent container “RRCConnectionReconfig” to the UTRA switching center SGSN.
- step S1011 the UTRA switching center SGSN transmits a “Relocation Command” including the transparent container “RRCConnectionReconfig” to the UTRA radio control station RNC.
- step S1012 the UTRA radio control station RNC transmits a “HOfromUTRACommand (handover instruction message)” including the transparent container “RRCConnectionReconfig” to the mobile station UE.
- step S1013 the mobile station UE, and included in the received "HOfromUTRACommand” extracts "NAS PDU (E-UTRA scheme)", “NAS PDU (E-UTRA scheme)” included in the "NONCE MME” Using “CK” and “IK” used in the communication before the handover, “K ASME ” is generated by (Equation 4).
- K ASME KDF (CK
- eKSI KSI (Formula 5)
- the mobile station UE performs “NAS PDU (E-UTRA scheme)” in the received “HOfromUTRA command” instead of “eKSI” generated by (Equation 5) in the security processing of NAS in the E-UTRA scheme.
- “EKSI” included in “” may be used.
- step S1014 the mobile station UE sets “NAS DL COUNT” and “NAS UL COUNT” to “0”, and then generates “K eNB ” according to (Equation 6).
- K eNB KDF (K ASME , NAS UL COUNT) (Formula 6)
- the mobile station UE performs “RRCConnectionReconfigurationComplete (E-UTRA scheme) in a state where E-UTRA scheme AS security processing using“ K eNB ”is performed on the E-UTRA scheme radio base station eNB. AS message) ”.
- the mobile station UE uses “K ASME ” and “eKSI” to perform “NAS PDU” included in “HOfromUTRACommand” by using an E-UTRA NAS security processing algorithm (such as “AES”).
- E-UTRA system is inspected for integrity by performing integrity protection processing, and“ NAS PDU (E-UTRA system) ”is If it is determined that the UTRA radio control station RNC or the switching center SGSN has notified that the handover procedure has failed, the UTRA AS message or the UTRA NAS message is sent. You may send it.
- step S1016 the E-UTRA radio base station eNB transmits “HO Complete (S1 message)” to the E-UTRA exchange MME.
- step S1017 the E-UTRA switching center MME transmits “Forward Relocation Complete” to the UTRA switching center SGSN.
- step S1018 the UTRA switching center SGSN transmits the E-UTRA switching station SGSN. “Forward Relocation Complete Ack” is transmitted to the exchange MME.
- steps S2001 to S2006 are the same as the operations in steps S1001 to S1006 shown in FIG.
- step S2007 the E-UTRA-based exchange MME transmits “HO Request (S1 message)” to the E-UTRA-based radio base station eNB.
- HO Request (S1 message) includes “K eNB ”, “allowed AS algorithms”, and “UE EPS security capabilities”. “HO Request (S1 message)” may not include “allowed AS algorithms”.
- HO Request S1 message
- NAS PDU including “eKSI”, “NANCE MME ”, and “selected NAS algorithm” shown in FIG. 5 as transparent containers.
- step S2008 the E-UTRA radio base station eNB determines whether the E-UTRA AS security processing algorithm specified by “allowed AS algorithms” based on “UE EPS security capabilities” is selected. One E-UTRA AS security processing algorithm is selected.
- an E-UTRA AS ciphering processing algorithm and an E-UTRA AS integrity protection processing algorithm are selected.
- step S2009 the E-UTRA radio base station eNB transmits “HO Request Ack (S1 message)” to the E-UTRA exchange MME.
- the “HO Request Ack (S1 message)” includes a transparent container “RRCConnectionReconfig”.
- the transparent container “RRCConnectionReconfig” includes only “selected AS algorithm”, and “NAS PDU (E) including“ eKSI ”,“ NONE MME ”, and“ selected NAS algorithm ”as shown in FIG. -UTRA method) "is not included.
- step S2010 the E-UTRA switching center MME transmits a “Forward Relocation Response” including the transparent container “RRCConnectionReconfig” to the UTRA switching center SGSN.
- the E-UTRA switching center MME in the “Forward Relocation Response”, separately from the transparent container “RRCConnectionReconfig”, “eKSI”, “NANCE MME ” and “selected NAS algorithm” as shown in FIG. “NAS PDU (E-UTRA system)” is included.
- step S2011 the UTRA exchange SGSN transmits a “Relocation Command” including the transparent containers “RRCConnectionReconfig” and “NAS PDU (UTRA method)” to the UTRA radio control station RNC.
- the UTRA exchange SGSN transmits the “NAS PDU (E-UTRA scheme)” received from the E-UTRA exchange MME in the “NAS PDU (UTRA scheme)”.
- step S2012 the UTRA radio control station RNC transmits a “HOfromUTRACommand (handover instruction message)” including a transparent container “RRCConnectionReconfig” and “NAS PDU (UTRA scheme)” to the mobile station UE.
- HOfromUTRACommand handover instruction message
- NAS PDU User Plane Data Unit
- steps S2013 to S2018 are the same as the operations in steps S1013 to S1018 shown in FIG.
- steps S3001 to S2011 are the same as the operations in steps S2001 to S2011 shown in FIG.
- step S3012A the UTRA radio control station RNC transmits “Direct Transfer (AS message)” including “NAS PDU (UTRA method)” included in the “Relocation Command” received from the UTRA exchange SGSN. Separately from the container “RRCConnectionReconfig”, it is transmitted to the mobile station UE.
- the UTRA radio control station RNC includes a transparent container “RRCConnectionReconfig” and does not include “NAS PDU (UTRA scheme)” or “NAS PDU (E-UTRA scheme)” for the mobile station UE. “HOfromUTRACommand (handover instruction message)” is transmitted.
- the “Direct Transfer” and “HOfromUTRACommand” may be transmitted by the same radio bearer in which the order is guaranteed so that the order of reception processing of “Direct Transfer” and “HOfromUTRACommand” in the mobile station UE is guaranteed. .
- the mobile station UE transmits a response signal (UTRA system AS message) to “Direct Transfer” and the UTRA radio control station RNC receives the response signal (UTRA system AS message)
- the UTRA system The radio control station RNC may be configured to transmit “HOfromUTRACommand”.
- the mobile station UE transmits a response signal (a UTRA system NAS message) to the “NAS PDU (UTRA system)” included in the “Direct Transfer”, and the UTRA system switching station SGSN receives After receiving the NAS message, the UTRA switching center SGSN notifies the UTRA radio control station RNC that the response signal has been received, and the UTRA radio control station RNC sends the notification. After receiving, “HOfromUTRACommand” may be configured to be transmitted.
- steps S3013 to S3018 are the same as those in steps S1013 to S1018 shown in FIG.
- steps S4001 to S4009 are the same as the operations in steps S3001 to S3009 shown in FIG.
- step S4010 the E-UTRA switching center MME transmits a “Forward Relocation Response” including the above-described transparent container “RRCConnectionReconfig” to the UTRA switching center SGSN.
- the switching center MME of the E-UTRA method includes information elements “eKSI”, “NANCE MME ”, and “selected NAS algorithm” in the “Forward Relocation Response”, separately from the transparent container “RRCConnectionReconfig”, Include as.
- step S4011A the UTRA switching center SGSN generates “NAS PDU (UTRA method)” including “eKSI”, “NONE MME ”, and “selected NAS algorithm” included in “Forward Relocation Response”.
- step S4011B “Ack” indicating that the “NAS PDU (UTRA scheme)” has been received is received from the mobile station UE.
- the UTRA switching center SGSN includes the transparent container “RRCConnectionReconfig” and does not include the above “eKSI”, “NONE MME ”, and “selected NAS algorithm” for the UTRA radio control station RNC. Send “Relocation Command”.
- the UTRA radio control station RNC includes a transparent container “RRCConnectionReconfig” and “HOfromUTRACommand (not including“ eKSI ”,“ NANCE MME ”, and“ selected NAS algorithm ”) for the mobile station UE. Handover instruction message) ".
- steps S4013 to S4018 are the same as those in steps S1013 to S1018 shown in FIG.
- steps S5001 to S5006 are the same as the operations in steps S1001 to S1006 shown in FIG.
- step S5007 the E-UTRA-based exchange MME transmits “HO Request (S1 message)” to the E-UTRA-based radio base station eNB.
- HO Request (S1 message) includes “K eNB ”, “allowed AS algorithms”, “UE EPS security capabilities”, “eKSI”, “NONE MME ”, and “selected NAS algorithm”. Yes. “HO Request (S1 message)” may not include “allowed AS algorithms”.
- step S5008 the E-UTRA radio base station eNB determines, based on “UE EPS security capabilities”, from among the E-UTRA AS security processing algorithms specified by “allowed AS algorithms”. One E-UTRA AS security processing algorithm is selected.
- an E-UTRA AS ciphering processing algorithm and an E-UTRA AS integrity protection processing algorithm are selected.
- step S5009 the E-UTRA radio base station eNB transmits “HO Request Ack (S1 message)” to the E-UTRA exchange MME.
- the "HO Request Ack (S1 message)" is included the transparent container "RRCConnectionReconfig", in the transparent container “RRCConnectionReconfig", "selected AS algorithm” and “eKSI” and “NONCE MME” and “selected NAS algorithm ".
- steps S5010 to S5018 are the same as those in steps S1010 to S1018 shown in FIG.
- the mobile station UE performs handover from a cell under the UTRA radio base station NB to a cell under the E-UTRA radio base station eNB.
- the UTRA NAS security parameter, the UTRA AS security parameter, etc. as the E-UTRA NAS security parameter, the E-UTRA AS security parameter, etc. It can be taken over properly.
- E-UTRA NAS security processing parameters “eKSI” and “NANCE MME ” are not directly included as information elements in E-UTRA AS message “RRCConnectionReconfig”. Therefore, the independence of NAS and AS can be maintained.
- NAS PDU including “selected NAS algorithm”, “eKSI”, and “NONE MME ”.
- E-UTRA E-UTRA scheme
- the operations of the mobile station UE, the radio base station NB and eNB, the switching center SGSN and MME, and the radio control station RNC described above may be implemented by hardware or by a software module executed by a processor. Or it may be implemented by a combination of both.
- Software modules include RAM (Random Access Memory), flash memory, ROM (Read Only Memory), EPROM (Erasable Programmable ROM), EEPROM (Electronically Erasable and Programmable, Removable ROM, and Hard Disk). Alternatively, it may be provided in an arbitrary format storage medium such as a CD-ROM.
- the storage medium is connected to the processor so that the processor can read and write information from and to the storage medium. Further, such a storage medium may be integrated in the processor. Further, such a storage medium and a processor may be provided in the ASIC. Such an ASIC may be provided in the mobile station UE, the radio base station NB and eNB, the exchange SGSN and MME, and the radio control station RNC. Further, the storage medium and the processor may be provided as a discrete component in the mobile station UE, the radio base station NB and eNB, the exchange SGSN and MME, and the radio control station RNC.
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Computer Hardware Design (AREA)
- Computing Systems (AREA)
- General Engineering & Computer Science (AREA)
- Mobile Radio Communication Systems (AREA)
Abstract
Description
図1乃至図4を参照して、本発明の第1の実施形態に係る移動通信システムの構成について説明する。
図5乃至図9を参照して、本発明の第1の実施形態に係る移動通信システムの動作例1乃至4について説明する。具体的には、移動局UEが、UTRA方式の無線基地局NB配下の第1セルからE-UTRA方式の無線基地局eNB配下の第2セルに対してハンドオーバを行うための手順について説明する。
また、E-UTRA方式の交換局MMEが、(式2)によって、「eKSI」を生成する。
ステップS1005において、E-UTRA方式の交換局MMEが、「NAS DL COUNT」及び「NAS UL COUNT」を「0」とした後、(式3)によって、「KeNB」を生成する。ここで、「NAS DL COUNT」は、下りリンクにおけるE-UTRA方式のNASメッセージのシーケンス番号であり、「NAS UL COUNT」は、上りリンクにおけるE-UTRA方式のNASメッセージのシーケンス番号である。
ステップS1006において、E-UTRA方式の交換局MMEが、「UE EPS security capabilities」に応じて、E-UTRA方式のNASのセキュリティ処理用アルゴリズムを選択する。
また、移動局UEが、ハンドオーバ前の通信で用いている「KSI」を用いて、(式5)によって、「eKSI」を生成してもよい。
ここで、移動局UEは、E-UTRA方式のNASのセキュリティ処理において、(式5)によって生成された「eKSI」の代わりに、受信した「HOfromUTRACommand」内の「NAS PDU(E-UTRA方式)」に含まれる「eKSI」を用いてもよい。
ステップS1015において、移動局UEは、E-UTRA方式の無線基地局eNBに対して、「KeNB」を用いたE-UTRA方式のASのセキュリティ処理を施した状態の「RRCConnectionReconfigurationComplete(E-UTRA方式のASメッセージ)」を送信する。
本発明の第1の実施形態に係る移動通信システムによれば、移動局UEが、UTRA方式の無線基地局NB配下のセルからE-UTRA方式の無線基地局eNB配下のセルに対してハンドオーバを行うための手順において、UTRA方式のNASのセキュリティ用パラメータやUTRA方式のASのセキュリティ用パラメータ等を、E-UTRA方式のNASのセキュリティ用パラメータやE-UTRA方式のASのセキュリティ用パラメータ等として、適切に引き継がせることができる。
Claims (4)
- 移動局が、第1無線アクセス方式の無線基地局配下の第1セルから第2無線アクセス方式の無線基地局配下の第2セルに対してハンドオーバを行うための手順において、
前記第1無線アクセス方式の交換局が、前記第2無線アクセス方式の交換局に対して、前記移動局と該第1無線アクセス方式の交換局との間の通信で用いられる該第1無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータ及び該移動局の該第2無線アクセス方式におけるセキュリティ処理能力を含むハンドオーバ要求メッセージを送信する工程Aと、
前記第2無線アクセス方式の交換局が、前記移動局の該第2無線アクセス方式におけるセキュリティ処理能力に基づいて、該移動局と該第2無線アクセス方式の交換局との間の通信で用いられる該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズムを選択する工程Bと、
前記第2無線アクセス方式の交換局が、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータを生成する工程Cと、
前記第2無線アクセス方式の交換局が、該第2無線アクセス方式の無線基地局に対して、前記移動局の該第2無線アクセス方式におけるセキュリティ処理能力と、前記工程Bで選択された該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズム及び該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータとを含むハンドオーバ要求メッセージを送信する工程Dと、
前記第2無線アクセス方式の無線基地局が、前記移動局の該第2無線アクセス方式におけるセキュリティ処理能力に基づいて、該移動局と該第2無線アクセス方式の無線基地局との間の通信で用いられる該第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズムを選択する工程Eと、
前記第2無線アクセス方式の無線基地局が、該第2無線アクセス方式の交換局に対して、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズム、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータ、及び、前記工程Eで選択された該第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズムを、トランスペアレントコンテナに含むハンドオーバ要求応答メッセージを送信する工程Fと、
前記第2無線アクセス方式の交換局が、受信した前記ハンドオーバ要求応答メッセージに応じて、前記第1無線アクセス方式の交換局に対して、前記トランスペアレントコンテナを含むメッセージを送信する工程Gと、
前記移動局が、前記第1セルにおいて、前記トランスペアレントコンテナを受信すると、前記第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズム及び該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータを用いて、該第2無線アクセス方式の第2プロトコルのセキュリティ処理用パラメータを算出する工程Hと、
前記移動局が、前記第2セルにおいて、前記第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズム及び該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータを用いて、前記第2無線アクセス方式の第1プロトコルを用いた通信におけるセキュリティ処理を行う工程Iと、
前記移動局が、前記第2セルにおいて、前記第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズム及び該第2無線アクセス方式の第2プロトコルのセキュリティ処理用パラメータを用いて、該第2無線アクセス方式の第2プロトコルを用いた通信におけるセキュリティ処理を行う工程Jとを有することを特徴とする移動通信方法。 - 前記第2無線アクセス方式の交換局が、前記第1プロトコルのセキュリティ処理用アルゴリズム及び該第1プロトコルのセキュリティ処理用パラメータを用いたインテグリティプロテクション処理を行うことによって、前記第1プロトコル用メッセージを生成する工程と、
前記移動局が、受信した前記第1プロトコルのセキュリティ処理用アルゴリズムと該第1プロトコルのセキュリティ処理用パラメータを用いたインテグリティプロテクション処理を行うことによって、前記第1プロトコル用メッセージに対する改竄の有無を検査する工程と、
前記移動局が、前記第1プロトコル用メッセージに対する改竄があると判断された場合、前記第1無線アクセス方式の無線制御局又は該第1無線アクセス方式の交換局に対して、前記ハンドオーバ手順が失敗した旨を通知する工程とを更に有することを特徴とする請求項1に記載の移動通信方法。 - 移動局が、第1無線アクセス方式の無線基地局配下の第1セルから第2無線アクセス方式の無線基地局配下の第2セルに対してハンドオーバを行うための手順を行うことができる該第2無線アクセス方式の交換局として機能することができる交換局であって、
前記手順において、前記第1無線アクセス方式の交換局から、前記移動局と該第1無線アクセス方式の交換局との間の通信で用いられる該第1無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータ及び前記移動局の前記第2無線アクセス方式におけるセキュリティ処理能力を含むハンドオーバ要求メッセージを受信するように構成されている第1受信部と、
前記手順において、前記第1受信部によって受信された前記移動局の前記第2無線アクセス方式におけるセキュリティ処理能力に基づいて、該移動局との間の通信で用いられる該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズムを選択するように構成されている選択部と、
前記手順において、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータを生成するように構成されている生成部と、
前記第2無線アクセス方式の無線基地局に対して、前記移動局の該第2無線アクセス方式におけるセキュリティ処理能力と、前記選択部によって選択された該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズムと、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータとを含むハンドオーバ要求メッセージを送信するように構成されている第1送信部と、
前記手順において、前記第2無線アクセス方式の無線基地局から、該第2無線アクセス方式の無線基地局の第1プロトコルのセキュリティ処理用アルゴリズム、該第2無線アクセス方式の無線基地局第1プロトコルのセキュリティ処理用パラメータ、及び、該第2無線アクセス方式の無線基地局と前記移動局との間の通信で用いられる該第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズムを、トランスペアレントコンテナに含むハンドオーバ要求応答メッセージを受信するように構成されている第2受信部と、
前記手順において、前記第1無線アクセス方式の交換局に対して、前記トランスペアレントコンテナを含むメッセージを送信するように構成されている第2送信部とを具備することを特徴とする交換局。 - 移動局が、第1無線アクセス方式の無線基地局配下の第1セルから第2無線アクセス方式の無線基地局配下の第2セルに対してハンドオーバを行うための手順を行うことができる該第2無線アクセス方式の無線基地局として機能することができる無線基地局であって、
前記手順において、前記第2無線アクセス方式の交換局から、前記移動局の該第2無線アクセス方式におけるセキュリティ処理能力と、該移動局と該第2無線アクセス方式の交換局との間の通信で用いられる該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズムと、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータとを含むハンドオーバ要求メッセージを受信するように構成されている受信部と、
前記手順において、前記移動局の前記第2無線アクセス方式におけるセキュリティ処理能力に基づいて、該移動局と該第2無線アクセス方式の無線基地局との間で用いられる該第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズムを選択するように構成されている選択部と、
前記手順において、前記第2無線アクセス方式の交換局に対して、前記選択部によって選択された該第2無線アクセス方式の第2プロトコルのセキュリティ処理用アルゴリズムと、該第2無線アクセス方式の第1プロトコルのセキュリティ処理用アルゴリズム及び該第2無線アクセス方式の第1プロトコルのセキュリティ処理用パラメータを含むトランスペアレントコンテナとを含むハンドオーバ要求応答メッセージを送信するように構成されている送信部とを具備することを特徴とする無線基地局。
Priority Applications (7)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| CA2725474A CA2725474C (en) | 2008-10-22 | 2009-10-22 | Mobile communication method and switching center |
| CN2009801164735A CN102017680B (zh) | 2008-10-22 | 2009-10-22 | 移动通信方法及交换台 |
| BRPI0919721A BRPI0919721A2 (pt) | 2008-10-22 | 2009-10-22 | método de comunicação móvel e permuta |
| MX2010012135A MX2010012135A (es) | 2008-10-22 | 2009-10-22 | Metodo de comunicacion movil y centro de conmutacion. |
| EP09822064A EP2268070B1 (en) | 2008-10-22 | 2009-10-22 | Mobile communication method and exchange |
| AU2009307353A AU2009307353B2 (en) | 2008-10-22 | 2009-10-22 | Mobile communication method and switching center |
| US12/989,801 US8346261B2 (en) | 2008-10-22 | 2009-10-22 | Mobile communication method and switching center |
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2008272517A JP4435254B1 (ja) | 2008-10-22 | 2008-10-22 | 移動通信方法及び交換局 |
| JP2008-272517 | 2008-10-22 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2010047367A1 true WO2010047367A1 (ja) | 2010-04-29 |
Family
ID=42119404
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/JP2009/068176 Ceased WO2010047367A1 (ja) | 2008-10-22 | 2009-10-22 | 移動通信方法及び交換局 |
Country Status (11)
| Country | Link |
|---|---|
| US (1) | US8346261B2 (ja) |
| EP (1) | EP2268070B1 (ja) |
| JP (1) | JP4435254B1 (ja) |
| KR (1) | KR101039345B1 (ja) |
| CN (1) | CN102017680B (ja) |
| AU (1) | AU2009307353B2 (ja) |
| BR (1) | BRPI0919721A2 (ja) |
| CA (1) | CA2725474C (ja) |
| MX (1) | MX2010012135A (ja) |
| RU (1) | RU2450482C1 (ja) |
| WO (1) | WO2010047367A1 (ja) |
Cited By (1)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| WO2011140695A1 (en) | 2010-05-10 | 2011-11-17 | Nokia Corporation | Key derivation during inter-network handover |
Families Citing this family (14)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US9002357B2 (en) * | 2009-06-26 | 2015-04-07 | Qualcomm Incorporated | Systems, apparatus and methods to facilitate handover security |
| ES2675326T3 (es) | 2009-10-05 | 2018-07-10 | Telefonaktiebolaget Lm Ericsson (Publ) | Método y aparato en un sistema de telecomunicación |
| US9167424B2 (en) * | 2010-01-18 | 2015-10-20 | Htc Corporation | Method of handling security in SRVCC handover and related communication device |
| JP5547340B2 (ja) * | 2010-05-04 | 2014-07-09 | クゥアルコム・インコーポレイテッド | 共用回線交換セキュリティコンテキスト |
| EP3300408B1 (en) | 2011-10-28 | 2022-03-16 | NEC Corporation | Secure method for mtc device triggering |
| CN104247328B (zh) | 2013-04-17 | 2017-06-06 | 华为技术有限公司 | 数据传输方法和装置 |
| CN104969578B (zh) * | 2013-04-17 | 2019-06-21 | 华为技术有限公司 | 数据传输方法、装置及系统 |
| WO2016013329A1 (ja) * | 2014-07-25 | 2016-01-28 | 日本電気株式会社 | 無線基地局およびその制御方法 |
| CN107241764B (zh) * | 2016-03-29 | 2020-11-06 | 电信科学技术研究院 | 一种上行、下行小数据传输方法及装置 |
| US10123243B2 (en) | 2016-10-21 | 2018-11-06 | Htc Corporation | Device and method of handling tight interworking of two cellular systems |
| EP3684138B1 (en) * | 2017-10-13 | 2024-08-14 | Samsung Electronics Co., Ltd. | Method and apparatus for transmitting and receiving data in wireless communication system |
| CN111971988B (zh) | 2018-02-19 | 2024-05-07 | 瑞典爱立信有限公司 | 支持不同无线通信系统之间的互通和/或移动性 |
| CN115696319A (zh) * | 2021-07-27 | 2023-02-03 | 华为技术有限公司 | 一种通信方法及装置 |
| CN121100512A (zh) * | 2023-05-12 | 2025-12-09 | 思科技术公司 | 各代接入点之间利用不同的安全协议的漫游 |
Citations (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2003516000A (ja) * | 1999-11-23 | 2003-05-07 | ノキア コーポレイション | 移動ターミナルハンドオーバー中のセキュリティ関連性の転送 |
| JP2006332788A (ja) * | 2005-05-23 | 2006-12-07 | Toshiba Corp | 基地局装置、無線通信システム、基地局制御プログラムおよび基地局制御方法 |
| JP2007515827A (ja) * | 2003-09-12 | 2007-06-14 | 株式会社エヌ・ティ・ティ・ドコモ | 異種ネットワークにおけるシームレスハンドオーバ |
Family Cites Families (15)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US6137791A (en) * | 1997-03-25 | 2000-10-24 | Ericsson Telefon Ab L M | Communicating packet data with a mobile station roaming within an incompatible mobile network |
| US6370380B1 (en) * | 1999-02-17 | 2002-04-09 | Telefonaktiebolaget Lm Ericsson (Publ) | Method for secure handover |
| RU2307473C2 (ru) * | 2002-08-01 | 2007-09-27 | Нокиа Корпорейшн | Передача перемежающихся потоков многокомпонентных данных |
| KR100889865B1 (ko) * | 2002-11-07 | 2009-03-24 | 엘지전자 주식회사 | 무선 이동통신 시스템의 통신방법 |
| KR101514845B1 (ko) | 2006-03-31 | 2015-04-23 | 삼성전자주식회사 | 액세스 시스템 간의 핸드오버 시의 인증 절차를 최적화하기위한 시스템 및 방법 |
| US8094817B2 (en) * | 2006-10-18 | 2012-01-10 | Telefonaktiebolaget Lm Ericsson (Publ) | Cryptographic key management in communication networks |
| CN101304600B (zh) * | 2007-05-08 | 2011-12-07 | 华为技术有限公司 | 安全能力协商的方法及系统 |
| CN101309500B (zh) * | 2007-05-15 | 2011-07-20 | 华为技术有限公司 | 不同无线接入技术间切换时安全协商的方法和装置 |
| WO2009020789A2 (en) * | 2007-08-03 | 2009-02-12 | Interdigital Patent Holdings, Inc. | Security procedure and apparatus for handover in a 3gpp long term evolution system |
| US20090209259A1 (en) * | 2008-02-15 | 2009-08-20 | Alec Brusilovsky | System and method for performing handovers, or key management while performing handovers in a wireless communication system |
| US8179860B2 (en) * | 2008-02-15 | 2012-05-15 | Alcatel Lucent | Systems and method for performing handovers, or key management while performing handovers in a wireless communication system |
| DK2266334T3 (en) * | 2008-04-04 | 2019-04-08 | Nokia Technologies Oy | PROCEDURES, DEVICES AND COMPUTER PROGRAM PRODUCTS TO PROVIDE MULTI-HOP CRYPTOGRAPHY OPERATION FOR HANDLES |
| US9344924B2 (en) * | 2008-11-27 | 2016-05-17 | Htc Corporation | Method of handling handover security configuration and related communication device |
| US20100172500A1 (en) * | 2009-01-05 | 2010-07-08 | Chih-Hsiang Wu | Method of handling inter-system handover security in wireless communications system and related communication device |
| US9002357B2 (en) * | 2009-06-26 | 2015-04-07 | Qualcomm Incorporated | Systems, apparatus and methods to facilitate handover security |
-
2008
- 2008-10-22 JP JP2008272517A patent/JP4435254B1/ja active Active
-
2009
- 2009-10-22 BR BRPI0919721A patent/BRPI0919721A2/pt not_active IP Right Cessation
- 2009-10-22 WO PCT/JP2009/068176 patent/WO2010047367A1/ja not_active Ceased
- 2009-10-22 EP EP09822064A patent/EP2268070B1/en active Active
- 2009-10-22 CN CN2009801164735A patent/CN102017680B/zh active Active
- 2009-10-22 CA CA2725474A patent/CA2725474C/en not_active Expired - Fee Related
- 2009-10-22 US US12/989,801 patent/US8346261B2/en active Active
- 2009-10-22 AU AU2009307353A patent/AU2009307353B2/en not_active Ceased
- 2009-10-22 KR KR1020107024039A patent/KR101039345B1/ko not_active Expired - Fee Related
- 2009-10-22 MX MX2010012135A patent/MX2010012135A/es active IP Right Grant
- 2009-10-22 RU RU2010144010/08A patent/RU2450482C1/ru not_active IP Right Cessation
Patent Citations (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2003516000A (ja) * | 1999-11-23 | 2003-05-07 | ノキア コーポレイション | 移動ターミナルハンドオーバー中のセキュリティ関連性の転送 |
| JP2007515827A (ja) * | 2003-09-12 | 2007-06-14 | 株式会社エヌ・ティ・ティ・ドコモ | 異種ネットワークにおけるシームレスハンドオーバ |
| JP2006332788A (ja) * | 2005-05-23 | 2006-12-07 | Toshiba Corp | 基地局装置、無線通信システム、基地局制御プログラムおよび基地局制御方法 |
Non-Patent Citations (1)
| Title |
|---|
| See also references of EP2268070A4 * |
Cited By (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| WO2011140695A1 (en) | 2010-05-10 | 2011-11-17 | Nokia Corporation | Key derivation during inter-network handover |
| EP2569964A4 (en) * | 2010-05-10 | 2015-08-12 | Nokia Technologies Oy | KEY REMOVAL DURING A TRANSFER BETWEEN NETWORKS |
| US9264957B2 (en) | 2010-05-10 | 2016-02-16 | Nokia Technologies Oy | Key derivation during inter-network handover |
Also Published As
| Publication number | Publication date |
|---|---|
| CN102017680B (zh) | 2013-09-25 |
| MX2010012135A (es) | 2010-12-06 |
| KR20100131502A (ko) | 2010-12-15 |
| RU2450482C1 (ru) | 2012-05-10 |
| EP2268070B1 (en) | 2013-01-16 |
| EP2268070A4 (en) | 2011-05-18 |
| US8346261B2 (en) | 2013-01-01 |
| CA2725474C (en) | 2011-11-29 |
| KR101039345B1 (ko) | 2011-06-08 |
| US20110111731A1 (en) | 2011-05-12 |
| CN102017680A (zh) | 2011-04-13 |
| CA2725474A1 (en) | 2010-04-29 |
| AU2009307353B2 (en) | 2013-05-16 |
| BRPI0919721A2 (pt) | 2015-12-08 |
| AU2009307353A1 (en) | 2010-04-29 |
| JP4435254B1 (ja) | 2010-03-17 |
| JP2010103714A (ja) | 2010-05-06 |
| EP2268070A1 (en) | 2010-12-29 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| JP4435254B1 (ja) | 移動通信方法及び交換局 | |
| KR101045560B1 (ko) | 이동통신방법 | |
| JP4465015B2 (ja) | 移動通信方法 | |
| CN101399767B (zh) | 终端移动时安全能力协商的方法、系统及装置 | |
| US8331567B2 (en) | Methods and apparatuses for generating dynamic pairwise master keys using an image | |
| JP5038366B2 (ja) | 移動通信システム、移動局及び無線基地局 | |
| EP2282443A1 (en) | A cryptographic key generating method, device and system | |
| JP4394730B1 (ja) | 移動通信方法及び移動局 | |
| JP5164122B2 (ja) | 移動通信方法及び移動通信システム | |
| CN101588579A (zh) | 一种对用户设备鉴权的系统、方法及其基站子系统 | |
| KR101673827B1 (ko) | 단방향 키 전환 방법 및 구현 기기 | |
| JP2010104020A (ja) | 移動通信方法及び交換局 | |
| JP2010074801A (ja) | 移動通信方法 | |
| CN119109574B (zh) | 通信认证方法、装置、终端、网络设备、介质和程序产品 | |
| JP5559841B2 (ja) | 移動通信方法、リレーノード及び無線基地局 | |
| JP2011041158A (ja) | 移動通信方法、無線基地局及び移動局 | |
| JP2025171779A (ja) | 通信装置、通信方法及びコンピュータプログラム | |
| JP4653231B2 (ja) | 移動通信方法 | |
| JP2010011513A (ja) | 移動通信方法及び移動局 | |
| Baek et al. | FI-based local group key generation/distribution for mobile multicast in a hierarchical mobile IPv6 network. |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| WWE | Wipo information: entry into national phase |
Ref document number: 200980116473.5 Country of ref document: CN |
|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 09822064 Country of ref document: EP Kind code of ref document: A1 |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2009307353 Country of ref document: AU |
|
| ENP | Entry into the national phase |
Ref document number: 20107024039 Country of ref document: KR Kind code of ref document: A |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 4036/KOLNP/2010 Country of ref document: IN |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2725474 Country of ref document: CA |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 12010502481 Country of ref document: PH |
|
| WWE | Wipo information: entry into national phase |
Ref document number: MX/A/2010/012135 Country of ref document: MX |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2009822064 Country of ref document: EP |
|
| ENP | Entry into the national phase |
Ref document number: 2009307353 Country of ref document: AU Date of ref document: 20091022 Kind code of ref document: A |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 12989801 Country of ref document: US |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2010144010 Country of ref document: RU |
|
| ENP | Entry into the national phase |
Ref document number: PI0919721 Country of ref document: BR Kind code of ref document: A2 Effective date: 20110419 |