WO2012011264A1 - 無線lanシステムにおける無線lan通信端末およびその通信制御方法 - Google Patents
無線lanシステムにおける無線lan通信端末およびその通信制御方法 Download PDFInfo
- Publication number
- WO2012011264A1 WO2012011264A1 PCT/JP2011/004057 JP2011004057W WO2012011264A1 WO 2012011264 A1 WO2012011264 A1 WO 2012011264A1 JP 2011004057 W JP2011004057 W JP 2011004057W WO 2012011264 A1 WO2012011264 A1 WO 2012011264A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- terminal
- wireless lan
- access point
- security
- communication
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Images

Classifications
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L63/00—Network architectures or network communication protocols for network security
- H04L63/10—Network architectures or network communication protocols for network security for controlling access to devices or network resources
- H04L63/105—Multiple levels of security
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L63/00—Network architectures or network communication protocols for network security
- H04L63/20—Network architectures or network communication protocols for network security for managing network security; network security policies in general
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/02—Protecting privacy or anonymity, e.g. protecting personally identifiable information [PII]
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/03—Protecting confidentiality, e.g. by encryption
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/08—Access security
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W76/00—Connection management
- H04W76/10—Connection setup
- H04W76/14—Direct-mode setup
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W84/00—Network topologies
- H04W84/02—Hierarchically pre-organised networks, e.g. paging networks, cellular networks, WLAN [Wireless Local Area Network] or WLL [Wireless Local Loop]
- H04W84/10—Small scale networks; Flat hierarchical networks
- H04W84/12—WLAN [Wireless Local Area Networks]
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W84/00—Network topologies
- H04W84/02—Hierarchically pre-organised networks, e.g. paging networks, cellular networks, WLAN [Wireless Local Area Network] or WLL [Wireless Local Loop]
- H04W84/04—Large scale networks; Deep hierarchical networks
- H04W84/042—Public Land Mobile systems, e.g. cellular systems
- H04W84/047—Public Land Mobile systems, e.g. cellular systems using dedicated repeater stations
Definitions
- the present invention relates to a wireless LAN (local area network) system, and more particularly to a wireless LAN communication terminal and a communication control method thereof.
- a wireless LAN local area network
- TKIP Temporal Key Integrity Protocol
- WEP Wired Equivalent Privacy
- AES Advanced Encryption Standard
- security setting information associated with each access point is stored in a server, and when a wireless LAN communication terminal is wirelessly connected to one access point, the access point A corresponding security level is set in the wireless LAN communication terminal.
- the wireless LAN communication terminal when communicating via an access point, can set security between the own terminal and the access point.
- the security level between the access point and the partner terminal cannot be set by the own terminal. Therefore, even if the partner terminal can set the same level of security as its own terminal, if such a security level is not set on the partner side, it communicates with the partner terminal with the desired strength of security. I can't.
- the security setting between the partner terminal and the access point is determined when the partner terminal belongs to the access point. Therefore, when communication with the partner terminal is started after this attribution is completed, the terminal itself cannot know the security setting contents of the partner terminal.
- the own terminal is directly connected to the other terminal, it is possible to set security directly.
- the terminal itself operates as an access point, and network control becomes more complicated than when the terminal is simply connected to an existing access point, resulting in a new problem of increased power consumption.
- an object of the present invention is to provide a wireless LAN communication terminal and its communication control method that enable desired security settings with a counterpart terminal without increasing the power consumption of the terminal.
- a wireless LAN communication terminal is a wireless LAN communication terminal in a wireless LAN (local area network) system having at least one access point, and a wireless LAN communication terminal (hereinafter referred to as a partner terminal) serving as a communication partner.
- acquisition means for acquiring security function information of the counterpart terminal and current connection information of the access point from the counterpart terminal, the security function information of the counterpart terminal, and the connection Selection means for comparing information with the security policy of the terminal and selecting either direct connection with the counterpart terminal or relay connection through the access point so as to satisfy the security policy based on the comparison result And using the selected connection, the phase And having a communication means for communicating with the terminal.
- a communication control method is a communication control method for a wireless LAN communication terminal in a wireless LAN (local area network) system having at least one access point, and the acquisition means is a wireless LAN communication terminal (hereinafter referred to as a communication partner). And the other terminal) are connected to the access point, the security function information of the partner terminal and the current connection information with the access point are acquired from the partner terminal, and the selection means is the partner terminal.
- the security function information and the connection information of the terminal are compared with the security policy of the own terminal, and the direct connection with the counterpart terminal or the relay connection through the access point so as to satisfy the security policy based on the comparison result Any of the communication means is selected It communicates with the counterpart terminal using the connection, characterized in that.
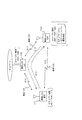
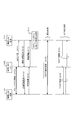
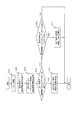
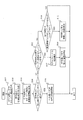
- FIG. 1 is a schematic system configuration diagram showing a schematic configuration and a communication control procedure of a wireless LAN system according to a first embodiment of the present invention. It is a sequence diagram which shows an example of the communication control procedure in the system shown in FIG. It is a flowchart which shows the communication control method of the wireless LAN communication terminal by 1st Example of this invention. It is a flowchart which shows the communication control method of the wireless LAN communication terminal by 2nd Example of this invention. It is a typical system block diagram which shows the schematic structure and communication control procedure of the wireless LAN system by 2nd Embodiment of this invention.
- FIG. 6 is a block diagram showing a schematic configuration of a wireless LAN communication terminal that can be used in the system shown in FIGS. 2 and 5.
- a simplified wireless LAN system will be exemplified to avoid complication of the description. Specifically, a case where a certain wireless LAN terminal starts communication with another wireless LAN terminal already belonging to one access point (AP) will be described as an example.
- AP access point
- the present invention is not limited to this, and the present invention can be applied to a system in which a plurality of access points can communicate through a network as long as direct communication between terminals is possible.
- security functions having different strengths WEP, TKIP, and AES described above are used as examples, but are not limited thereto.
- a wireless LAN terminal 101 is connected to a wireless LAN access point 102, and this wireless LAN terminal 101 is connected. Assume that the wireless LAN terminal 103 starts communication.
- the wireless LAN terminal 101 has security functions WEP / TKIP / AES with different security levels
- the access point 102 has security functions WEP / TKIP
- the wireless LAN terminal 103 has security functions WEP / TKIP / AES. It is assumed that Assume that the security level increases in the order of WEP ⁇ TKIP ⁇ AES, and the connection 104 between the wireless LAN terminal 101 and the access point 102 is set by the security function WEP.
- the wireless LAN terminal 103 is preset with a predetermined security level (for example, TKIP or higher) and a priority of use security as security policies.
- a predetermined security level for example, TKIP or higher
- a priority of use security as security policies.
- the predetermined security communication using TKIP or AES is set, and when priority is given, for example, if both TKIP and AES are available, a higher (or lower) security function is used.
- TKIP TKIP or higher
- AES is preferentially used instead of TKIP.
- the connection 104 between the wireless LAN terminal 101 and the access point 102 is set by WEP (step S10).
- the wireless LAN terminal 103 When attempting to start communication with the wireless LAN terminal 101, the wireless LAN terminal 103 first belongs to the access point 102 (step S11). Subsequently, the wireless LAN terminal 103 requests connection information including the security function and the current connection setting from the wireless LAN terminal 101 via the access point 102 (step S12).
- connection information request the wireless LAN terminal 101 returns the requested connection information to the wireless LAN terminal 103 via the access point 102 (step S13).
- the connection information includes security function information (in this case, WEP / TKIP / AES) installed in the terminal and current connection setting information (in this case, using WEP) with the access point 102.
- the wireless LAN terminal 103 compares the security function information and current connection setting information received from the wireless LAN terminal 101 with the security policy of its own terminal, and relays via the access point 102 when directly connecting to the wireless LAN terminal 101. It is determined which of the connection cases satisfies the required security level, and a connection that matches the security policy is selected (step S14).
- the security policy is set to preferentially select AES having a higher security level from TKIP or AES, and the security function information of the wireless LAN terminal 101 is WEP / TKIP / AES, the current connection with the access point 102 Since the setting is WEP, in order to satisfy the security policy, the direct connection is selected, and AES is used for the connection 106 with the wireless LAN terminal 101 (step S15).
- connection 104 between the wireless LAN terminal 101 and the access point 102 is set by, for example, TKIP in step S10, the current connection 104 satisfies the security policy, so the wireless LAN terminal 103 passes the connections 105 and 104. That is, the relay connection through the access point 102 is selected.
- the existing connection information with the access point when a certain wireless LAN terminal tries to connect to another wireless LAN terminal connected to the access point, the existing connection information with the access point.
- the connection method Specifically, the security information between the partner terminal and the access point and the security function of the partner terminal are acquired, the security level via the access point (AP relay connection), and when operating as an access point by itself (direct connection)
- the security level is compared with the security policy of the terminal itself.
- connection setting at a necessary level can be made from the settable security levels. Thereby, it is possible to select an optimum connection method from the viewpoint of power saving while ensuring a necessary security level.
- the wireless LAN terminal according to the present embodiment corresponds to the wireless LAN terminal 103 in FIG. 1, and includes a wireless communication unit for performing direct wireless communication with the access point 102 or the wireless LAN terminal 101 as a communication partner, It is assumed that a control unit or a program control processor for executing the communication control described in (1) is provided (details will be described later with reference to FIG. 6).
- the control unit of the wireless LAN terminal 103 when the control unit of the wireless LAN terminal 103 tries to start communication with the wireless LAN terminal 101 (hereinafter referred to as a partner terminal) as a communication partner, it first belongs to the access point 102 (step 201). Subsequently, the control unit transmits a request for connection information including the security function information and the current connection setting information to the partner terminal 101 through the wireless communication unit (step 202). Current connection setting information is acquired (step 203).
- the control unit determines whether or not the security level of the connection 104 satisfies the security policy of the own terminal from the current connection setting information of the counterpart terminal 101 (step 204). If the current connection 104 of the partner terminal 101 has a security level that satisfies the security policy of the own terminal (step 204: YES), the current connection 104 via the access point 102 satisfies the security policy, so the control unit Selects a relay connection via the access point 102, establishes a connection 106 with the access point 102, and starts communication with the partner terminal (step 205).
- the control unit connects directly to the partner terminal 101 from the security function information of the partner terminal 101. Whether communication satisfying the security policy is possible is determined (step 206). In other words, it is determined from the security function information installed in the counterpart terminal 101 whether or not it is possible to directly increase the security with the counterpart terminal 101 to a level that satisfies the security policy.
- the counterpart terminal 101 is connected to the access point 102 by WEP via the connection 104, but the security function corresponds to WEP / TKIP / AES.
- the wireless LAN terminal 103 establishes the connection 106 and starts direct communication with the counterpart terminal 101 using AES (step 207).
- the wireless LAN terminal 103 requests the counterpart terminal 101 to operate as an access point, and uses AES that is a necessary security level. It is also possible to establish an established connection.
- the access point 102 when the security level between the counterpart terminal 101 and the access point 102 satisfies the level required by the own terminal 103, the access point 102 is used. By communicating with the counterpart terminal 101, the own terminal does not need to operate as an access point. If the security level between the counterpart terminal 101 and the access point 102 is less than the level required by the own terminal 103, the security level can be ensured by directly communicating with the counterpart terminal 101.
- the wireless LAN terminal according to the present embodiment corresponds to the wireless LAN terminal 103 in FIG. 1, and includes a wireless communication unit for performing direct wireless communication with the access point 102 or the wireless LAN terminal 101 as a communication partner, It is assumed that a control unit or a program control processor for executing the communication control described in (1) is provided (details will be described later with reference to FIG. 6).
- the security priority of the wireless LAN terminal 103 is not particularly defined, and it is only necessary to be able to communicate with either AES or TKIP.
- control unit of the wireless LAN terminal 103 when the control unit of the wireless LAN terminal 103 tries to start communication with the counterpart terminal 101, it first belongs to the access point 102, and at that time the security function of the access point 102 (here, WEP / TKIP) is assigned. Obtain (step 301). Subsequently, the control unit transmits a request for connection information including the security function information and the current connection setting information to the partner terminal 101 through the wireless communication unit (step 302). Connection setting information is acquired (step 303).
- the control unit determines whether or not the security level of the connection 104 satisfies the security policy of the own terminal from the current connection setting information of the counterpart terminal 101 (step 304). If the current connection 104 of the partner terminal 101 has a security level that satisfies the security policy of the own terminal (step 304: YES), the current connection 104 via the access point 102 satisfies the security policy, so the control unit Selects a relay connection via the access point 102, establishes a connection 106 with the access point 102, and starts communication with the counterpart terminal 101 (step 305).
- step 304 if the current connection 104 of the partner terminal 101 does not satisfy the security policy of the own terminal (step 304: NO), the control unit satisfies the security policy by raising the security level of the connections 104 and 105. It is determined whether or not it is possible (step 306). If possible (step 306: YES), the control unit requests the partner terminal 101 to connect to the access point 102 with high security (step 307), and accesses the current connection 104 in a state satisfying the security policy. A relay connection via the point 102 is selected, a connection 106 is established with the access point 102, and communication with the counterpart terminal 101 is started (step 308).
- step 306 it is determined from the security function information of the partner terminal 101 whether communication satisfying the security policy is possible when the partner terminal 101 is directly connected. (Step 309). In other words, it is determined from the security function information installed in the counterpart terminal 101 whether or not it is possible to directly increase the security with the counterpart terminal 101 to a level that satisfies the security policy.
- the counterpart terminal 101 is connected to the access point 102 by WEP via the connection 104, but the security function corresponds to WEP / TKIP / AES. Therefore, it is possible to establish a connection using AES when the wireless LAN terminal 103 itself becomes an access point and directly connects to the counterpart terminal 101.
- the control unit of the wireless LAN terminal 103 establishes connection 106 using AES and starts direct communication with the counterpart terminal 101 (step 310).
- the counterpart terminal 101 has a function of operating as an access point
- the wireless LAN terminal 103 requests the counterpart terminal 101 to operate as an access point, and establishes a connection using the necessary security level AES. It is also possible to establish.
- Second Embodiment In the first embodiment, information related to the security of the counterpart terminal 101 is obtained via an access point.
- the present invention is not limited to this, and according to the second embodiment of the present invention, wireless It is also possible to obtain similar connection information by communication means other than the LAN.
- the wireless LAN terminals 401 and 402 have a communication function 403 different from the communication function of the wireless LAN, and can communicate with each other.
- a short-range wireless communication function NFC Near Field Communication
- a method is also conceivable in which information is obtained by displaying a two-dimensional barcode or the like on the screen of the counterpart terminal 401 and photographing it with the camera of the own terminal 402.
- WEP is used for the connection 104 between the counterpart terminal 401 and the access point 102 (step S10).
- the own terminal 402 When the own terminal 402 tries to start communication with the counterpart terminal 401, it transmits a request for connection information using NFC or the like (step 21), and the counterpart terminal 401 returns connection information in response thereto (step 21). Step S22). In this way, the own terminal 402 can acquire the security function information of the counterpart terminal 401 and the current connection setting information.
- the own terminal 402 compares the security function information and the current connection setting information received from the partner terminal 401 with the security policy of the own terminal, and connects directly to the partner terminal 401 and connects via the access point 102. Which of the security levels satisfies the required security level is selected, and a connection that matches the security policy is selected (step S23a or S23b).
- necessary information is acquired from the counterpart terminal 401 using information acquisition means other than the wireless LAN.
- the security level between the partner terminal 401 and the access point 102 is less than the level required by the own terminal 402
- the security level is ensured by directly communicating with the partner terminal 401 as described above. Can do. In this way, it is possible to confirm the necessity of direct communication by confirming the status of the existing connection between the partner terminal 401 and the access point 102, and performing communication at a necessary security level with power saving. Is possible.
- Wireless LAN Terminal A configuration example of a wireless LAN terminal that can implement the above-described embodiment will be described below with reference to FIG.
- the wireless LAN terminal is provided with a wireless communication unit 501 and a communication control unit 502 for wireless LAN communication. Further, the security function information and the current connection setting information from the counterpart terminal 101 described above.
- a connection information acquisition unit 503 having a function for acquiring the connection information is provided.
- a program control processor 504 such as a CPU (Central Processing Unit) controls the communication control unit 502, the connection information acquisition unit 503, and the security information storage unit 505 as shown in FIG. 3 or FIG.
- the security information storage unit 505 the above-described security policy is registered in advance, and the comparison result is obtained by comparing the security function information and the current connection setting information of the counterpart terminal 101 acquired by the connection information acquisition unit 503.
- AP relay connection or direct connection can be selected as shown in FIG. 3 or FIG.
- Such a communication control function can be realized by executing a program stored in the program storage unit 506 on the program control processor 504.
- the security information storage unit 505 and the program storage unit 506 may be a single storage medium or may be detachably attached to the wireless LAN terminal.
- the short-range wireless communication unit 507 is connected to the connection information acquisition unit 503, and the security function is started from the partner terminal 101. Information and current connection setting information are obtained.
- the program control processor 504 selects the relay connection via the access point 102 by controlling the communication control unit 502, and accordingly, the communication control Unit 502 need not operate as an access point. Further, when the security level of the other party does not satisfy the level required by the security policy, the security level can be ensured by the own terminal or the other terminal operating as an access point and directly communicating with the other party. By confirming the existing connection status of the other party in this way, it is possible to confirm the necessity of direct communication, and it is possible to perform communication at a required security level with power saving.
- the selection means selects the relay connection when the current connection information satisfies the security policy, and selects the security policy among the security functions of the counterpart terminal when the connection information does not satisfy the security policy.
- connection information does not satisfy the security policy
- the relay connection is selected using a security function of the access point and a security function of the counterpart terminal that satisfies the security policy.
- the wireless LAN communication terminal according to attachment 2.
- the communication means requests the local terminal to function as a wireless LAN access point or to request the counterpart terminal to function as a wireless LAN access point.
- the wireless LAN communication terminal according to any one of 1-3.
- a communication control method for a wireless LAN communication terminal in a wireless LAN (local area network) system having at least one access point When the acquisition unit is connected to a wireless LAN communication terminal (hereinafter referred to as a partner terminal) that is a communication partner with an access point, security function information of the partner terminal and current connection information with the access point are obtained. Obtained from the other terminal, The selection means compares the security function information and the connection information of the counterpart terminal with the security policy of the own terminal, and based on the comparison result, the direct connection with the counterpart terminal or the Select one of the relay connections via the access point, A communication means communicates with the counterpart terminal using the selected connection; A communication control method characterized by the above.
- the selection means selects the relay connection when the current connection information satisfies the security policy, and selects the security policy among the security functions of the counterpart terminal when the connection information does not satisfy the security policy.
- the communication means requests the local terminal to function as a wireless LAN access point or to request the counterpart terminal to function as a wireless LAN access point.
- the communication control method according to any one of 6-8.
- Appendix 10 Any one of appendix 6-9, wherein the acquisition unit acquires the security function information and the connection information of the counterpart terminal through the access point or through a communication unit different from the wireless LAN system.
- the communication control method according to item 1.
- a wireless LAN communication terminal as a communication partner (hereinafter referred to as a partner terminal) is connected to an access point, security function information of the partner terminal and current connection information with the access point are transmitted from the partner terminal.
- the security function information and the connection information of the counterpart terminal are compared with the security policy of the local terminal, and the direct connection with the counterpart terminal or via the access point so as to satisfy the security policy based on the comparison result.
- a wireless LAN system comprising:
- the selection means selects the relay connection when the current connection information satisfies the security policy, and selects the security policy among the security functions of the counterpart terminal when the connection information does not satisfy the security policy.
- connection information does not satisfy the security policy
- the relay connection is selected using a security function of the access point and a security function of the counterpart terminal that satisfies the security policy.
- the wireless LAN system according to attachment 12.
- the communication means requests the local terminal to function as a wireless LAN access point or to request the counterpart terminal to function as a wireless LAN access point.
- the wireless LAN system according to any one of 11-13.
- Appendix 15 Any one of appendices 11-14, wherein the acquisition means acquires the security function information and the connection information of the counterpart terminal through the access point or through communication means different from the wireless LAN system.
- the wireless LAN system according to item 1.
- a program for causing a program control processor of a wireless LAN communication terminal in a wireless LAN (local area network) system having at least one access point to function When a wireless LAN communication terminal as a communication partner (hereinafter referred to as a partner terminal) is connected to an access point, security function information of the partner terminal and current connection information with the access point are transmitted from the partner terminal.
- An acquisition function to acquire, The security function information and the connection information of the counterpart terminal are compared with the security policy of the local terminal, and the direct connection with the counterpart terminal or via the access point so as to satisfy the security policy based on the comparison result.
- a selection function to select one of the relay connections, A communication function for communicating with the counterpart terminal using the selected connection;
- the selection function selects the relay connection when the current connection information satisfies the security policy, and selects the security policy among the security functions of the counterpart terminal when the connection information does not satisfy the security policy.
- connection information does not satisfy the security policy
- the relay connection is selected using a security function of the access point and a security function of the counterpart terminal that satisfies the security policy.
- the communication means requests the local terminal to function as a wireless LAN access point or to request the counterpart terminal to function as a wireless LAN access point.
- the program according to any one of 16-18.
- Appendix 20 Any one of appendix 16-19, wherein the acquisition unit acquires the security function information and the connection information of the counterpart terminal through the access point or through a communication unit different from the wireless LAN system.
- the present invention can be provided for a wireless LAN terminal, particularly a system that uses a wireless LAN as a short-range communication method.
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Computer Hardware Design (AREA)
- Computing Systems (AREA)
- General Engineering & Computer Science (AREA)
- Mobile Radio Communication Systems (AREA)
Abstract
端末の消費電力を増加させることなく、相手端末との間で所望のセキュリティ設定を可能にする無線LAN通信端末およびその通信制御方法を提供する。アクセスポイント(102)を有する無線LANシステムにおける無線LAN通信端末(103)が、相手端末(101)がアクセスポイント102と接続されている場合、相手端末が有するセキュリティ機能情報とアクセスポイントとの現在の接続情報とを相手端末から取得し、相手端末のセキュリティ機能情報および接続情報と、自端末のセキュリティポリシとを比較し、比較結果に基づいて当該セキュリティポリシを満たすように相手端末との直接接続(106)あるいはアクセスポイントを介した中継接続(105,104)のいずれかを選択しと、選択された接続を用いて相手端末との通信を行う。
Description
本発明は無線LAN(ローカルエリアネットワーク)システムに係り、特に無線LAN通信端末およびその通信制御方法に関する。
無線LANでは、電波によりデータの送受信を行うことからセキュリティ強化が常に課題となっており、いくつかのセキュリティ規格が実際に採用されている。たとえばTKIP(Temporal Key Integrity Protocol)は、それまで使用されてきたWEP(Wired Equivalent Privacy)の脆弱性を克服する暗号化方式であり、AES(Advanced Encryption Standard)はさらに強固な暗号化アルゴリズムを採用した標準規格である。一般に、無線LANのアクセスポイント経由で通信を行う場合、無線通信端末はアクセスポイントとの間のセキュリティを自局でサポートされているセキュリティ機能を用いて設定することができる。
しかしながら、このようなセキュリティ機能を備えた無線LAN端末であっても、常に同じセキュリティレベルが要求されるわけではない。たとえば、社外の無線LAN環境で使用する場合には高いセキュリティレベルの設定が必要であり、社内の無線LANでは低いセキュリティレベルでもよい。そこで、使用場所や環境に応じてセキュリティ設定を変更できる無線LANシステムが提案されている。
たとえば特許文献1に開示された無線LAN通信装置では、サーバにアクセスポイントごとに対応づけたセキュリティ設定情報を記憶しておき、無線LAN通信端末が1つのアクセスポイントに無線接続すると、当該アクセスポイントに対応したセキュリティレベルが無線LAN通信端末に設定される。
上述したように、アクセスポイント経由で通信を行う場合、無線LAN通信端末は、自端末とアクセスポイントとの間のセキュリティを設定することが可能である。しかしながら、アクセスポイントから相手端末までの間のセキュリティレベルを自端末で設定することはできない。そのため、相手端末が自端末と同等レベルのセキュリティを設定できる場合であっても、そのようなセキュリティレベルが相手側で設定されていなければ、希望する強度のセキュリティで当該相手端末と通信を行うことはできない。
さらに、相手端末とアクセスポイントとの間のセキュリティの設定は当該相手端末がアクセスポイントへ帰属した時に決定される。したがって、この帰属が完了した後で当該相手端末と通信を開始する場合、自端末は相手端末のセキュリティ設定内容を知ることができない。
これに対して、自端末が相手端末と直接接続すれば、セキュリティを直接設定することは可能である。しかしながら、この場合、自端末がアクセスポイントとして動作することになり、単に端末として既存のアクセスポイントに接続した場合よりもネットワーク制御が複雑となり、消費電力が増加するという新たな課題が生じる。
そこで、本発明の目的は、端末の消費電力を増加させることなく、相手端末との間で所望のセキュリティ設定を可能にする無線LAN通信端末およびその通信制御方法を提供することにある。
本発明による無線LAN通信端末は、少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末であって、通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、前記選択された接続を用いて前記相手端末との通信を行う通信手段と、を有することを特徴とする。
本発明による通信制御方法は、少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末の通信制御方法であって、取得手段が、通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得し、選択手段が、前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択し、通信手段が前記選択された接続を用いて前記相手端末との通信を行う、ことを特徴とする。
本発明によれば、端末の消費電力を増加させることなく、相手端末との間で所望のセキュリティ設定が可能となる。
以下、説明の複雑化を避けるために、簡略化した無線LANシステムを例示する。具体的には、ある無線LAN端末が、1つのアクセスポイント(AP)に既に帰属している別の無線LAN端末に対して通信を開始する場合を一例として説明する。ただし、これに限定されるものではなく、複数のアクセスポイントがネットワークを通して通信可能なシステムであっても、端末間の直接通信が可能である限り、本発明は適用可能である。また、強度が異なるセキュリティ機能としては、既に述べたWEP、TKIPおよびAESを一例として使用するが、これらに限定されるものではない。
1.第1実施形態
1.1)システム
図1に示すように、本発明の第1実施形態による無線LANシステムは、無線LAN端末101が無線LANアクセスポイント102と接続されており、この無線LAN端末101に対して無線LAN端末103が通信を開始するものとする。
1.1)システム
図1に示すように、本発明の第1実施形態による無線LANシステムは、無線LAN端末101が無線LANアクセスポイント102と接続されており、この無線LAN端末101に対して無線LAN端末103が通信を開始するものとする。
無線LAN端末101にはセキュリティレベルが異なるセキュリティ機能WEP/TKIP/AESが搭載され、アクセスポイント102にはセキュリティ機能WEP/TKIPが搭載され、無線LAN端末103にはセキュリティ機能WEP/TKIP/AESが搭載されているものとする。セキュリティレベルはWEP<TKIP<AESの順で高くなり、無線LAN端末101とアクセスポイント102との接続104はセキュリティ機能WEPで設定されているものとする。
さらに、無線LAN端末103には、セキュリティポリシとして、所定セキュリティレベル(たとえばTKIP以上)および使用セキュリティの優先順位が予め設定されている。所定セキュリティとしては、TKIPあるいはAESを用いた通信が設定され、その際の優先順位は、たとえばTKIPとAESの両方が利用可能であれば、より高い(あるいはより低い)セキュリティ機能を利用するというように設定される。ここでは、より高い方のセキュリティレベルを選択するように設定され、TKIPではなくAESが優先的に利用されるものとする。
1.2)動作
次に、図1および図2を参照しながら、本実施形態の通信制御手順を説明する。
次に、図1および図2を参照しながら、本実施形態の通信制御手順を説明する。
まず、上述したように、無線LAN端末101とアクセスポイント102との接続104はWEPで設定されている(ステップS10)。無線LAN端末103は、無線LAN端末101との通信を開始しようとする際、まずアクセスポイント102に帰属する(ステップS11)。続いて、無線LAN端末103はアクセスポイント102経由で無線LAN端末101に対してセキュリティ機能および現在の接続設定を含む接続情報を要求する(ステップS12)。
無線LAN端末101は、この接続情報要求に応じて、要求された接続情報をアクセスポイント102経由で無線LAN端末103へ返信する(ステップS13)。接続情報は、自端末が搭載するセキュリティ機能情報(ここではWEP/TKIP/AES)と、アクセスポイント102との現在の接続設定情報(ここではWEP使用)とを含む。
無線LAN端末103は、無線LAN端末101から受信したセキュリティ機能情報および現在の接続設定情報と自端末のセキュリティポリシとを比較し、無線LAN端末101と直接接続する場合とアクセスポイント102を介して中継接続する場合のどちらが必要なセキュリティレベルを満たすかを判定し、セキュリティポリシに合致した接続を選択する(ステップS14)。ここでは、セキュリティポリシがTKIPあるいはAESのうちセキュリティレベルが高いAESを優先的に選択するように設定され、無線LAN端末101のセキュリティ機能情報がWEP/TKIP/AES、アクセスポイント102との現在の接続設定がWEPであるから、セキュリティポリシを満たすためには直接接続を選択して、無線LAN端末101との間の接続106にAESを利用する(ステップS15)。
もしステップS10において無線LAN端末101とアクセスポイント102との接続104がたとえばTKIPで設定されていれば、現在の接続104はセキュリティポリシを満たしているので、無線LAN端末103は接続105および104を通した、すなわちアクセスポイント102を通した中継接続を選択する。
1.3)効果
上述したように、本実施形態によれば、ある無線LAN端末がアクセスポイントに接続された別の無線LAN端末に対して接続しようとする際、アクセスポイントとの既存の接続情報を参照して接続方法を選択する。具体的には、相手端末とアクセスポイント間のセキュリティ情報および相手端末のセキュリティ機能を取得し、アクセスポイント経由(AP中継接続)でのセキュリティレベルと、自らアクセスポイントとして動作した場合(直接接続)のセキュリティレベルと、自端末のセキュリティポリシとを比較する。この比較結果から、AP中継接続と直接接続のいずれかを選択することで、設定可能なセキュリティレベルの中から必要なレベルでの接続設定が可能となる。これにより、必要なセキュリティレベルを確保しつつ、省電力という観点から最適な接続方法を選択することができる。
上述したように、本実施形態によれば、ある無線LAN端末がアクセスポイントに接続された別の無線LAN端末に対して接続しようとする際、アクセスポイントとの既存の接続情報を参照して接続方法を選択する。具体的には、相手端末とアクセスポイント間のセキュリティ情報および相手端末のセキュリティ機能を取得し、アクセスポイント経由(AP中継接続)でのセキュリティレベルと、自らアクセスポイントとして動作した場合(直接接続)のセキュリティレベルと、自端末のセキュリティポリシとを比較する。この比較結果から、AP中継接続と直接接続のいずれかを選択することで、設定可能なセキュリティレベルの中から必要なレベルでの接続設定が可能となる。これにより、必要なセキュリティレベルを確保しつつ、省電力という観点から最適な接続方法を選択することができる。
2.第1実施例
2.1)通信制御
次に、本発明の第1実施例による無線LAN端末の通信制御方法を図3を参照しながら詳細に説明する。なお、本実施例による無線LAN端末は図1における無線LAN端末103に対応するものであり、アクセスポイント102あるいは通信相手となる無線LAN端末101と直接無線通信を行うための無線通信部と、次に述べる通信制御を実行する制御部あるいはプログラム制御プロセッサとが設けられているものとする(詳細は、図6を参照しながら後で説明する。)。
2.1)通信制御
次に、本発明の第1実施例による無線LAN端末の通信制御方法を図3を参照しながら詳細に説明する。なお、本実施例による無線LAN端末は図1における無線LAN端末103に対応するものであり、アクセスポイント102あるいは通信相手となる無線LAN端末101と直接無線通信を行うための無線通信部と、次に述べる通信制御を実行する制御部あるいはプログラム制御プロセッサとが設けられているものとする(詳細は、図6を参照しながら後で説明する。)。
図3において、無線LAN端末103の制御部は、通信相手となる無線LAN端末101(以下相手端末という。)との通信を開始しようとする際、まずアクセスポイント102に帰属する(ステップ201)。続いて、制御部は相手端末101に対してセキュリティ機能情報および現在の接続設定情報を含む接続情報の要求を無線通信部を通して送信し(ステップ202)、その応答として相手端末101からセキュリティ機能情報と現在の接続設定情報とを取得する(ステップ203)。
続いて、制御部は、相手端末101の現在の接続設定情報から接続104のセキュリティレベルが自端末のセキュリティポリシを満たすか否かを判定する(ステップ204)。相手端末101の現在の接続104が自端末のセキュリティポリシを満たすセキュリティレベルを有するならば(ステップ204:YES)、アクセスポイント102を介した現在の接続104はセキュリティポリシを満たしているので、制御部はアクセスポイント102を介した中継接続を選択し、アクセスポイント102との間に接続106を確立し相手端末との通信を開始する(ステップ205)。
これに対して、相手端末101の現在の接続104が自端末のセキュリティポリシを満たさないならば(ステップ204:NO)、制御部は相手端末101のセキュリティ機能情報から相手端末101と直接接続した場合にセキュリティポリシを満たす通信が可能かどうかを判定する(ステップ206)。言い換えれば、相手端末101に搭載されたセキュリティ機能情報から、相手端末101との間のセキュリティをセキュリティポリシを満たすレベルまで直接上げることが可能かどうかを判断する。具体的には、相手端末101は、接続104を介してWEPでアクセスポイント102に接続されているが、セキュリティ機能としてはWEP/TKIP/AESに対応している。したがって、無線LAN端末103が自らアクセスポイントとなって相手端末101と直接接続することで、AESを用いた接続を確立することが可能である。よって、無線LAN端末103は接続106を確立し相手端末101とAESを用いて直接通信を開始する(ステップ207)。あるいは、相手端末101がアクセスポイントとして動作する機能を有している場合には、無線LAN端末103は、相手端末101へアクセスポイントとして動作するように要求し、必要なセキュリティレベルであるAESを用いた接続を確立することも可能である。
2.2)効果
以上説明したように、本実施例によれば、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルを満たす場合には、アクセスポイント102を介して相手端末101と通信を行うことで、自端末がアクセスポイントとして動作する必要がなくなる。また、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルに満たない場合には、相手端末101と直接通信することでセキュリティのレベルを確保することができる。
以上説明したように、本実施例によれば、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルを満たす場合には、アクセスポイント102を介して相手端末101と通信を行うことで、自端末がアクセスポイントとして動作する必要がなくなる。また、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルに満たない場合には、相手端末101と直接通信することでセキュリティのレベルを確保することができる。
このように相手端末101とアクセスポイント102との間の既存の接続の状況を確認することで、直接通信の必要性の有無を確認することができ、必要なセキュリティレベルの通信を省電力で行うことが可能となる。
3.第2実施例
3.1)通信制御
次に、本発明の第2実施例による無線LAN端末の通信制御方法を図4を参照しながら詳細に説明する。なお、本実施例による無線LAN端末は図1における無線LAN端末103に対応するものであり、アクセスポイント102あるいは通信相手となる無線LAN端末101と直接無線通信を行うための無線通信部と、次に述べる通信制御を実行する制御部あるいはプログラム制御プロセッサとが設けられているものとする(詳細は、図6を参照しながら後で説明する。)。また、本実施例においては、無線LAN端末103のセキュリティポリシでセキュリティの優先順位は特に定めず、AESかTKIPのいずれかで通信できればよいものとする。
3.1)通信制御
次に、本発明の第2実施例による無線LAN端末の通信制御方法を図4を参照しながら詳細に説明する。なお、本実施例による無線LAN端末は図1における無線LAN端末103に対応するものであり、アクセスポイント102あるいは通信相手となる無線LAN端末101と直接無線通信を行うための無線通信部と、次に述べる通信制御を実行する制御部あるいはプログラム制御プロセッサとが設けられているものとする(詳細は、図6を参照しながら後で説明する。)。また、本実施例においては、無線LAN端末103のセキュリティポリシでセキュリティの優先順位は特に定めず、AESかTKIPのいずれかで通信できればよいものとする。
図4において、無線LAN端末103の制御部は、相手端末101との通信を開始しようとする際、まずアクセスポイント102に帰属し、その時にアクセスポイント102のセキュリティ機能(ここではWEP/TKIP)を取得する(ステップ301)。続いて、制御部は相手端末101に対してセキュリティ機能情報および現在の接続設定情報を含む接続情報の要求を無線通信部を通して送信し(ステップ302)、その応答として相手端末からセキュリティ機能情報と現在の接続設定情報とを取得する(ステップ303)。
続いて、制御部は、相手端末101の現在の接続設定情報から接続104のセキュリティレベルが自端末のセキュリティポリシを満たすか否かを判定する(ステップ304)。相手端末101の現在の接続104が自端末のセキュリティポリシを満たすセキュリティレベルを有するならば(ステップ304:YES)、アクセスポイント102を介した現在の接続104はセキュリティポリシを満たしているので、制御部はアクセスポイント102を介した中継接続を選択し、アクセスポイント102との間に接続106を確立し相手端末101との通信を開始する(ステップ305)。
これに対して、相手端末101の現在の接続104が自端末のセキュリティポリシを満たさないならば(ステップ304:NO)、制御部は接続104および105のセキュリティレベルを上げることでセキュリティポリシを満たすことが可能かどうか判断する(ステップ306)。可能であれば(ステップ306:YES)、制御部は相手端末101に対して高いセキュリティでアクセスポイント102と接続するよう要求し(ステップ307)、現在の接続104をセキュリティポリシを満たす状態にしてアクセスポイント102を介した中継接続を選択し、アクセスポイント102との間に接続106を確立し相手端末101との通信を開始する(ステップ308)。
接続104および105のセキュリティレベルを上げることができない場合には(ステップ306:NO)、相手端末101のセキュリティ機能情報から相手端末101と直接接続した場合にセキュリティポリシを満たす通信が可能かどうかを判定する(ステップ309)。言い換えれば、相手端末101に搭載されたセキュリティ機能情報から、相手端末101との間でセキュリティをセキュリティポリシを満たすレベルまで直接上げることが可能かどうかを判断する。具体的には、相手端末101は、接続104を介してWEPでアクセスポイント102に接続されているが、セキュリティ機能としてはWEP/TKIP/AESに対応している。したがって、無線LAN端末103が自らアクセスポイントとなって相手端末101と直接接続することで、AESを用いた接続を確立することが可能である。よって、無線LAN端末103の制御部は、AESを利用した接続106を確立し相手端末101と直接通信を開始する(ステップ310)。あるいは、相手端末101がアクセスポイントとして動作する機能を持っていれば、無線LAN端末103は、相手端末101へアクセスポイントとして動作するように要求し、必要なセキュリティレベルであるAESを用いた接続を確立することも可能である。
3.2)効果
以上説明したように、本実施例によれば、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルに満たない場合、相手端末101と直接通信する前に、相手端末101とアクセスポイント102との間のセキュリティレベルの増加が可能かどうかを判定する。このセキュリティ増加が可能であれば、自端末103あるいは相手端末101がアクセスポイントとして動作する必要がなくなり、セキュリティポリシを満たす中継接続で端末間の通信が可能となる。これによって端末の消費電力がさらに抑制されうる。
以上説明したように、本実施例によれば、相手端末101とアクセスポイント102との間のセキュリティレベルが自端末103の要求するレベルに満たない場合、相手端末101と直接通信する前に、相手端末101とアクセスポイント102との間のセキュリティレベルの増加が可能かどうかを判定する。このセキュリティ増加が可能であれば、自端末103あるいは相手端末101がアクセスポイントとして動作する必要がなくなり、セキュリティポリシを満たす中継接続で端末間の通信が可能となる。これによって端末の消費電力がさらに抑制されうる。
4.第2実施形態
上記第1実施形態では、相手端末101のセキュリティに関する情報の入手をアクセスポイント経由で行ったが、これに限定されるものではなく、本発明の第2実施形態によれば、無線LAN以外の通信手段により同様の接続情報を入手することも可能である。
上記第1実施形態では、相手端末101のセキュリティに関する情報の入手をアクセスポイント経由で行ったが、これに限定されるものではなく、本発明の第2実施形態によれば、無線LAN以外の通信手段により同様の接続情報を入手することも可能である。
図5に示す本発明の第2実施形態による無線LANシステムにおいて、図1に示すシステムと同様の機能を有するブロックには同一の参照番号が付されている。無線LAN端末401および402は、無線LANの通信機能とは別の通信機能403を有し、相互に通信可能であるものとする。別の通信機能403としては、たとえば短距離無線通信機能NFC(Near Field Communication)などが利用できる。あるいは、相手端末401の画面に二次元バーコード等を表示し、自端末402のカメラでそれを撮影することで情報を入手するといった方法も考えられる。
上述したように、相手端末401とアクセスポイント102との接続104ではWEPが使用されている(ステップS10)。自端末402は、相手端末401との通信を開始しようとする際、NFC等を利用して接続情報の要求を送信し(ステップ21)、それに応答して相手端末401が接続情報を返信する(ステップS22)。こうして自端末402は、相手端末401のセキュリティ機能情報および現在の接続設定情報を取得することができる。
自端末402は、相手端末401から受信したセキュリティ機能情報および現在の接続設定情報と自端末のセキュリティポリシとを比較し、相手端末401と直接接続する場合とアクセスポイント102を介して中継接続する場合のどちらが必要なセキュリティレベルを満たすかを判定し、セキュリティポリシに合致した接続を選択する(ステップS23aあるいはS23b)。
以上説明したように、本実施形態によれば、無線LAN以外の情報取得手段を利用して相手端末401から必要な情報を取得する。相手端末401とアクセスポイント102との間のセキュリティレベルが自端末402の要求するレベルに満たない場合には、既に述べたように、相手端末401と直接通信することでセキュリティのレベルを確保することができる。このように相手端末401とアクセスポイント102との間の既存の接続の状況を確認することで直接通信の必要性の有無を確認することができ、必要なセキュリティレベルの通信を省電力で行うことが可能となる。
5.無線LAN端末
以下、図6を参照しながら、上述した実施例を実装可能な無線LAN端末の構成例を説明する。
以下、図6を参照しながら、上述した実施例を実装可能な無線LAN端末の構成例を説明する。
図6に示すように、無線LAN端末には、無線LAN通信のための無線通信部501および通信制御部502が設けられ、さらに、上述した相手端末101からのセキュリティ機能情報および現在の接続設定情報を取得する機能を実装した接続情報取得部503が設けられている。CPU(Central Processing Unit)等のプログラム制御プロセッサ504は、通信制御部502、接続情報取得部503およびセキュリティ情報格納部505を図3あるいは図4に示すように制御する。
セキュリティ情報格納部505には、上述したセキュリティポリシを予め登録しておき、接続情報取得部503により取得された相手端末101のセキュリティ機能情報および現在の接続設定情報と比較することで、その比較結果に応じて図3あるいは図4に示すようにAP中継接続あるいは直接接続のいずれかを選択することができる。このような通信制御機能は、プログラム格納部506に記憶されたプログラムをプログラム制御プロセッサ504上で実行することにより実現することができる。なお、セキュリティ情報格納部505およびプログラム格納部506は単体の記憶媒体であってもよく、無線LAN端末に着脱可能に取り付けられてもよい。
なお、第2実施形態で説明したように、短距離無線通信機能NFCを利用した無線LAN端末であれば、接続情報取得部503に短距離無線通信部507が接続され、相手端末101からセキュリティ機能情報および現在の接続設定情報が取得される。
上述したように、相手端末側のセキュリティレベルがセキュリティポリシが要求するレベルを満たせば、プログラム制御プロセッサ504は通信制御部502を制御してアクセスポイント102を介した中継接続を選択し、したがって通信制御部502はアクセスポイントとして動作する必要がなくなる。また、相手側のセキュリティレベルがセキュリティポリシが要求するレベルを満たさない場合には、自端末あるいは相手端末がアクセスポイントとして動作して相手と直接通信することでセキュリティのレベルを確保することができる。このように相手側の既存の接続状況を確認することで、直接通信の必要性の有無を確認することができ、必要なセキュリティレベルの通信を省電力で行うことが可能となる。
6.付記
上述した実施形態の一部あるいは全部は、以下の付記のようにも記載されうるが、これらに限定されるものではない。
上述した実施形態の一部あるいは全部は、以下の付記のようにも記載されうるが、これらに限定されるものではない。
(付記1)
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末であって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LAN通信端末。
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末であって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LAN通信端末。
(付記2)
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記1に記載の無線LAN通信端末。
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記1に記載の無線LAN通信端末。
(付記3)
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記2に記載の無線LAN通信端末。
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記2に記載の無線LAN通信端末。
(付記4)
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記1-3のいずれか1項に記載の無線LAN通信端末。
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記1-3のいずれか1項に記載の無線LAN通信端末。
(付記5)
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記1-4のいずれか1項に記載の無線LAN通信端末。
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記1-4のいずれか1項に記載の無線LAN通信端末。
(付記6)
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末の通信制御方法であって、
取得手段が、通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得し、
選択手段が、前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択し、
通信手段が前記選択された接続を用いて前記相手端末との通信を行う、
ことを特徴とする通信制御方法。
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末の通信制御方法であって、
取得手段が、通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得し、
選択手段が、前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択し、
通信手段が前記選択された接続を用いて前記相手端末との通信を行う、
ことを特徴とする通信制御方法。
(付記7)
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記6に記載の通信制御方法。
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記6に記載の通信制御方法。
(付記8)
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記7に記載の通信制御方法。
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記7に記載の通信制御方法。
(付記9)
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記6-8のいずれか1項に記載の通信制御方法。
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記6-8のいずれか1項に記載の通信制御方法。
(付記10)
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記6-9のいずれか1項に記載の通信制御方法。
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記6-9のいずれか1項に記載の通信制御方法。
(付記11)
少なくとも1つのアクセスポイントと複数の無線LAN通信端末とを有する無線LAN(ローカルエリアネットワーク)システムにおいて、
無線LAN通信端末が、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LANシステム。
少なくとも1つのアクセスポイントと複数の無線LAN通信端末とを有する無線LAN(ローカルエリアネットワーク)システムにおいて、
無線LAN通信端末が、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LANシステム。
(付記12)
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記11に記載の無線LANシステム。
前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記11に記載の無線LANシステム。
(付記13)
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記12に記載の無線LANシステム。
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記12に記載の無線LANシステム。
(付記14)
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記11-13のいずれか1項に記載の無線LANシステム。
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記11-13のいずれか1項に記載の無線LANシステム。
(付記15)
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記11-14のいずれか1項に記載の無線LANシステム。
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記11-14のいずれか1項に記載の無線LANシステム。
(付記16)
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末のプログラム制御プロセッサを機能させるプログラムであって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得機能と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択機能と、
前記選択された接続を用いて前記相手端末との通信を行う通信機能と、
を有する無線LAN通信端末として前記プログラム制御プロセッサを機能させるプログラム。
少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末のプログラム制御プロセッサを機能させるプログラムであって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得機能と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択機能と、
前記選択された接続を用いて前記相手端末との通信を行う通信機能と、
を有する無線LAN通信端末として前記プログラム制御プロセッサを機能させるプログラム。
(付記17)
前記選択機能は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記16に記載のプログラム。
前記選択機能は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする付記16に記載のプログラム。
(付記18)
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記17に記載のプログラム。
前記接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする付記17に記載のプログラム。
(付記19)
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記16-18のいずれか1項に記載のプログラム。
前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする付記16-18のいずれか1項に記載のプログラム。
(付記20)
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記16-19のいずれか1項に記載のプログラム。
前記取得手段は、前記アクセスポイントを通して、あるいは前記無線LANシステムとは別の通信手段を通して、前記相手端末の前記セキュリティ機能情報および前記接続情報を取得することを特徴とする付記16-19のいずれか1項に記載のプログラム。
本発明は、無線LAN端末、特に無線LANを近距離通信方式として利用するシステムに提供可能である。
101、103、401、402 無線LAN端末
102 アクセスポイント
104,105,106 接続
501 無線通信部
502 通信制御部
503 接続情報取得部
504 プログラム制御プロセッサ
505 セキュリティ情報格納部
506 プログラム格納部
102 アクセスポイント
104,105,106 接続
501 無線通信部
502 通信制御部
503 接続情報取得部
504 プログラム制御プロセッサ
505 セキュリティ情報格納部
506 プログラム格納部
Claims (10)
- 少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末であって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LAN通信端末。 - 前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記現在の接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする請求項1に記載の無線LAN通信端末。
- 前記現在の接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする請求項2に記載の無線LAN通信端末。
- 前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする請求項1-3のいずれか1項に記載の無線LAN通信端末。
- 少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末の通信制御方法であって、
取得手段が、通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得し、
選択手段が、前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択し、
通信手段が前記選択された接続を用いて前記相手端末との通信を行う、
ことを特徴とする通信制御方法。 - 前記選択手段は、前記現在の接続情報が前記セキュリティポリシを満たす場合には前記中継接続を選択し、前記現在の接続情報が前記セキュリティポリシを満たさない場合には前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記直接接続あるいは前記中継接続を選択することを特徴とする請求項5に記載の通信制御方法。
- 前記現在の接続情報が前記セキュリティポリシを満たさない場合には、前記アクセスポイントのセキュリティ機能および前記相手端末のセキュリティ機能のうち前記セキュリティポリシを満たすものを利用して前記中継接続を選択することを特徴とする請求項6に記載の通信制御方法。
- 前記通信手段は、前記直接接続の場合には、自端末を無線LANのアクセスポイントとして機能させるか、あるいは前記相手端末を無線LANのアクセスポイントとして機能させるように要求する、ことを特徴とする請求項5-7のいずれか1項に記載の通信制御方法。
- 少なくとも1つのアクセスポイントと複数の無線LAN通信端末とを有する無線LAN(ローカルエリアネットワーク)システムにおいて、
無線LAN通信端末が、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得手段と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択手段と、
前記選択された接続を用いて前記相手端末との通信を行う通信手段と、
を有することを特徴とする無線LANシステム。 - 少なくとも1つのアクセスポイントを有する無線LAN(ローカルエリアネットワーク)システムにおける無線LAN通信端末のプログラム制御プロセッサを機能させるプログラムであって、
通信相手となる無線LAN通信端末(以下、相手端末という。)がアクセスポイントと接続されている場合、前記相手端末が有するセキュリティ機能情報と前記アクセスポイントとの現在の接続情報とを前記相手端末から取得する取得機能と、
前記相手端末の前記セキュリティ機能情報および前記接続情報と、自端末のセキュリティポリシとを比較し、前記比較結果に基づいて当該セキュリティポリシを満たすように前記相手端末との直接接続あるいは前記アクセスポイントを介した中継接続のいずれかを選択する選択機能と、
前記選択された接続を用いて前記相手端末との通信を行う通信機能と、
を有する無線LAN通信端末として前記プログラム制御プロセッサを機能させるプログラム。
Priority Applications (4)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2012525321A JP5894075B2 (ja) | 2010-07-21 | 2011-07-15 | 無線lanシステムにおける無線lan通信端末およびその通信制御方法 |
| US13/810,820 US8997175B2 (en) | 2010-07-21 | 2011-07-15 | Wireless LAN communication terminal and communication control method thereof in wireless LAN system for the same |
| EP11809440.8A EP2597901A4 (en) | 2010-07-21 | 2011-07-15 | Wireless lan communication terminal in wireless lan system, and communication control method for wireless lan communication terminal |
| CN201180035479.7A CN103004245B (zh) | 2010-07-21 | 2011-07-15 | 无线lan系统中的无线lan通信终端及其通信控制方法 |
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2010-163597 | 2010-07-21 | ||
| JP2010163597 | 2010-07-21 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2012011264A1 true WO2012011264A1 (ja) | 2012-01-26 |
Family
ID=45496697
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/JP2011/004057 Ceased WO2012011264A1 (ja) | 2010-07-21 | 2011-07-15 | 無線lanシステムにおける無線lan通信端末およびその通信制御方法 |
Country Status (5)
| Country | Link |
|---|---|
| US (1) | US8997175B2 (ja) |
| EP (1) | EP2597901A4 (ja) |
| JP (2) | JP5894075B2 (ja) |
| CN (1) | CN103004245B (ja) |
| WO (1) | WO2012011264A1 (ja) |
Cited By (5)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2013225824A (ja) * | 2012-04-23 | 2013-10-31 | Toshiba Corp | 電子機器、無線接続制御方法、無線接続制御プログラム |
| WO2013185705A1 (zh) * | 2013-01-16 | 2013-12-19 | 中兴通讯股份有限公司 | 一种终端自动建立无线连接的方法和终端 |
| WO2014141980A1 (en) * | 2013-03-15 | 2014-09-18 | Canon Kabushiki Kaisha | Communication apparatus, method of controlling the same, program, and printing apparatus |
| JP2015156561A (ja) * | 2014-02-20 | 2015-08-27 | 株式会社バッファロー | 無線接続装置、無線接続装置の制御方法、無線接続装置と移動体通信端末とを備えるネットワークシステム、および、移動体通信端末が実行するコンピュータプログラム |
| JP2021158529A (ja) * | 2020-03-27 | 2021-10-07 | セイコーエプソン株式会社 | 電子機器、通信システム及び通信方法 |
Families Citing this family (7)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US9894108B2 (en) | 2010-12-13 | 2018-02-13 | At&T Intellectual Property I, L.P. | Synchronization based on device presence |
| EP3117681A4 (en) * | 2014-03-13 | 2017-01-18 | Telefonaktiebolaget LM Ericsson (publ) | Establishment of secure connections between radio access nodes of a wireless network |
| US10063439B2 (en) * | 2014-09-09 | 2018-08-28 | Belkin International Inc. | Coordinated and device-distributed detection of abnormal network device operation |
| JP6789628B2 (ja) * | 2015-12-18 | 2020-11-25 | キヤノン株式会社 | 通信装置、制御方法、および、プログラム |
| US10757105B2 (en) * | 2017-06-12 | 2020-08-25 | At&T Intellectual Property I, L.P. | On-demand network security system |
| CN111935851A (zh) * | 2020-07-17 | 2020-11-13 | 广东以诺通讯有限公司 | 通信方法、WiFi接入点和D2D终端 |
| CN112040477A (zh) * | 2020-08-19 | 2020-12-04 | 广东以诺通讯有限公司 | 一种d2d安全直连通信方法及终端 |
Citations (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2008035371A (ja) * | 2006-07-31 | 2008-02-14 | Canon Inc | 通信装置、通信装置の制御方法、及び当該制御方法をコンピュータに実行させるためのコンピュータプログラム |
| JP2008219750A (ja) | 2007-03-07 | 2008-09-18 | Oki Electric Ind Co Ltd | 無線lan通信装置 |
| JP2008219358A (ja) * | 2007-03-02 | 2008-09-18 | Sony Corp | 無線通信システム、無線通信装置及び無線通信方法、並びにコンピュータ・プログラム |
| JP2009500969A (ja) * | 2005-07-08 | 2009-01-08 | マイクロソフト コーポレーション | 直接ワイヤレス・クライアント間通信 |
| JP2009212732A (ja) * | 2008-03-03 | 2009-09-17 | Sony Corp | 通信装置、及び通信方法 |
| JP2009219051A (ja) * | 2008-03-12 | 2009-09-24 | Canon Inc | 通信システム、通信方法、端末及び管理装置 |
Family Cites Families (14)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US5841854A (en) * | 1994-02-16 | 1998-11-24 | Priority Call Management, Inc. | Wireless telephone integration system and method for call centers and workgroups |
| US6795444B1 (en) * | 1999-10-26 | 2004-09-21 | Telefonaktiebolaget L M Ericsson (Publ) | System and method for providing wireless telephony over a packet-switched network |
| US20030026229A1 (en) * | 2001-07-26 | 2003-02-06 | Dave Larson | Virtual data trunks between switching points using an IP network |
| JP2003143289A (ja) * | 2001-11-07 | 2003-05-16 | Hitachi Ltd | 情報端末およびその通信方法 |
| JP4032257B2 (ja) * | 2004-06-28 | 2008-01-16 | 日本電気株式会社 | 無線lanにおける省電力化方法、基地局、端末局、無線lanシステム |
| JP2006093945A (ja) * | 2004-09-22 | 2006-04-06 | Nec Corp | 無線lanハンドオーバー方法、及び無線lan装置 |
| US20070150742A1 (en) * | 2005-12-22 | 2007-06-28 | Cukier Johnas I | Secure data communication for groups of mobile devices |
| US20080175379A1 (en) * | 2007-01-23 | 2008-07-24 | Broadcom Corporation | Simple pairing to generate private keys for different protocol communications |
| JP4475328B2 (ja) * | 2007-12-26 | 2010-06-09 | ソニー株式会社 | 無線通信システム、無線通信装置、無線通信方法、およびプログラム |
| JP4518183B2 (ja) * | 2008-04-28 | 2010-08-04 | ソニー株式会社 | 無線通信システム、無線通信装置、無線通信方法及びプログラム |
| US8401166B1 (en) * | 2008-05-20 | 2013-03-19 | Peerless Network, Inc. | Systems and methods of mitigating phantom call traffic |
| JP4609547B2 (ja) * | 2008-08-14 | 2011-01-12 | ソニー株式会社 | 無線通信装置、通信システム、および通信制御方法、並びにプログラム |
| US8095112B2 (en) * | 2008-08-21 | 2012-01-10 | Palo Alto Research Center Incorporated | Adjusting security level of mobile device based on presence or absence of other mobile devices nearby |
| US8495706B2 (en) * | 2010-10-21 | 2013-07-23 | Kabushiki Kaisha Toshiba | Television apparatus, display control device, and display control method |
-
2011
- 2011-07-15 EP EP11809440.8A patent/EP2597901A4/en not_active Withdrawn
- 2011-07-15 JP JP2012525321A patent/JP5894075B2/ja not_active Expired - Fee Related
- 2011-07-15 CN CN201180035479.7A patent/CN103004245B/zh active Active
- 2011-07-15 US US13/810,820 patent/US8997175B2/en active Active
- 2011-07-15 WO PCT/JP2011/004057 patent/WO2012011264A1/ja not_active Ceased
-
2016
- 2016-02-23 JP JP2016031766A patent/JP2016119711A/ja active Pending
Patent Citations (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2009500969A (ja) * | 2005-07-08 | 2009-01-08 | マイクロソフト コーポレーション | 直接ワイヤレス・クライアント間通信 |
| JP2008035371A (ja) * | 2006-07-31 | 2008-02-14 | Canon Inc | 通信装置、通信装置の制御方法、及び当該制御方法をコンピュータに実行させるためのコンピュータプログラム |
| JP2008219358A (ja) * | 2007-03-02 | 2008-09-18 | Sony Corp | 無線通信システム、無線通信装置及び無線通信方法、並びにコンピュータ・プログラム |
| JP2008219750A (ja) | 2007-03-07 | 2008-09-18 | Oki Electric Ind Co Ltd | 無線lan通信装置 |
| JP2009212732A (ja) * | 2008-03-03 | 2009-09-17 | Sony Corp | 通信装置、及び通信方法 |
| JP2009219051A (ja) * | 2008-03-12 | 2009-09-24 | Canon Inc | 通信システム、通信方法、端末及び管理装置 |
Non-Patent Citations (1)
| Title |
|---|
| See also references of EP2597901A4 * |
Cited By (12)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2013225824A (ja) * | 2012-04-23 | 2013-10-31 | Toshiba Corp | 電子機器、無線接続制御方法、無線接続制御プログラム |
| EP2658334A3 (en) * | 2012-04-23 | 2014-12-31 | Kabushiki Kaisha Toshiba | Wireless connection system, wireless connection control method, and wireless connection control program |
| WO2013185705A1 (zh) * | 2013-01-16 | 2013-12-19 | 中兴通讯股份有限公司 | 一种终端自动建立无线连接的方法和终端 |
| CN103929797A (zh) * | 2013-01-16 | 2014-07-16 | 中兴通讯股份有限公司 | 一种终端自动建立无线连接的方法和终端 |
| WO2014141980A1 (en) * | 2013-03-15 | 2014-09-18 | Canon Kabushiki Kaisha | Communication apparatus, method of controlling the same, program, and printing apparatus |
| US9628991B2 (en) | 2013-03-15 | 2017-04-18 | Canon Kabushiki Kaisha | Communication apparatus, method of controlling the same, program, and printing apparatus |
| US10477399B2 (en) | 2013-03-15 | 2019-11-12 | Canon Kabushiki Kaisha | Communication apparatus, method of controlling the same, program, and printing apparatus |
| US11019105B2 (en) | 2013-03-15 | 2021-05-25 | Canon Kabushiki Kaisha | Communication apparatus, method of controlling the same, program, and printing apparatus |
| JP2015156561A (ja) * | 2014-02-20 | 2015-08-27 | 株式会社バッファロー | 無線接続装置、無線接続装置の制御方法、無線接続装置と移動体通信端末とを備えるネットワークシステム、および、移動体通信端末が実行するコンピュータプログラム |
| JP2021158529A (ja) * | 2020-03-27 | 2021-10-07 | セイコーエプソン株式会社 | 電子機器、通信システム及び通信方法 |
| JP7443881B2 (ja) | 2020-03-27 | 2024-03-06 | セイコーエプソン株式会社 | 電子機器、通信システム及び通信方法 |
| US12015979B2 (en) | 2020-03-27 | 2024-06-18 | Seiko Epson Corporation | Electronic apparatus, communication system, and communication method |
Also Published As
| Publication number | Publication date |
|---|---|
| JP2016119711A (ja) | 2016-06-30 |
| CN103004245B (zh) | 2016-06-01 |
| US20130133029A1 (en) | 2013-05-23 |
| CN103004245A (zh) | 2013-03-27 |
| EP2597901A1 (en) | 2013-05-29 |
| US8997175B2 (en) | 2015-03-31 |
| JPWO2012011264A1 (ja) | 2013-09-09 |
| JP5894075B2 (ja) | 2016-03-23 |
| EP2597901A4 (en) | 2017-01-25 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| JP5894075B2 (ja) | 無線lanシステムにおける無線lan通信端末およびその通信制御方法 | |
| US10848946B2 (en) | Network access method, device, and system | |
| US9769732B2 (en) | Wireless network connection establishment method and terminal device | |
| CN102917438B (zh) | 接入点装置以及通信设定提供方法 | |
| US10278045B2 (en) | Function execution device and communication terminal | |
| KR101885500B1 (ko) | Wifi 설정 포팅 | |
| JP5421584B2 (ja) | 通信システムおよび通信方法 | |
| US20200304327A1 (en) | ROBUST EVENT HANDLING IN AN ELECTRONIC SUBSCRIBER IDENTITY MODULE (eSIM) NOTIFICATION SERVICE | |
| RU2437240C2 (ru) | Способ установления параметров связи, осуществляющее связь устройство, способ управления осуществляющим связь устройством и программа | |
| US20160242033A1 (en) | Communication service using method and electronic device supporting the same | |
| JP2005176021A (ja) | 情報処理装置およびプログラム | |
| US20140176981A1 (en) | Information Processing Apparatus, Method for Controlling the Same, and Computer Readable Medium for the Same | |
| US20090191847A1 (en) | System for setting security in wireless network system using cluster function and method of controlling the same | |
| WO2012065101A1 (en) | Context-based dynamic policy system for mobile devices and supporting network infrastructure | |
| US9277581B2 (en) | Communication apparatus, communication method, program and storage medium | |
| JP5436345B2 (ja) | 携帯端末を利用した無線lan設定方法およびシステム | |
| KR20140128764A (ko) | 연결 정보 제어 방법 및 그 전자 장치 | |
| JP2017539176A (ja) | デバイス構成のための方法およびデバイス | |
| EP3177097B1 (en) | Method for establishing network connection by means of wps, and mobile wi-fi device and computer storage medium | |
| JP2008263445A (ja) | 接続設定システム、認証装置、無線端末、及び接続設定方法 | |
| JP2009188765A (ja) | 無線端末及び無線通信方法 | |
| JP6394606B2 (ja) | 端末装置、端末装置制御方法および端末装置制御プログラム | |
| US10009290B2 (en) | Method and broadband device for modem dial-up | |
| KR20120024786A (ko) | 보안 네트워크 접속 | |
| JP6417539B2 (ja) | 情報処理装置 |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 11809440 Country of ref document: EP Kind code of ref document: A1 |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2011809440 Country of ref document: EP |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 2012525321 Country of ref document: JP |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 13810820 Country of ref document: US |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |