WO2018029893A1 - データ提供システム、データ保安装置、データ提供方法、及びコンピュータプログラム - Google Patents
データ提供システム、データ保安装置、データ提供方法、及びコンピュータプログラム Download PDFInfo
- Publication number
- WO2018029893A1 WO2018029893A1 PCT/JP2017/012720 JP2017012720W WO2018029893A1 WO 2018029893 A1 WO2018029893 A1 WO 2018029893A1 JP 2017012720 W JP2017012720 W JP 2017012720W WO 2018029893 A1 WO2018029893 A1 WO 2018029893A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- data
- vehicle
- security device
- ecu
- interface unit
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Images


Classifications
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F21/00—Security arrangements for protecting computers, components thereof, programs or data against unauthorised activity
- G06F21/50—Monitoring users, programs or devices to maintain the integrity of platforms, e.g. of processors, firmware or operating systems
- G06F21/57—Certifying or maintaining trusted computer platforms, e.g. secure boots or power-downs, version controls, system software checks, secure updates or assessing vulnerabilities
-
- B—PERFORMING OPERATIONS; TRANSPORTING
- B60—VEHICLES IN GENERAL
- B60R—VEHICLES, VEHICLE FITTINGS, OR VEHICLE PARTS, NOT OTHERWISE PROVIDED FOR
- B60R16/00—Electric or fluid circuits specially adapted for vehicles and not otherwise provided for; Arrangement of elements of electric or fluid circuits specially adapted for vehicles and not otherwise provided for
- B60R16/02—Electric or fluid circuits specially adapted for vehicles and not otherwise provided for; Arrangement of elements of electric or fluid circuits specially adapted for vehicles and not otherwise provided for electric constitutive elements
- B60R16/023—Electric or fluid circuits specially adapted for vehicles and not otherwise provided for; Arrangement of elements of electric or fluid circuits specially adapted for vehicles and not otherwise provided for electric constitutive elements for transmission of signals between vehicle parts or subsystems
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F21/00—Security arrangements for protecting computers, components thereof, programs or data against unauthorised activity
- G06F21/60—Protecting data
- G06F21/64—Protecting data integrity, e.g. using checksums, certificates or signatures
-
- G—PHYSICS
- G07—CHECKING-DEVICES
- G07C—TIME OR ATTENDANCE REGISTERS; REGISTERING OR INDICATING THE WORKING OF MACHINES; GENERATING RANDOM NUMBERS; VOTING OR LOTTERY APPARATUS; ARRANGEMENTS, SYSTEMS OR APPARATUS FOR CHECKING NOT PROVIDED FOR ELSEWHERE
- G07C5/00—Registering or indicating the working of vehicles
- G07C5/008—Registering or indicating the working of vehicles communicating information to a remotely located station
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L63/00—Network architectures or network communication protocols for network security
- H04L63/06—Network architectures or network communication protocols for network security for supporting key management in a packet data network
- H04L63/062—Network architectures or network communication protocols for network security for supporting key management in a packet data network for key distribution, e.g. centrally by trusted party
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L63/00—Network architectures or network communication protocols for network security
- H04L63/12—Applying verification of the received information
- H04L63/123—Applying verification of the received information received data contents, e.g. message integrity
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L67/00—Network arrangements or protocols for supporting network services or applications
- H04L67/01—Protocols
- H04L67/12—Protocols specially adapted for proprietary or special-purpose networking environments, e.g. medical networks, sensor networks, networks in vehicles or remote metering networks
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/08—Key distribution or management, e.g. generation, sharing or updating, of cryptographic keys or passwords
- H04L9/0894—Escrow, recovery or storing of secret information, e.g. secret key escrow or cryptographic key storage
- H04L9/0897—Escrow, recovery or storing of secret information, e.g. secret key escrow or cryptographic key storage involving additional devices, e.g. trusted platform module [TPM], smartcard or USB
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/32—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials
- H04L9/3236—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials using cryptographic hash functions
- H04L9/3242—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials using cryptographic hash functions involving keyed hash functions, e.g. message authentication codes [MACs], CBC-MAC or HMAC
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W4/00—Services specially adapted for wireless communication networks; Facilities therefor
- H04W4/30—Services specially adapted for particular environments, situations or purposes
- H04W4/40—Services specially adapted for particular environments, situations or purposes for vehicles, e.g. vehicle-to-pedestrians [V2P]
- H04W4/44—Services specially adapted for particular environments, situations or purposes for vehicles, e.g. vehicle-to-pedestrians [V2P] for communication between vehicles and infrastructures, e.g. vehicle-to-cloud [V2C] or vehicle-to-home [V2H]
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L2209/00—Additional information or applications relating to cryptographic mechanisms or cryptographic arrangements for secret or secure communication H04L9/00
- H04L2209/84—Vehicles
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/10—Integrity
- H04W12/106—Packet or message integrity
Definitions
- the present invention relates to a data providing system, a data security device, a data providing method, and a computer program.
- Non-Patent Document 1 discloses a security technique for an in-vehicle control system configured by connecting a plurality of ECUs to a CAN (Controller Area Network).
- the present invention has been made in view of such circumstances, and a data providing system, a data security device, a data providing method, and a data providing system capable of improving the reliability of data applied to an in-vehicle computer such as an ECU, and the like It is an object to provide a computer program.
- One aspect of the present invention includes a data providing device and a data security device mounted on a vehicle, and the data providing device is mounted on the vehicle and a vehicle interface that transmits and receives data to and from the vehicle.
- An expected value calculation unit that calculates an expected value of application data applied to the in-vehicle computer, and transmits the application data and the expected value to the vehicle through the vehicle interface
- the data security device includes the data security An interface unit for transmitting / receiving data to / from an external device of the device; and a measured value of the applied data received from the data providing device by the interface unit, and the expected value received from the data providing device by the interface unit.
- a measurement unit that verifies the measured value based on the application data that has passed the verification of the measured value.
- the data security device determines whether the application data transmitted to the in-vehicle computer is applied to the in-vehicle computer by the interface unit.
- the data providing system receives the data application result shown from the in-vehicle computer and transfers the result to the data providing apparatus.
- the data security device may transmit the application data that has passed the verification of the measurement value and a message authentication code for the application data to the in-vehicle computer through the interface unit. .
- the message authentication code may be a message authentication code related to a packet that stores the application data that has passed the verification of the measurement value and transmits the data to the in-vehicle computer.
- the data security device divides the applied data that has passed the verification of the measurement value into a plurality of blocks, calculates the message authentication code for each block, and the block and the message An authentication code may be transmitted to the in-vehicle computer by the interface unit.
- One aspect of the present invention is a data security device mounted on a vehicle, an interface unit that transmits / receives data to / from an external device of the data security device, and applied data received from a data providing device by the interface unit
- a measurement unit that calculates the measured value of the received data from the data providing apparatus by the interface unit, and verifies the measured value based on the expected value received from the data providing apparatus,
- the data security device is transmitted to the in-vehicle computer mounted on the vehicle by the unit.
- One aspect of the present invention is a data providing method of a data providing system including a data providing device and a data security device mounted on a vehicle, wherein the data providing device is mounted on the vehicle.
- An expected value of application data to be applied to a computer is calculated, and the data providing device transmits the application data and the expected value to the vehicle via a vehicle interface that transmits and receives data to and from the vehicle, and the data security device
- the measured value of the applied data received from the data providing device is calculated by an interface unit that transmits / receives data to / from an external device of the data security device, and based on the expected value received from the data providing device by the interface unit
- the measured value is verified, and the data security device converts the input data that has passed the verification of the measured value into the input data. Transmitting to the vehicle computer by a face portion, a data providing method.
- the measured value of the application data received from the data providing device by the interface unit that transmits and receives data to and from the device outside the data security device is transmitted to the computer of the data security device mounted on the vehicle.
- An in-vehicle computer that calculates and verifies the measured value based on the expected value received from the data providing device by the interface unit, and mounts the application data that has passed the verification of the measured value on the vehicle by the interface unit. It is a computer program which performs the process transmitted to.
- FIG. 1 is a diagram illustrating a configuration example of a data providing system and an automobile 1001 according to an embodiment. It is a figure which shows the structural example of the server apparatus 2000 which concerns on one Embodiment. It is a figure which shows the structural example of the data security apparatus 1010 which concerns on one Embodiment. It is a figure showing an example of composition of ECU1020 concerning one embodiment. It is a sequence chart which shows the example of the data provision method which concerns on one Embodiment. It is a flowchart which shows the Example of the data provision method which concerns on one Embodiment. It is a flowchart which shows the Example of the data provision method which concerns on one Embodiment. It is a flowchart which shows the Example of the data provision method which concerns on one Embodiment. It is a flowchart which shows the Example of the data provision method which concerns on one Embodiment. It is a flowchart which shows the Example of the data provision method which concerns on one Embodiment.
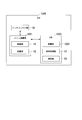
- FIG. 1 is a diagram illustrating a configuration example of a data providing system and an automobile 1001 according to an embodiment.
- an ECU electronic control device mounted on the automobile 1001 will be described as an example of the in-vehicle computer.
- an automobile 1001 includes a data security device 1010 and a plurality of ECUs 1020.
- the ECU 1020 is an in-vehicle computer provided in the automobile 1001.
- ECU 1020 has a control function such as engine control of automobile 1001. Examples of the ECU 1020 include an ECU having an engine control function, an ECU having a handle control function, and an ECU having a brake control function.
- the data security device 1010 has a data security (security) function applied to the ECU 1020 mounted on the automobile 1001. Note that any ECU mounted on the automobile 1001 may function as the data security device 1010.
- the data security device 1010 and the plurality of ECUs 1020 are connected to a CAN (Controller Area Network) 1030 provided in the automobile 1001.
- CAN 1030 is a communication network.
- CAN is known as one of communication networks mounted on vehicles.
- the data security device 1010 exchanges data with each ECU 1020 via the CAN 1030.
- ECU 1020 exchanges data with other ECUs 1020 via CAN 1030.
- a communication network other than CAN is provided in the automobile 1001, and data exchange between the data security device 1010 and the ECU 1020 and communication between the ECUs 1020 are performed via the communication network other than CAN. Data exchanges between them may be performed.
- the automobile 1001 may be provided with LIN (Local Interconnect Network).
- the automobile 1001 may include CAN and LIN.
- the automobile 1001 may be provided with an ECU 1020 connected to the LIN.
- the data security device 1010 may be connected to CAN and LIN.
- the data security device 1010 exchanges data with the ECU 1020 connected to the CAN via the CAN, and exchanges data with the ECU 1020 connected to the LIN via the LIN. Also good. Further, the ECUs 1020 may exchange data via the LIN.
- the in-vehicle computer system 1002 provided in the automobile 1001 is configured by connecting a data security device 1010 and a plurality of ECUs 1020 to a CAN 1030.
- the in-vehicle computer system 1002 functions as an in-vehicle control system for the automobile 1001.
- the gateway 1070 monitors communication between the inside and the outside of the in-vehicle computer system 1002.
- the gateway 1070 is connected to the CAN 1030.
- the gateway 1070 is connected to an infotainment device 1040, a TCU (Tele Communication Unit) 1050, and a diagnostic port 1060 as examples of devices external to the in-vehicle computer system 1002.
- the data security device 1010 and the ECU 1020 communicate with devices outside the in-vehicle computer system 1002 via the gateway 1070.
- the CAN 1030 may include a plurality of buses (communication lines), and the plurality of buses may be connected to the gateway 1070.
- the plurality of buses may be connected to the gateway 1070.
- one ECU 1020 or a plurality of ECUs 1020 is connected to one bus.
- the data security device 1010 and the ECU 1020 may be connected to the same bus, or the bus to which the data security device 1010 is connected and the bus to which the ECU 1020 is connected may be separated.
- the automobile 1001 has a diagnostic port 1060.
- the diagnostic port 1060 for example, an OBD (On-board Diagnostics) port may be used.
- a device outside the automobile 1001 can be connected to the diagnostic port 1060.
- As an external device of the automobile 1001 that can be connected to the diagnosis port 1060 for example, there is a maintenance tool 2100 shown in FIG. Data is exchanged between the data security device 1010 and a device connected to the diagnostic port 1060, such as the maintenance tool 2100, via the diagnostic port 1060 and the gateway 1070.
- the maintenance tool 2100 may have a function of a conventional diagnostic terminal connected to the OBD port.
- the automobile 1001 includes an infotainment device 1040.
- infotainment device 1040 examples include a navigation function, a location information service function, a multimedia playback function such as music and video, a voice communication function, a data communication function, and an Internet connection function.
- the automobile 1001 includes a TCU 1050.
- the TCU 1050 is a communication device.
- the TCU 1050 includes a communication module 1051.
- the communication module 1051 performs wireless communication using a wireless communication network.
- the communication module 1051 includes a SIM (Subscriber Identity Module) 1052.
- the SIM 1052 is a SIM in which information for using the wireless communication network is written.
- the communication module 1051 can use the SIM 1052 to connect to the wireless communication network and perform wireless communication.
- eSIM Embedded Subscriber Identity
- the data security device 1010 exchanges data with the TCU 1050 via the gateway 1070.
- the TCU 1050 and the data security device 1010 may be directly connected via a communication cable, and the TCU 1050 and the data security device 1010 may exchange data via the communication cable.
- the TCU 1050 and the data security device 1010 may be directly connected via a USB (universal serial bus) cable, and the TCU 1050 and the data security device 1010 may exchange data via the USB cable.
- the transmission-side apparatus may include a buffer that temporarily stores data to be transmitted to the reception-side apparatus.
- the TCU 1050 may be connected to the infotainment device 1040, and the data security device 1010 may exchange data with the TCU 1050 via the gateway 1070 and the infotainment device 1040.
- the TCU 1050 may be connected to the diagnostic port 1060, and the data security device 1010 may exchange data with the TCU 1050 connected to the diagnostic port 1060 via the gateway 1070 and the diagnostic port 1060.
- the data security device 1010 may include a communication module 1051 including a SIM 1052. When the data security device 1010 includes the communication module 1051 including the SIM 1052, the automobile 1001 may not include the TCU 1050.
- the data security device 1010 includes a main computing unit 1011 and an HSM (Hardware Security Module) 1012.
- the main arithmetic unit 1011 executes a computer program for realizing the functions of the data security device 1010.
- the HSM 1012 has a cryptographic processing function and the like.
- HSM 1012 has tamper resistance.
- the HSM 1012 is an example of a secure element (Secure Element: SE).
- SE Secure Element
- the HSM 1012 includes a storage unit 1013 that stores data.
- the main arithmetic unit 1011 uses an HSM 1012.
- the ECU 1020 includes a main computing unit 1021 and a SHE (Secure Hardware Extension) 1022.
- the main computing unit 1021 executes a computer program for realizing the functions of the ECU 1020.
- the SHE 1022 has a cryptographic processing function and the like.
- SHE1022 has tamper resistance.
- SHE1022 is an example of a secure element.
- the SHE 1022 includes a storage unit 1023 that stores data.
- the main computing unit 1021 uses SHE1022.
- the server device 2000 transmits and receives data to and from the communication module 1051 of the TCU 1050 of the automobile 1001 via the communication line.
- Server device 2000 transmits and receives data to and from communication module 1051 via a wireless communication network used by communication module 1051 of TCU 1050 of automobile 1001.
- the server device 2000 may transmit / receive data to / from the communication module 1051 via a communication network such as the Internet and the wireless communication network.
- the server apparatus 2000 and the communication module 1051 may be connected by a dedicated line such as a VPN (Virtual Private Network) line, and data may be transmitted and received through the dedicated line.
- a dedicated line such as a VPN line may be provided by a wireless communication network corresponding to the SIM 1052.
- Server device 2000 and automobile 1001 may be connected by a communication cable.
- the server apparatus 2000 and the gateway 1070 of the automobile 1001 may be configured to be connected with a communication cable.
- the server device 2000 provides the vehicle 1001 with an ECU code (ECU code) applied to the ECU 1020.
- ECU code is an example of data applied to the ECU 1020.
- the ECU code may be a computer program such as an update program installed in the ECU 1020, or may be setting data such as a parameter setting value set in the ECU 1020.
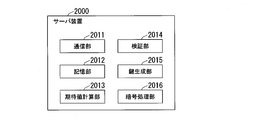
- FIG. 2 is a diagram illustrating a configuration example of the server apparatus 2000.
- the server device 2000 includes a communication unit 2011, a storage unit 2012, an expected value calculation unit 2013, a verification unit 2014, a key generation unit 2015, and an encryption processing unit 2016.
- the communication unit 2011 communicates with other devices via a communication line.
- the communication unit 2011 corresponds to a vehicle interface.
- the storage unit 2012 stores data.
- the expected value calculation unit 2013 calculates an expected value for the ECU code.
- the verification unit 2014 performs processing related to verification of the measurement value of the ECU 1020.
- the key generation unit 2015 generates a key.
- the encryption processing unit 2016 encrypts data and decrypts encrypted data.
- the function of the server device 2000 is realized by a CPU (Central Processing Unit) included in the server device 2000 executing a computer program.
- the server device 2000 may be configured using a general-purpose computer device, or may be configured as a dedicated hardware device.
- FIG. 3 is a diagram illustrating a configuration example of the data security device 1010.
- the data security device 1010 includes a main arithmetic unit 1011, an HSM 1012, and an interface unit 20.
- the main computing unit 1011 includes a control unit 21 and a storage unit 22.
- the HSM 1012 includes a storage unit 1013, an encryption processing unit 32, and a measurement unit 33.
- the interface unit 20 transmits / receives data to / from an external device of the own data security device 1010.
- the interface unit 20 includes an interface that transmits and receives data via the CAN 1030.
- the main computing unit 1011 transmits / receives data to / from devices other than the data security device 1010 via the interface unit 20.
- the control unit 21 controls the data security device 1010.
- the storage unit 22 stores data.
- the storage unit 1013 stores data.
- the encryption processing unit 32 encrypts data and decrypts encrypted data.
- the measurement unit 33 calculates a measured value of data such as an ECU code and verifies the measured value based on an expected value.
- FIG. 4 is a diagram illustrating a configuration example of the ECU 1020.
- the ECU 1020 includes a main computing unit 1021, a SHE 1022, and an interface unit 40.
- the main computing unit 1021 includes a control unit 41 and a storage unit 42.
- the SHE 1022 includes a storage unit 1023, an encryption processing unit 52, and a measurement unit 53.
- the interface unit 40 transmits / receives data to / from an external device of the own ECU 1020.
- the interface unit 40 includes an interface that transmits and receives data via the CAN 1030.
- the main computing unit 1021 transmits and receives data to and from devices other than its own ECU 1020 via the interface unit 40.
- the control unit 41 controls the ECU 1020.
- the storage unit 42 stores data.
- the storage unit 1023 stores data.
- the encryption processing unit 52 encrypts data and decrypts encrypted data.
- the measurement unit 53 calculates a measurement value of data such as an ECU code, and verifies the measurement value based on an expected value.
- HSM is used for the data security device 1010
- SHE may be used in the data security device 1010 instead of HSM.
- SHE it describes in the nonpatent literature 2, for example.
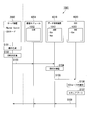
- FIG. 5 is a sequence chart showing an example of a data providing method according to the present embodiment.
- the server apparatus 2000 stores the master key Master_Secret and the ECU code of the ECU 1020 in the storage unit 2012 in advance.
- the ECU code of ECU 1020 includes an ECU code scheduled to be applied to ECU 1020.
- the data security device 1010 stores the signature key Kbc and the encryption key Kec in the storage unit 1013 of the HSM 1012 in advance.
- the ECU 1020 stores the signature key Kbe in the storage unit 1023 of the SHE 1022 in advance.
- the server apparatus 2000 communicates with the TCU 1050 of the automobile 1001 through the communication unit 2011, and transmits / receives data to / from the data security apparatus 1010 connected to the CAN 1030 of the automobile 1001 via the TCU 1050 and the gateway 1070.
- An encrypted communication path may be used as a communication path between server device 2000 and data security device 1010.
- the server apparatus 2000 and the data security apparatus 1010 may perform https (hypertext transfer transfer protocol secure) communication as an example of an encrypted communication path.
- Step S101 The key generation unit 2015 of the server device 2000 generates the signature key Kbc and encryption key Kec of the data security device 1010 mounted on the automobile 1001 and the signature key Kbe of the ECU 1020.
- the key generation unit 2015 uses the master key Master_Secret stored in the storage unit 2012, the identifier UNIT_ID of the key generation target device, and the variable Nk to generate a key (common key) according to the following equation.
- Common key digest (Master_Secret, UNIT_ID, Nk)
- UNIT_ID is the identifier SecU_ID of the data security device 1010.
- UNIT_ID is the identifier ECU_ID of the ECU 1020.
- the digest (Master_Secret, UNIT_ID, Nk) is a digest value generated from the master key Master_Secret, the identifier UNIT_ID, and the variable Nk. Examples of the digest value include a value calculated by a hash function, a value calculated by an exclusive OR operation, or CMAC (Cipher-based Message Authentication Code).
- the common key is a hash function value calculated using a master key Master_Secret, an identifier UNIT_ID, and a variable Nk as input values.
- the digest value is different.
- different common keys can be generated from the same master key Master_Secret and identifier UNIT_ID.
- the value of the signature key variable Nk is Nk_a
- the value of the encryption key variable Nk is Nk_b.
- the storage unit 2012 stores the signature key Kbc and encryption key Kec of the data security device 1010 and the signature key Kbe of the ECU 1020.
- the storage unit 1013 of the HSM 1012 of the data security device 1010 stores in advance a signature key Kbc and an encryption key Kec generated by the same key generation method as the server device 2000.
- the storage unit 1023 of the SHE 1022 of the ECU 1020 stores in advance a signature key Kbe generated by the same key generation method as the server device 2000.
- the signature key may be a value calculated by a hash function
- the encryption key may be a value calculated by an exclusive OR operation.
- the signature key may be a value calculated by an exclusive OR operation
- the encryption key may be a value calculated by a hash function.
- the expected value calculation unit 2013 of the server device 2000 calculates the CMAC of the ECU code to be applied to the ECU 1020 mounted on the automobile 1001 using the signature key Kbc of the data security device 1010.
- the calculated CMAC is an expected value for the ECU code.
- CMAC is used as an example of the measured value of the ECU code.
- the expected value (CMAC) of the ECU code calculated by the expected value calculation unit 2013 is used for verification of the measured value (CMAC) of the ECU code.
- the storage unit 2012 stores an expected value (CMAC) of the ECU code.
- Step S ⁇ b> 103 The server device 2000 transmits the ECU code applied to the ECU 1020 and the expected value (CMAC) calculated by the expected value calculation unit 2013 to the data security device 1010 through the communication unit 2011.
- the data security device 1010 receives the ECU code and the expected value (CMAC) transmitted from the server device 2000.
- Step S104 The control unit 21 of the data security device 1010 passes the CMAC of the expected value received from the server device 2000 to the HSM 1012, and sets the CMAC to the expected value of the measurement value in the HSM 1012.
- the control unit 21 passes the ECU code received from the server device 2000 to the HSM 1012 and causes the HSM 1012 to execute measurement of the ECU code.
- the measuring unit 33 of the HSM 1012 calculates the measured value of the ECU code using the signature key Kbc stored in the storage unit 1013.
- CMAC is used as an example of the measurement value. Therefore, the measurement unit 33 calculates the CMAC of the ECU code using the signature key Kbc stored in the storage unit 1013.
- the measuring unit 33 compares the expected value CMAC with the calculated measured value CMAC. As a result of this comparison, when the two values match, the verification of the measurement value (CMAC) is acceptable, and when the two values do not match, the verification of the measurement value (CMAC) fails.
- the HSM 1012 passes the measurement result verification result “pass or fail” to the control unit 21.
- the control unit 21 proceeds with the process to step S105.
- the control part 21 complete finishes the process of FIG. 5, when the verification result of the measured value of ECU code fails.
- the control unit 21 may execute a predetermined error process. For example, the control unit 21 may transmit an error message indicating that the verification result of the measured value of the ECU code is unacceptable to the server device 2000.
- the server device 2000 may execute predetermined error processing in response to the error message. For example, the server device 2000 may retransmit the ECU code and the expected value (CMAC) to the data security device 1010, or may regenerate the expected value (CMAC) and transmit it to the data security device 1010. Good.
- Step S ⁇ b> 105 The control unit 21 of the data security device 1010 transmits the ECU code that has passed the verification of the measured value of the ECU code to the ECU 1020 by the interface unit 20. ECU 1020 receives the ECU code transmitted from data security device 1010.
- Step S106 The control unit 41 of the ECU 1020 applies the ECU code received from the data security device 1010 to the own ECU 1020.
- Step S107 The control unit 41 of the ECU 1020 executes secure boot after application of the ECU code.
- the measurement unit 53 of the SHE 1022 calculates the measured value of the ECU code using the signature key Kbe stored in the storage unit 1023.
- CMAC is used as an example of the measurement value. Therefore, the measurement unit 53 calculates the CMAC of the ECU code using the signature key Kbe stored in the storage unit 1023.
- the measuring unit 53 compares the calculated CMAC with the expected value.
- the control unit 41 sets an expected value in the SHE 1022 in advance before executing the secure boot.
- the SHE 1022 passes the secure boot result to the control unit 41.
- the control unit 41 advances the execution of the ECU code when the secure boot result is acceptable.
- the control part 41 stops execution of ECU code, when a secure boot result is a failure.
- the expected value used in the secure boot of the ECU 1020 is supplied from the server device 2000 or the data security device 1010 to the ECU 1020 in advance.
- the expected value calculation unit 2013 of the server apparatus 2000 calculates an expected value (CMAC) of the ECU code using the signature key Kbe of the ECU 1020.
- the signature key Kbe of ECU 1020 is shared between ECU 1020 and server device 2000 in advance.
- the server apparatus 2000 calculates an expected value (CMAC) of “expected value (CMAC) used in secure boot of ECU 1020” using the signature key Kbc of the data security apparatus 1010 in the same manner as in step S102. Then, the server apparatus 2000 may transmit the CMAC as a result of the calculation and “expected value (CMAC) used in the secure boot of the ECU 1020” to the data security apparatus 1010 as in step S103.
- the data security device 1010 verifies the “expected value (CMAC) used in the secure boot of the ECU 1020” received from the server device 2000 and the CMAC of the expected value using its own signature key Kbc as in step S104. Do. Similarly to step S105, the data security device 1010 transmits the “expected value (CMAC) used in the secure boot of the ECU 1020” received from the server device 2000 to the ECU 1020 when the verification is passed. “Expected value (CMAC) used in secure boot of ECU 1020” is an example of data applied to ECU 1020.
- the data security device 1010 when the data security device 1010 supplies the ECU 1020 with an expected value to be used for secure boot, the data security device 1010 has an expected value calculation unit, and an expected value (ECU code) (with the signature key Kbe of the ECU 1020) CMAC).
- ECU code an expected value (ECU code) (with the signature key Kbe of the ECU 1020) CMAC).
- the signature key Kbe of ECU 1020 is shared between ECU 1020 and data security device 1010 in advance.
- Step S ⁇ b> 1028 The control unit 41 of the ECU 1020 transmits the secure boot result “pass or fail” to the data security device 1010 through the interface unit 40.
- the data security device 1010 transfers the secure boot result “pass or fail” received from the ECU 1020 to the server device 2000.
- the secure boot result “pass or fail” corresponds to a data application result indicating whether or not the ECU code is applied to the ECU 1020.
- the server device 2000 receives the secure boot result “pass or fail” transmitted from the data security device 1010 via the communication unit 2011.
- the server device 2000 executes a predetermined process according to the secure boot result “passed or failed” received from the data security device 1010. For example, if the secure boot result is acceptable, the fact is recorded. On the other hand, when the secure boot result is unacceptable, the server apparatus 2000 may execute predetermined error processing. For example, as error processing, the server device 2000 retransmits the ECU code and the expected value (CMAC) to the data security device 1010, or regenerates the expected value (CMAC) and transmits it to the data security device 1010. Or you may. Further, the error processing may be repeated until the secure boot result is passed, or may be repeated a predetermined number of times.
- CMAC expected value
- step S107 the secure boot after application of the ECU code in step S107 described above is not essential and may not be executed.
- step S ⁇ b> 103 the server apparatus 2000 encrypts the ECU code by the encryption processing unit 2016 and transmits it to the data security apparatus 1010.
- the key used for this encryption is the encryption key Kec of the data security device 1010.
- the data security device 1010 obtains the ECU code by decrypting the encrypted data received from the server device 2000 with the encryption key Kec stored in the storage unit 1013 by the encryption processing unit 32 of the HSM 1012.
- step S ⁇ b> 105 the data security device 1010 encrypts the ECU code by the encryption processing unit 32 of the HSM 1012 and transmits it to the ECU 1020.
- the key used for this encryption is shared between the data security device 1010 and the ECU 1020 in advance.
- the ECU 1020 obtains the ECU code by decrypting the encrypted data received from the data security device 1010 with the corresponding key stored in the storage unit 1023 by the encryption processing unit 52 of the SHE 1022.
- step S105 the ECU code is stored in a packet of CAN 1030 and transmitted from the data security device 1010 to the ECU 1020.
- the data security device 1010 further includes CMAC for the packet in the packet.
- the key used for generating the CMAC is shared between the data security device 1010 and the ECU 1020 in advance.
- the ECU 1020 verifies the CMAC included in the packet received from the data security device 1010 with the corresponding key.
- the ECU 1020 applies the ECU code when the verification of the CMAC has passed. On the other hand, the ECU 1020 does not apply the ECU code when the CMAC verification fails.
- CMAC about all or a part of the ECU code may be used as the CMAC included in the packet storing the ECU code.
- the data security device 1010 may divide the ECU code into blocks of a certain size, calculate the CMAC for each block, and store the block and the CMAC in a packet.
- the ECU 1020 acquires the ECU code while verifying the CMAC for each block.
- the key used for generating the CMAC is shared between the data security device 1010 and the ECU 1020 in advance.
- step S108 the secure boot result “pass or fail” transmitted from the ECU 1020 to the server device 2000 is set to a predetermined value. For example, the pass is “1” and the failure is “0”.
- the secure boot result “pass or fail” transmitted from the ECU 1020 to the server apparatus 2000 is the CMAC of the ECU code calculated in the secure boot in step S107.
- the verification unit 2014 of the server device 2000 calculates the CMAC of the ECU code transmitted to the data security device 1010 in step S103 using the signature key Kbe of the ECU 1020.
- the verification unit 2014 of the server device 2000 compares the CMAC of the calculation result with the CMAC of the secure boot result of the ECU 1020. As a result of the comparison, the verification unit 2014 of the server device 2000 determines that the secure boot result of the ECU 1020 is acceptable if both match, and if the both do not match, the secure boot result of the ECU 1020 fails. Judge that there is.
- the server device 2000 supplies a verification value (for example, a random number) to the ECU 1020 in advance.
- the ECU 1020 includes the verification value in the secure boot result “pass” if the secure boot result is pass, while the secure boot result “fail” if the secure boot result is fail. Do not include verification values.
- the verification unit 2014 of the server device 2000 compares the verification value included in the secure boot result “pass” of the ECU 1020 with the original verification value supplied to the ECU 1020 in advance. As a result of the comparison, the verification unit 2014 of the server device 2000 determines that the secure boot result of the ECU 1020 is acceptable if both match, and if the both do not match, the secure boot result of the ECU 1020 fails. Judge that there is.
- the ECU 1020 encrypts the secure boot result by the encryption processing unit 52 of the SHE 1022 and transmits it to the server device 2000.
- the key used for this encryption is shared between server device 2000 and ECU 1020 in advance.
- the server device 2000 uses the encryption processing unit 2016 to decrypt the encrypted data from the ECU 1020 with the corresponding key stored in the storage unit 2012, and obtains a secure boot result.
- an encryption key that can be used by the SHE 1022 only when the secure boot result is acceptable may be used as the key used for the encryption.
- the secure boot result “pass” may be encrypted with the encryption key.
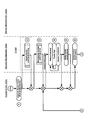
- 6 to 8 are flowcharts showing examples of the data providing method according to the present embodiment.
- “Non-volatile server server memory programming process” of Chapter 15 described in Non-Patent Document 3 the procedure of “15.2.1.2 Programming stepof phase # 1”-“Download” of ”application” software ”and” data ”and“ 15.2. .1.3Post-Programming step of phase # 1-Re-synchronization of vehicle network ”procedure.
- 6 and 7 show “graphically depicts the functionality embedded in the programming step of phase" of FIG.
- FIG. 8 shows “graphicallypicdepicts the functionality embedded in the post-programming step ⁇ of” of FIG. 34 of “15.2.1.3-Post-Programming step of phase # 1 --Re-synchronization of vehicle network” described in Non-Patent Document 3. An application example of “phase # 1” is shown.
- the step indicated by reference numeral S1001 corresponds to the security access (Security Access) processing of the data security device 1010.
- the step indicated by reference numeral S ⁇ b> 1002 corresponds to the decryption process for each block of the ECU code of the data security device 1010 and the verification of the electronic signature.
- the step indicated by reference numeral S1003 corresponds to the ECU 1020 ECU code verification process.
- the step indicated by reference numeral S1004 corresponds to the secure boot process after the ECU code of the ECU 1020 is applied.
- the data security device 1010 verifies the measured value (CMAC) of the ECU code based on the expected value (CMAC) of the ECU code provided from the server device 2000, and determines the measured value (CMAC).
- the ECU code that has passed the CMAC verification is transmitted to the ECU 1020.
- the reliability of the ECU code applied to the ECU 1020 can be improved.
- the server apparatus 2000 supplies the ECU 1020 with an expected value used in the secure boot
- the data security apparatus 1010 receives the “expected value used in the secure boot of the ECU 1020 received from the server apparatus 2000, similarly to the ECU code. And the expected value (CMAC) of the expected value is verified. Thereby, the reliability of the “expected value used in secure boot” applied to the ECU 1020 can be improved.
- the server device 2000 corresponds to a data providing device.
- the maintenance tool 2100 may have the same function as the server device 2000.
- the maintenance tool 2100 provides the ECU code to the ECU 1020 via the diagnostic port 1060 and the data security device 1010 by the same data providing method as the server device 2000.
- the TCU 1050 or the gateway 1070 of the automobile 1001 may have the function of the data security device 1010.
- HSM and SHE are used for the data security device 1010 and the ECU 1020, but cryptographic processing chips other than HSM and SHE may be used.
- a cryptographic processing chip called “TPM (Trusted Platform Module) f” may be used.
- TPMf has tamper resistance.
- TPMf is an example of a secure element.
- a cryptographic processing chip called “TPMt” may be used.
- TPMt has tamper resistance.
- TPMt is an example of a secure element.
- the embodiment described above may be applied to an ECU mounted on a car in a car manufacturing process in a car manufacturing factory. Further, the above-described embodiment may be applied to an ECU mounted on an automobile in an automobile maintenance factory, a dealer, or the like.
- an automobile is taken as an example of a vehicle, but the present invention can also be applied to other vehicles such as a motorbike and a railway vehicle.
- a computer program for realizing the functions of each device described above may be recorded on a computer-readable recording medium, and the program recorded on the recording medium may be read into a computer system and executed.
- the “computer system” may include an OS and hardware such as peripheral devices.
- “Computer-readable recording medium” refers to a flexible disk, a magneto-optical disk, a ROM, a writable nonvolatile memory such as a flash memory, a portable medium such as a DVD (Digital Versatile Disc), and a built-in computer system.
- a storage device such as a hard disk.
- the “computer-readable recording medium” means a volatile memory (for example, DRAM (Dynamic DRAM) in a computer system that becomes a server or a client when a program is transmitted through a network such as the Internet or a communication line such as a telephone line. Random Access Memory)), etc., which hold programs for a certain period of time.
- the program may be transmitted from a computer system storing the program in a storage device or the like to another computer system via a transmission medium or by a transmission wave in the transmission medium.
- the “transmission medium” for transmitting the program refers to a medium having a function of transmitting information, such as a network (communication network) such as the Internet or a communication line (communication line) such as a telephone line.
- the program may be for realizing a part of the functions described above. Furthermore, what can implement
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Hardware Design (AREA)
- General Engineering & Computer Science (AREA)
- Theoretical Computer Science (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Software Systems (AREA)
- Physics & Mathematics (AREA)
- General Physics & Mathematics (AREA)
- Computing Systems (AREA)
- General Health & Medical Sciences (AREA)
- Health & Medical Sciences (AREA)
- Mechanical Engineering (AREA)
- Power Engineering (AREA)
- Bioethics (AREA)
- Medical Informatics (AREA)
- Stored Programmes (AREA)
- Small-Scale Networks (AREA)
- Information Transfer Between Computers (AREA)
Abstract
データ提供システムは、データ提供装置と、車両に搭載されるデータ保安装置とを備える。前記データ提供装置は、前記車両とデータを送受する車両インタフェースと、前記車両に搭載される車載コンピュータに適用される適用データの期待値を計算する期待値計算部と、を備え、前記適用データ及び前記期待値を前記車両インタフェースにより前記車両に送信する。前記データ保安装置は、前記データ保安装置の外部の装置とデータを送受するインタフェース部と、前記インタフェース部により前記データ提供装置から受信した前記適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した前記期待値に基づいて該測定値を検証する測定部と、を備え、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車載コンピュータに送信する。
Description
本発明は、データ提供システム、データ保安装置、データ提供方法、及びコンピュータプログラムに関する。
本願は、2016年8月10日に、日本に出願された特願2016-158121号に基づき優先権を主張し、その内容をここに援用する。
本願は、2016年8月10日に、日本に出願された特願2016-158121号に基づき優先権を主張し、その内容をここに援用する。
従来、自動車は、ECU(Electronic Control Unit:電子制御装置)を有し、ECUによってエンジン制御等の機能を実現する。ECUは、コンピュータの一種であり、コンピュータプログラムによって所望の機能を実現する。複数のECUをCAN(Controller Area Network)に接続して構成される車載制御システムについてのセキュリティ技術が例えば非特許文献1に記載されている。
竹森敬祐、"セキュアエレメントを基点とした車載制御システムの保護 -要素技術の整理と考察-"、電子情報通信学会、信学技報、vol. 114、no. 508、pp. 73-78、2015年3月
STMicroelectronics、"AN4240 Application note"、[平成28年8月3日検索]、インターネット<URL:http://www.st.com/web/en/resource/technical/document/application_note/DM00075575.pdf>
INTERNATIONAL STANDARD、ISO14229-1、「Road vehicles Unifieddiagnostic services (UDS) Part 1: Specification and requirements」、Second edition、2013-03-15
自動車の車載制御システムのECUに適用される更新プログラム等のデータの信頼性を向上させることが一つの課題であった。
本発明は、このような事情を考慮してなされたものであり、ECU等の車載コンピュータに適用されるデータの信頼性を向上させることができるデータ提供システム、データ保安装置、データ提供方法、及びコンピュータプログラムを提供することを課題とする。
(1)本発明の一態様は、データ提供装置と、車両に搭載されるデータ保安装置とを備え、前記データ提供装置は、前記車両とデータを送受する車両インタフェースと、前記車両に搭載される車載コンピュータに適用される適用データの期待値を計算する期待値計算部と、を備え、前記適用データ及び前記期待値を前記車両インタフェースにより前記車両に送信し、前記データ保安装置は、前記データ保安装置の外部の装置とデータを送受するインタフェース部と、前記インタフェース部により前記データ提供装置から受信した前記適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した前記期待値に基づいて該測定値を検証する測定部と、を備え、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車載コンピュータに送信する、データ提供システムである。
(2)本発明の一態様は、上記(1)のデータ提供システムにおいて、前記データ保安装置は、前記インタフェース部により、前記車載コンピュータに送信した前記適用データの前記車載コンピュータへの適用の合否を示すデータ適用結果を前記車載コンピュータから受信して前記データ提供装置へ転送する、データ提供システムである。
本発明の一態様においては、前記データ保安装置は、前記測定値の検証が合格した前記適用データと、当該適用データについてのメッセージ認証符号とを前記インタフェース部により前記車載コンピュータに送信してもよい。
本発明の一態様においては、前記メッセージ認証符号は、前記測定値の検証が合格した前記適用データを格納して前記車載コンピュータに伝送するパケットに関するメッセージ認証符号であってもよい。
本発明の一態様においては、前記データ保安装置は、前記測定値の検証が合格した前記適用データを複数のブロックに分割し、該ブロック毎に前記メッセージ認証符号を計算し、該ブロックと該メッセージ認証符号とを前記インタフェース部により前記車載コンピュータに送信してもよい。
(3)本発明の一態様は、車両に搭載されるデータ保安装置であり、前記データ保安装置の外部の装置とデータを送受するインタフェース部と、前記インタフェース部によりデータ提供装置から受信した適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した期待値に基づいて該測定値を検証する測定部と、を備え、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車両に搭載される車載コンピュータに送信する、データ保安装置である。
(4)本発明の一態様は、データ提供装置と、車両に搭載されるデータ保安装置とを備えるデータ提供システムのデータ提供方法であって、前記データ提供装置が、前記車両に搭載される車載コンピュータに適用される適用データの期待値を計算し、前記データ提供装置が、前記適用データ及び前記期待値を、前記車両とデータを送受する車両インタフェースにより前記車両に送信し、前記データ保安装置が、前記データ保安装置の外部の装置とデータを送受するインタフェース部により前記データ提供装置から受信した前記適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した前記期待値に基づいて該測定値を検証し、前記データ保安装置が、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車載コンピュータに送信する、データ提供方法である。
(5)本発明の一態様は、車両に搭載されるデータ保安装置のコンピュータに、前記データ保安装置の外部の装置とデータを送受するインタフェース部によりデータ提供装置から受信した適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した期待値に基づいて該測定値を検証し、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車両に搭載される車載コンピュータに送信する、処理を実行させるコンピュータプログラムである。
本発明によれば、ECU等の車載コンピュータに適用されるデータの信頼性を向上させることができるという効果が得られる。
以下、図面を参照し、本発明の実施形態について説明する。なお、以下に示す実施形態では、車両として自動車を例に挙げて説明する。
図1は、一実施形態に係るデータ提供システム及び自動車1001の構成例を示す図である。本実施形態では、車載コンピュータの一例として、自動車1001に搭載されるECU(電子制御装置)を挙げて説明する。
図1において、自動車1001は、データ保安装置1010と複数のECU1020とを備える。ECU1020は、自動車1001に備わる車載コンピュータである。ECU1020は、自動車1001のエンジン制御等の制御機能を有する。ECU1020として、例えば、エンジン制御機能を有するECU、ハンドル制御機能を有するECU、ブレーキ制御機能を有するECUなどがある。データ保安装置1010は、自動車1001に搭載されたECU1020に適用されるデータのセキュリティ(保安)の機能を有する。
なお、自動車1001に搭載されたいずれかのECUをデータ保安装置1010として機能させてもよい。
なお、自動車1001に搭載されたいずれかのECUをデータ保安装置1010として機能させてもよい。
データ保安装置1010と複数のECU1020とは、自動車1001に備わるCAN(Controller Area Network)1030に接続される。CAN1030は通信ネットワークである。CANは車両に搭載される通信ネットワークの一つとして知られている。データ保安装置1010は、CAN1030を介して、各ECU1020との間でデータを交換する。ECU1020は、CAN1030を介して、他のECU1020との間でデータを交換する。
なお、車両に搭載される通信ネットワークとして、CAN以外の通信ネットワークを自動車1001に備え、CAN以外の通信ネットワークを介して、データ保安装置1010とECU1020との間のデータの交換、及び、ECU1020同士の間のデータの交換が行われてもよい。例えば、LIN(Local Interconnect Network)が自動車1001に備えられてもよい。また、CANとLINとが自動車1001に備えられてもよい。また、自動車1001において、LINに接続するECU1020が備えられてもよい。また、データ保安装置1010は、CANとLINとに接続されてもよい。また、データ保安装置1010は、CANを介して該CANに接続されるECU1020との間でデータを交換し、また、LINを介して該LINに接続されるECU1020との間でデータを交換してもよい。また、ECU1020同士が、LINを介してデータを交換してもよい。
自動車1001に備わる車載コンピュータシステム1002は、データ保安装置1010と複数のECU1020とがCAN1030に接続されて構成される。本実施形態において、車載コンピュータシステム1002は、自動車1001の車載制御システムとして機能する。
ゲートウェイ1070は、車載コンピュータシステム1002の内部と外部の間の通信を監視する。ゲートウェイ1070はCAN1030に接続される。また、ゲートウェイ1070は、車載コンピュータシステム1002の外部の装置の例として、インフォテイメント機器1040、TCU(Tele Communication Unit)1050及び診断ポート1060と接続される。データ保安装置1010及びECU1020は、ゲートウェイ1070を介して、車載コンピュータシステム1002の外部の装置と通信を行う。
なお、CAN1030の構成として、CAN1030が複数のバス(通信線)を備え、該複数のバスがゲートウェイ1070に接続されてもよい。この場合、一つのバスに、一つのECU1020又は複数のECU1020が接続される。また、同じバスにデータ保安装置1010とECU1020とが接続されてもよく、又は、データ保安装置1010が接続されるバスとECU1020が接続されるバスとが別個にされてもよい。
自動車1001は診断ポート1060を備える。診断ポート1060として、例えばOBD(On-board Diagnostics)ポートが使用されてもよい。診断ポート1060には、自動車1001の外部の装置を接続可能である。診断ポート1060に接続可能な自動車1001の外部の装置として、例えば、図1に示されるメンテナンスツール2100などがある。データ保安装置1010と、診断ポート1060に接続された装置、例えばメンテナンスツール2100とは、診断ポート1060及びゲートウェイ1070を介して、データが交換される。メンテナンスツール2100は、OBDポートに接続される従来の診断端末の機能を有していてもよい。
自動車1001はインフォテイメント(Infotainment)機器1040を備える。インフォテイメント機器1040として、例えば、ナビゲーション機能、位置情報サービス機能、音楽や動画などのマルチメディア再生機能、音声通信機能、データ通信機能、インターネット接続機能などを有するものが挙げられる。
自動車1001は、TCU1050を備える。TCU1050は通信装置である。TCU1050は通信モジュール1051を備える。通信モジュール1051は、無線通信ネットワークを利用して無線通信を行う。通信モジュール1051は、SIM(Subscriber Identity Module)1052を備える。SIM1052は、無線通信ネットワークを利用するための情報が書き込まれたSIMである。通信モジュール1051は、SIM1052を使用することにより該無線通信ネットワークに接続して無線通信を行うことができる。なお、SIM1052として、eSIM(Embedded Subscriber Identity Module)が使用されてもよい。
データ保安装置1010は、ゲートウェイ1070を介して、TCU1050とデータを交換する。なお、TCU1050とデータ保安装置1010とを通信ケーブルで直接接続し、TCU1050とデータ保安装置1010は該通信ケーブルを介してデータを交換してもよい。例えば、USB(universal serial bus)ケーブルでTCU1050とデータ保安装置1010とを直接接続し、TCU1050とデータ保安装置1010は該USBケーブルを介してデータを交換してもよい。また、TCU1050とデータ保安装置1010とをUSBケーブル等の通信ケーブルで直接接続し、該通信ケーブルを介してTCU1050とデータ保安装置1010間のデータの交換を行う場合、TCU1050とデータ保安装置1010とのうち送信側の装置は、受信側の装置に送信するデータを一時的に蓄えるバッファを備えてもよい。
なお、TCU1050の他の接続形態として、例えば、TCU1050をインフォテイメント機器1040に接続し、データ保安装置1010が、ゲートウェイ1070及びインフォテイメント機器1040を介して、TCU1050とデータを交換してもよい。又は、TCU1050を診断ポート1060に接続し、データ保安装置1010が、ゲートウェイ1070及び診断ポート1060を介して、該診断ポート1060に接続されたTCU1050とデータを交換してもよい。又は、データ保安装置1010が、SIM1052を含む通信モジュール1051を備えてもよい。データ保安装置1010がSIM1052を含む通信モジュール1051を備える場合には、自動車1001はTCU1050を備えなくてもよい。
データ保安装置1010は、メイン演算器1011とHSM(Hardware Security Module)1012とを備える。メイン演算器1011は、データ保安装置1010の機能を実現させるためのコンピュータプログラムを実行する。HSM1012は暗号処理機能等を有する。HSM1012は耐タンパー性(Tamper Resistant)を有する。HSM1012はセキュアエレメント(Secure Element:SE)の例である。HSM1012は、データを記憶する記憶部1013を備える。メイン演算器1011はHSM1012を使用する。
ECU1020は、メイン演算器1021とSHE(Secure Hardware Extension)1022とを備える。メイン演算器1021は、ECU1020の機能を実現させるためのコンピュータプログラムを実行する。SHE1022は暗号処理機能等を有する。SHE1022は耐タンパー性を有する。SHE1022はセキュアエレメントの例である。SHE1022は、データを記憶する記憶部1023を備える。メイン演算器1021はSHE1022を使用する。
サーバ装置2000は、通信回線を介して、自動車1001のTCU1050の通信モジュール1051とデータを送受する。サーバ装置2000は、自動車1001のTCU1050の通信モジュール1051が利用する無線通信ネットワークを介して、該通信モジュール1051とデータを送受する。又は、サーバ装置2000は、インターネット等の通信ネットワークと該無線通信ネットワークとを介して、該通信モジュール1051とデータを送受してもよい。また、例えば、サーバ装置2000と通信モジュール1051との間がVPN(Virtual Private Network)回線等の専用回線で接続され、該専用回線でデータが送受されてもよい。例えば、SIM1052に対応する無線通信ネットワークによって、VPN回線等の専用回線が提供されてもよい。なお、サーバ装置2000と自動車1001とが通信ケーブルで接続されてもよい。例えば、サーバ装置2000と自動車1001のゲートウェイ1070とが通信ケーブルで接続するように構成されてもよい。
サーバ装置2000は、ECU1020に適用されるECUコード(ECU code)を自動車1001に提供する。ECUコードは、ECU1020に適用されるデータの例である。ECUコードは、ECU1020にインストールされる更新プログラム等のコンピュータプログラムであってもよく、又は、ECU1020に設定されるパラメータ設定値などの設定データであってもよい。
図2は、サーバ装置2000の構成例を示す図である。図2において、サーバ装置2000は、通信部2011と記憶部2012と期待値計算部2013と検証部2014と鍵生成部2015と暗号処理部2016とを備える。通信部2011は、通信回線を介して、他の装置と通信を行う。通信部2011は車両インタフェースに対応する。記憶部2012は、データを記憶する。期待値計算部2013は、ECUコードについての期待値を計算する。検証部2014は、ECU1020の測定値の検証に係る処理を行う。鍵生成部2015は、鍵を生成する。暗号処理部2016は、データの暗号化及び暗号化データの復号を行う。
サーバ装置2000の機能は、該サーバ装置2000が備えるCPU(Central Processing Unit)がコンピュータプログラムを実行することにより実現される。なお、サーバ装置2000として、汎用のコンピュータ装置を使用して構成されてもよく、又は、専用のハードウェア装置として構成されてもよい。
図3は、データ保安装置1010の構成例を示す図である。図3において、データ保安装置1010は、メイン演算器1011とHSM1012とインタフェース部20とを備える。メイン演算器1011は、制御部21と記憶部22とを備える。HSM1012は、記憶部1013と暗号処理部32と測定部33とを備える。
インタフェース部20は、自データ保安装置1010の外部の装置とデータを送受する。インタフェース部20は、CAN1030を介してデータを送受するインタフェースを備える。メイン演算器1011は、インタフェース部20を介して、データ保安装置1010以外の他の装置とデータの送受を行う。
制御部21は、データ保安装置1010の制御を行う。記憶部22は、データを記憶する。記憶部1013は、データを記憶する。暗号処理部32は、データの暗号化及び暗号化データの復号を行う。測定部33は、ECUコード等のデータの測定値を計算し、該測定値を期待値に基づいて検証する。
図4は、ECU1020の構成例を示す図である。図4において、ECU1020は、メイン演算器1021とSHE1022とインタフェース部40とを備える。メイン演算器1021は、制御部41と記憶部42とを備える。SHE1022は、記憶部1023と暗号処理部52と測定部53とを備える。
インタフェース部40は、自ECU1020の外部の装置とデータを送受する。インタフェース部40は、CAN1030を介してデータを送受するインタフェースを備える。メイン演算器1021は、インタフェース部40を介して、自ECU1020以外の他の装置とデータの送受を行う。
制御部41は、ECU1020の制御を行う。記憶部42は、データを記憶する。記憶部1023は、データを記憶する。暗号処理部52は、データの暗号化及び暗号化データの復号を行う。測定部53は、ECUコード等のデータの測定値を計算し、該測定値を期待値に基づいて検証する。
なお、本実施形態では、データ保安装置1010にHSMが使用されているが、データ保安装置1010においてHSMの代わりにSHEが使用されてもよい。なお、SHEについては、例えば非特許文献2に記載されている。
次に図5を参照して、本実施形態に係るデータ提供方法の例を説明する。図5は、本実施形態に係るデータ提供方法の例を示すシーケンスチャートである。
サーバ装置2000は、マスタ鍵Master_Secretと、ECU1020のECUコードとを予め記憶部2012に格納している。ECU1020のECUコードは、ECU1020に適用する予定のECUコードを含む。データ保安装置1010は、署名鍵Kbc及び暗号鍵Kecを予めHSM1012の記憶部1013に格納している。ECU1020は、署名鍵Kbeを予めSHE1022の記憶部1023に格納している。
以下、サーバ装置2000は、通信部2011により、自動車1001のTCU1050と通信を行い、TCU1050及びゲートウェイ1070を介して、自動車1001のCAN1030に接続されるデータ保安装置1010との間でデータを送受する。なお、サーバ装置2000とデータ保安装置1010との間の通信路として、暗号化通信路が使用されてもよい。例えば、サーバ装置2000とデータ保安装置1010は、暗号化通信路の一例として、https(hypertext transfer protocol secure)通信を行ってもよい。
(ステップS101)サーバ装置2000の鍵生成部2015は、自動車1001に搭載されているデータ保安装置1010の署名鍵Kbc及び暗号鍵Kec、並びに、ECU1020の署名鍵Kbeを生成する。
鍵生成部2015の鍵生成方法の例を説明する。鍵生成部2015は、記憶部2012に格納されているマスタ鍵Master_Secretと、鍵生成対象装置の識別子UNIT_IDと、変数Nkとを使用して、次式により鍵(共通鍵)を生成する。
共通鍵=ダイジェスト(Master_Secret、UNIT_ID、Nk)
共通鍵=ダイジェスト(Master_Secret、UNIT_ID、Nk)
但し、鍵生成対象装置がデータ保安装置1010である場合には、UNIT_IDはデータ保安装置1010の識別子SecU_IDである。鍵生成対象装置がECU1020である場合には、UNIT_IDはECU1020の識別子ECU_IDである。ダイジェスト(Master_Secret、UNIT_ID、Nk)は、マスタ鍵Master_Secretと識別子UNIT_IDと変数Nkとから生成されるダイジェスト値である。ダイジェスト値として、例えば、ハッシュ(hash)関数により算出される値、排他的論理和演算により算出される値、又は、CMAC(Cipher-based Message Authentication Code)などが挙げられる。例えば、共通鍵は、マスタ鍵Master_Secretと識別子UNIT_IDと変数Nkとを入力値に使用して算出されるハッシュ関数値である。
変数Nkの値が異なれば、ダイジェスト値は異なる。変数Nkの値を変えることによって、同じマスタ鍵Master_Secretと識別子UNIT_IDとから、異なる共通鍵を生成することができる。例えば、署名鍵用の変数Nkの値をNk_aとし、暗号鍵用の変数Nkの値をNk_bとする。鍵生成部2015は、マスタ鍵Master_Secretと、データ保安装置1010の識別子SecU_IDと、変数Nk_a,Nk_bとを使用して、
署名鍵Kbc=ダイジェスト(Master_Secret、SecU_ID、Nk_a)、
暗号鍵Kec=ダイジェスト(Master_Secret、SecU_ID、Nk_b)、
により、データ保安装置1010の署名鍵Kbcと暗号鍵Kecとを異なる鍵として生成する。また、鍵生成部2015は、マスタ鍵Master_Secretと、ECU1020の識別子ECU_IDと、変数Nk_aとを使用して、
署名鍵Kbe=ダイジェスト(Master_Secret、ECU_ID、Nk_a)、
により、ECU1020の署名鍵Kbeを生成する。記憶部2012は、データ保安装置1010の署名鍵Kbc及び暗号鍵Kec、並びに、ECU1020の署名鍵Kbeを格納する。データ保安装置1010のHSM1012の記憶部1013は、サーバ装置2000と同じ鍵生成方法によって生成された署名鍵Kbc及び暗号鍵Kecを予め格納している。ECU1020のSHE1022の記憶部1023は、サーバ装置2000と同じ鍵生成方法によって生成された署名鍵Kbeを予め格納している。
なお、本実施形態に係る鍵(共通鍵)の生成方法の他の例として、署名鍵をハッシュ関数により算出される値とし、暗号鍵を排他的論理和演算により算出される値としてもよい。又は、その逆、つまり、署名鍵を排他的論理和演算により算出される値とし、暗号鍵をハッシュ関数により算出される値としてもよい。
(ステップS102)サーバ装置2000の期待値計算部2013は、自動車1001に搭載されているECU1020に適用する予定のECUコードのCMACを、データ保安装置1010の署名鍵Kbcにより計算する。この計算結果のCMACは、該ECUコードについての期待値である。なお、本実施形態では、ECUコードの測定値の一例として、CMACを使用する。期待値計算部2013が計算したECUコードの期待値(CMAC)は、該ECUコードの測定値(CMAC)の検証に使用される。記憶部2012は、ECUコードの期待値(CMAC)を格納する。
(ステップS103)サーバ装置2000は、通信部2011により、ECU1020に適用されるECUコードと、期待値計算部2013が計算した期待値(CMAC)とを、データ保安装置1010に送信する。データ保安装置1010は、サーバ装置2000から送信された、ECUコードと期待値(CMAC)とを受信する。
(ステップS104)データ保安装置1010の制御部21は、サーバ装置2000から受信した期待値のCMACをHSM1012に渡し、該CMACをHSM1012における測定値の期待値に設定する。制御部21は、サーバ装置2000から受信したECUコードをHSM1012に渡し、HSM1012にECUコードの測定を実行させる。HSM1012の測定部33は、記憶部1013に格納している署名鍵Kbcにより、ECUコードの測定値を計算する。本実施形態では、測定値の一例としてCMACを使用する。
よって、測定部33は、記憶部1013に格納している署名鍵Kbcにより、ECUコードのCMACを計算する。
よって、測定部33は、記憶部1013に格納している署名鍵Kbcにより、ECUコードのCMACを計算する。
測定部33は、期待値のCMACと、計算した測定値のCMACとを比較する。この比較の結果、両者が一致する場合には測定値(CMAC)の検証が合格であり、両者が一致しない場合には測定値(CMAC)の検証が不合格である。HSM1012は、測定値の検証結果「合格又は不合格」を制御部21に渡す。制御部21は、ECUコードの測定値の検証結果が合格である場合に、ステップS105に処理を進める。一方、制御部21は、ECUコードの測定値の検証結果が不合格である場合には、図5の処理を終了する。
なお、ECUコードの測定値の検証結果が不合格である場合には、制御部21は、所定のエラー処理を実行してもよい。例えば、制御部21は、ECUコードの測定値の検証結果が不合格であることを示すエラーメッセージを、サーバ装置2000に送信してもよい。サーバ装置2000は、該エラーメッセージに応じて、所定のエラー処理を実行してもよい。例えば、サーバ装置2000は、ECUコードと期待値(CMAC)とをデータ保安装置1010に再送信したり、又は、期待値(CMAC)を再生成してデータ保安装置1010に送信したりしてもよい。
(ステップS105)データ保安装置1010の制御部21は、ECUコードの測定値の検証が合格したECUコードを、インタフェース部20によりECU1020に送信する。ECU1020は、データ保安装置1010から送信されたECUコードを受信する。
(ステップS106)ECU1020の制御部41は、データ保安装置1010から受信したECUコードを自ECU1020に適用する。
(ステップS107)ECU1020の制御部41は、ECUコードの適用後に、セキュアブートを実行する。このセキュアブートでは、SHE1022の測定部53は、記憶部1023に格納している署名鍵KbeによりECUコードの測定値を計算する。本実施形態では、測定値の一例として、CMACを使用する。よって、測定部53は、記憶部1023に格納している署名鍵Kbeにより、ECUコードのCMACを計算する。測定部53は、該計算結果のCMACと期待値との比較を行う。制御部41は、セキュアブートの実行前に、予め、期待値をSHE1022に設定する。該計算結果のCMACと期待値との比較の結果、両者が一致する場合にはセキュアブート結果が合格であり、両者が一致しない場合にはセキュアブート結果が不合格である。SHE1022は、セキュアブート結果を制御部41に渡す。制御部41は、セキュアブート結果が合格である場合にECUコードの実行を進める。一方、制御部41は、セキュアブート結果が不合格である場合にはECUコードの実行を停止する。
なお、ECU1020のセキュアブートで使用される期待値は、サーバ装置2000又はデータ保安装置1010からECU1020に予め供給される。サーバ装置2000がECU1020にセキュアブートで使用される期待値を供給する場合、サーバ装置2000の期待値計算部2013がECU1020の署名鍵KbeによりECUコードの期待値(CMAC)を計算する。ECU1020の署名鍵Kbeは、予め、ECU1020とサーバ装置2000間で共有される。また、サーバ装置2000は、「ECU1020のセキュアブートで使用される期待値(CMAC)」の期待値(CMAC)を、上記ステップS102と同様にデータ保安装置1010の署名鍵Kbcにより計算する。そして、サーバ装置2000は、この計算結果のCMACと「ECU1020のセキュアブートで使用される期待値(CMAC)」とを上記ステップS103と同様にデータ保安装置1010に送信してもよい。データ保安装置1010は、サーバ装置2000から受信した「ECU1020のセキュアブートで使用される期待値(CMAC)」と該期待値のCMACについて、上記ステップS104と同様に、自己の署名鍵Kbcにより検証を行う。データ保安装置1010は、上記ステップS105と同様に、該検証が合格した場合に、サーバ装置2000から受信した「ECU1020のセキュアブートで使用される期待値(CMAC)」をECU1020に送信する。「ECU1020のセキュアブートで使用される期待値(CMAC)」は、ECU1020に適用されるデータの例である。
一方、データ保安装置1010がECU1020にセキュアブートで使用される期待値を供給する場合には、データ保安装置1010は、期待値計算部を有し、ECU1020の署名鍵KbeによりECUコードの期待値(CMAC)を計算する。ECU1020の署名鍵Kbeは、予め、ECU1020とデータ保安装置1010間で共有される。
(ステップS108)ECU1020の制御部41は、インタフェース部40により、セキュアブート結果「合格又は不合格」をデータ保安装置1010に送信する。データ保安装置1010は、ECU1020から受信したセキュアブート結果「合格又は不合格」をサーバ装置2000に転送する。セキュアブート結果「合格又は不合格」は、ECUコードのECU1020への適用の合否を示すデータ適用結果に対応する。
サーバ装置2000は、通信部2011により、データ保安装置1010から送信されたセキュアブート結果「合格又は不合格」を受信する。サーバ装置2000は、データ保安装置1010から受信したセキュアブート結果「合格又は不合格」に応じて、所定の処理を実行する。例えば、セキュアブート結果が合格である場合には、その旨を記録する。
一方、セキュアブート結果が不合格である場合には、サーバ装置2000は、所定のエラー処理を実行してもよい。例えば、エラー処理として、サーバ装置2000は、ECUコードと期待値(CMAC)とをデータ保安装置1010に再送信したり、又は、期待値(CMAC)を再生成してデータ保安装置1010に送信したりしてもよい。また、該エラー処理を、セキュアブート結果が合格になるまで繰り返す、又は、所定回数だけ繰り返してもよい。
一方、セキュアブート結果が不合格である場合には、サーバ装置2000は、所定のエラー処理を実行してもよい。例えば、エラー処理として、サーバ装置2000は、ECUコードと期待値(CMAC)とをデータ保安装置1010に再送信したり、又は、期待値(CMAC)を再生成してデータ保安装置1010に送信したりしてもよい。また、該エラー処理を、セキュアブート結果が合格になるまで繰り返す、又は、所定回数だけ繰り返してもよい。
なお、上記したステップS107のECUコードの適用後のセキュアブートは、必須ではなく、実行しなくてもよい。
次に、上述した図5のデータ提供方法の変形例を説明する。
<データ提供方法の変形例1>
ステップS103において、サーバ装置2000は、暗号処理部2016によりECUコードを暗号化して、データ保安装置1010に送信する。この暗号化に用いる鍵は、データ保安装置1010の暗号鍵Kecである。データ保安装置1010は、サーバ装置2000から受信した暗号化データを、HSM1012の暗号処理部32により、記憶部1013に格納されている暗号鍵Kecで復号して、ECUコードを取得する。
ステップS103において、サーバ装置2000は、暗号処理部2016によりECUコードを暗号化して、データ保安装置1010に送信する。この暗号化に用いる鍵は、データ保安装置1010の暗号鍵Kecである。データ保安装置1010は、サーバ装置2000から受信した暗号化データを、HSM1012の暗号処理部32により、記憶部1013に格納されている暗号鍵Kecで復号して、ECUコードを取得する。
<データ提供方法の変形例2>
ステップS105において、データ保安装置1010は、HSM1012の暗号処理部32によりECUコードを暗号化して、ECU1020に送信する。この暗号化に用いる鍵は、予め、データ保安装置1010とECU1020間で共有される。ECU1020は、データ保安装置1010から受信した暗号化データを、SHE1022の暗号処理部52により、記憶部1023に格納されている該当の鍵で復号して、ECUコードを取得する。
ステップS105において、データ保安装置1010は、HSM1012の暗号処理部32によりECUコードを暗号化して、ECU1020に送信する。この暗号化に用いる鍵は、予め、データ保安装置1010とECU1020間で共有される。ECU1020は、データ保安装置1010から受信した暗号化データを、SHE1022の暗号処理部52により、記憶部1023に格納されている該当の鍵で復号して、ECUコードを取得する。
<データ提供方法の変形例3>
ステップS105において、ECUコードは、CAN1030のパケットに格納されて、データ保安装置1010からECU1020に伝送される。データ保安装置1010は、該パケットに、該パケットについてのCMACをさらに含める。該CMACの生成に使用する鍵は、予め、データ保安装置1010とECU1020間で共有される。ECU1020は、データ保安装置1010から受信したパケットに含まれるCMACを、該当の鍵で検証する。ECU1020は、該CMACの検証が合格した場合に当該ECUコードを適用する。一方、ECU1020は、該CMACの検証が不合格である場合には当該ECUコードを適用しない。
ステップS105において、ECUコードは、CAN1030のパケットに格納されて、データ保安装置1010からECU1020に伝送される。データ保安装置1010は、該パケットに、該パケットについてのCMACをさらに含める。該CMACの生成に使用する鍵は、予め、データ保安装置1010とECU1020間で共有される。ECU1020は、データ保安装置1010から受信したパケットに含まれるCMACを、該当の鍵で検証する。ECU1020は、該CMACの検証が合格した場合に当該ECUコードを適用する。一方、ECU1020は、該CMACの検証が不合格である場合には当該ECUコードを適用しない。
なお、ECUコードを格納するパケットに含めるCMACとして、該ECUコードの全て又は一部についてのCMACが使用されてもよい。例えば、データ保安装置1010は、ECUコードを一定サイズのブロックに分割し、ブロック毎にCMACを計算して、該ブロックと該CMACとをパケットに格納してもよい。ECU1020は、ブロック毎にCMACを検証しながらECUコードを取得する。該CMACの生成に使用する鍵は、予め、データ保安装置1010とECU1020間で共有される。
<データ提供方法の変形例4>
ステップS108において、ECU1020からサーバ装置2000に送信するセキュアブート結果「合格又は不合格」は所定値とする。例えば、合格は「1」であり、不合格は「0」である。
ステップS108において、ECU1020からサーバ装置2000に送信するセキュアブート結果「合格又は不合格」は所定値とする。例えば、合格は「1」であり、不合格は「0」である。
<データ提供方法の変形例5>
ステップS108において、ECU1020からサーバ装置2000に送信するセキュアブート結果「合格又は不合格」は、ステップS107のセキュアブートで計算された結果のECUコードのCMACとする。サーバ装置2000の検証部2014は、ステップS103でデータ保安装置1010に送信したECUコードのCMACを、ECU1020の署名鍵Kbeにより計算する。サーバ装置2000の検証部2014は、該計算結果のCMACと、ECU1020のセキュアブート結果のCMACとを比較する。サーバ装置2000の検証部2014は、該比較の結果、両者が一致する場合にはECU1020のセキュアブート結果が合格であると判断し、両者が一致しない場合にはECU1020のセキュアブート結果が不合格であると判断する。
ステップS108において、ECU1020からサーバ装置2000に送信するセキュアブート結果「合格又は不合格」は、ステップS107のセキュアブートで計算された結果のECUコードのCMACとする。サーバ装置2000の検証部2014は、ステップS103でデータ保安装置1010に送信したECUコードのCMACを、ECU1020の署名鍵Kbeにより計算する。サーバ装置2000の検証部2014は、該計算結果のCMACと、ECU1020のセキュアブート結果のCMACとを比較する。サーバ装置2000の検証部2014は、該比較の結果、両者が一致する場合にはECU1020のセキュアブート結果が合格であると判断し、両者が一致しない場合にはECU1020のセキュアブート結果が不合格であると判断する。
<データ提供方法の変形例6>
サーバ装置2000は、検証値(例えば、乱数)を予めECU1020に供給する。ステップS108において、ECU1020は、セキュアブート結果が合格である場合にはセキュアブート結果「合格」に検証値を含め、一方、セキュアブート結果が不合格である場合にはセキュアブート結果「不合格」に検証値を含めない。サーバ装置2000の検証部2014は、ECU1020のセキュアブート結果「合格」に含まれる検証値と、予めECU1020に供給した元の検証値とを比較する。サーバ装置2000の検証部2014は、該比較の結果、両者が一致する場合にはECU1020のセキュアブート結果が合格であると判断し、両者が一致しない場合にはECU1020のセキュアブート結果が不合格であると判断する。
サーバ装置2000は、検証値(例えば、乱数)を予めECU1020に供給する。ステップS108において、ECU1020は、セキュアブート結果が合格である場合にはセキュアブート結果「合格」に検証値を含め、一方、セキュアブート結果が不合格である場合にはセキュアブート結果「不合格」に検証値を含めない。サーバ装置2000の検証部2014は、ECU1020のセキュアブート結果「合格」に含まれる検証値と、予めECU1020に供給した元の検証値とを比較する。サーバ装置2000の検証部2014は、該比較の結果、両者が一致する場合にはECU1020のセキュアブート結果が合格であると判断し、両者が一致しない場合にはECU1020のセキュアブート結果が不合格であると判断する。
<データ提供方法の変形例7>
上記のデータ提供方法の変形例4,5,6のいずれか複数を組合せて適用する。
上記のデータ提供方法の変形例4,5,6のいずれか複数を組合せて適用する。
<データ提供方法の変形例8>
上記のデータ提供方法の変形例4,5,6,7において、ECU1020は、SHE1022の暗号処理部52によりセキュアブート結果を暗号化して、サーバ装置2000に送信する。この暗号化に用いる鍵は、予め、サーバ装置2000とECU1020間で共有される。サーバ装置2000は、ECU1020からの暗号化データを、暗号処理部2016により、記憶部2012に格納されている該当の鍵で復号して、セキュアブート結果を取得する。なお、該暗号化に用いる鍵として、セキュアブート結果が合格である場合にのみSHE1022で使用可能となる暗号鍵が、使用されてもよい。この場合、セキュアブート結果「合格」が該暗号鍵により暗号化されてもよい。
上記のデータ提供方法の変形例4,5,6,7において、ECU1020は、SHE1022の暗号処理部52によりセキュアブート結果を暗号化して、サーバ装置2000に送信する。この暗号化に用いる鍵は、予め、サーバ装置2000とECU1020間で共有される。サーバ装置2000は、ECU1020からの暗号化データを、暗号処理部2016により、記憶部2012に格納されている該当の鍵で復号して、セキュアブート結果を取得する。なお、該暗号化に用いる鍵として、セキュアブート結果が合格である場合にのみSHE1022で使用可能となる暗号鍵が、使用されてもよい。この場合、セキュアブート結果「合格」が該暗号鍵により暗号化されてもよい。
次に、上述した図5のデータ提供方法におけるデータ保安装置1010とECU1020間の実施例を説明する。図6から図8は、本実施形態に係るデータ提供方法の実施例を示すフローチャートである。本実施例では、非特許文献3に記載される15章の「Non-volatile server memory programming process」において、「15.2.1.2 Programming stepof phase #1 - Download of application software and data」の手順と、「15.2.1.3Post-Programming step of phase #1 - Re-synchronization of vehicle network」の手順と、を利用する。図6及び図7には、非特許文献3に記載される「15.2.1.2 Programming step of phase #1 - Download of application software and data」の図33の「graphically depicts the functionality embedded in the programming step of phase #1.」における適用例が示されている。図8には、非特許文献3に記載される「15.2.1.3 Post-Programming step of phase #1 - Re-synchronization of vehicle network」の図34の「graphically depicts the functionality embedded in the post-programming step of phase #1.」における適用例が示されている。
図6において、符号S1001で示されるステップは、データ保安装置1010のセキュリティ・アクセス(Security Access)の処理に対応する。図7において、符号S1002で示されるステップは、データ保安装置1010のECUコードのブロック毎の復号及び電子署名の検証の処理に対応する。図7において、符号S1003で示されるステップは、ECU1020のECUコードの検証の処理に対応する。図8において、符号S1004で示されるステップは、ECU1020のECUコードの適用後のセキュアブートの処理に対応する。
上述した実施形態によれば、データ保安装置1010は、サーバ装置2000から提供されたECUコードの期待値(CMAC)に基づいて、該ECUコードの測定値(CMAC)を検証し、この測定値(CMAC)の検証が合格したECUコードをECU1020に送信する。これにより、ECU1020に適用されるECUコードの信頼性を向上させることができる。また、サーバ装置2000がECU1020にセキュアブートで使用される期待値を供給する場合、データ保安装置1010は、ECUコードと同様に、サーバ装置2000から受信した「ECU1020のセキュアブートで使用される期待値」と該期待値の期待値(CMAC)について検証を行う。これにより、ECU1020に適用される「セキュアブートで使用される期待値」の信頼性を向上させることができる。
上述した実施形態において、サーバ装置2000はデータ提供装置に対応する。
なお、メンテナンスツール2100が、サーバ装置2000と同様の機能を備えてもよい。メンテナンスツール2100は、サーバ装置2000と同様のデータ提供方法により、診断ポート1060及びデータ保安装置1010を介してECU1020にECUコードを提供する。
また、自動車1001のTCU1050又はゲートウェイ1070が、データ保安装置1010の機能を有してもよい。
以上、本発明の実施形態について図面を参照して詳述してきたが、具体的な構成はこの実施形態に限られるものではなく、本発明の要旨を逸脱しない範囲の設計変更等も含まれる。
上述した実施形態では、データ保安装置1010やECU1020にHSMやSHEが使用されたが、HSM及びSHE以外の暗号処理チップが使用されてもよい。データ保安装置1010に対して、例えば「TPM(Trusted Platform Module)f」と呼ばれる暗号処理チップが使用されてもよい。TPMfは耐タンパー性を有する。TPMfはセキュアエレメントの例である。ECU1020に対して、例えば「TPMt」と呼ばれる暗号処理チップが使用されてもよい。TPMtは耐タンパー性を有する。TPMtはセキュアエレメントの例である。
上述した実施形態は、自動車の製造工場において、自動車の製造工程で自動車に搭載されたECUに適用されてもよい。また、上述した実施形態は、自動車の整備工場や販売店等において、自動車に搭載されているECUに適用されてもよい。
上述した実施形態では、車両として自動車を例に挙げたが、原動機付自転車や鉄道車両等の自動車以外の他の車両にも適用可能である。
また、上述した各装置の機能を実現するためのコンピュータプログラムをコンピュータ読み取り可能な記録媒体に記録して、この記録媒体に記録されたプログラムをコンピュータシステムに読み込ませ、実行するようにしてもよい。なお、ここでいう「コンピュータシステム」とは、OSや周辺機器等のハードウェアを含むものであってもよい。
また、「コンピュータ読み取り可能な記録媒体」とは、フレキシブルディスク、光磁気ディスク、ROM、フラッシュメモリ等の書き込み可能な不揮発性メモリ、DVD(Digital Versatile Disc)等の可搬媒体、コンピュータシステムに内蔵されるハードディスク等の記憶装置のことをいう。
また、「コンピュータ読み取り可能な記録媒体」とは、フレキシブルディスク、光磁気ディスク、ROM、フラッシュメモリ等の書き込み可能な不揮発性メモリ、DVD(Digital Versatile Disc)等の可搬媒体、コンピュータシステムに内蔵されるハードディスク等の記憶装置のことをいう。
さらに「コンピュータ読み取り可能な記録媒体」とは、インターネット等のネットワークや電話回線等の通信回線を介してプログラムが送信された場合のサーバやクライアントとなるコンピュータシステム内部の揮発性メモリ(例えばDRAM(Dynamic Random Access Memory))のように、一定時間プログラムを保持しているものも含むものとする。
また、上記プログラムは、このプログラムを記憶装置等に格納したコンピュータシステムから、伝送媒体を介して、あるいは、伝送媒体中の伝送波により他のコンピュータシステムに伝送されてもよい。ここで、プログラムを伝送する「伝送媒体」は、インターネット等のネットワーク(通信網)や電話回線等の通信回線(通信線)のように情報を伝送する機能を有する媒体のことをいう。
また、上記プログラムは、前述した機能の一部を実現するためのものであっても良い。
さらに、前述した機能をコンピュータシステムにすでに記録されているプログラムとの組み合わせで実現できるもの、いわゆる差分ファイル(差分プログラム)であっても良い。
また、上記プログラムは、このプログラムを記憶装置等に格納したコンピュータシステムから、伝送媒体を介して、あるいは、伝送媒体中の伝送波により他のコンピュータシステムに伝送されてもよい。ここで、プログラムを伝送する「伝送媒体」は、インターネット等のネットワーク(通信網)や電話回線等の通信回線(通信線)のように情報を伝送する機能を有する媒体のことをいう。
また、上記プログラムは、前述した機能の一部を実現するためのものであっても良い。
さらに、前述した機能をコンピュータシステムにすでに記録されているプログラムとの組み合わせで実現できるもの、いわゆる差分ファイル(差分プログラム)であっても良い。
本発明によれば、ECU等の車載コンピュータに適用されるデータの信頼性を向上させることができるという効果が得られる。
22,42,2012…記憶部、2013…期待値計算部、2014…検証部、32,52,2016…暗号処理部、20,40…インタフェース部、21,41…制御部、33,53…測定部、1001…自動車、1002…車載コンピュータシステム、1010…データ保安装置、1011,1021…メイン演算器、1012…HSM、1013,1023…記憶部、1020…ECU、1022…SHE、1030…CAN、1040…インフォテイメント機器、1050…TCU、1051…通信モジュール、1052…SIM、1060…診断ポート、1070…ゲートウェイ、2000…サーバ装置、2011…通信部、2015…鍵生成部、2100…メンテナンスツール
Claims (8)
- データ提供装置と、車両に搭載されるデータ保安装置とを備え、
前記データ提供装置は、
前記車両とデータを送受する車両インタフェースと、
前記車両に搭載される車載コンピュータに適用される適用データの期待値を計算する期待値計算部と、を備え、前記適用データ及び前記期待値を前記車両インタフェースにより前記車両に送信し、
前記データ保安装置は、
前記データ保安装置の外部の装置とデータを送受するインタフェース部と、
前記インタフェース部により前記データ提供装置から受信した前記適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した前記期待値に基づいて該測定値を検証する測定部と、を備え、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車載コンピュータに送信する、
データ提供システム。 - 前記データ保安装置は、前記インタフェース部により、前記車載コンピュータに送信した前記適用データの前記車載コンピュータへの適用の合否を示すデータ適用結果を前記車載コンピュータから受信して前記データ提供装置へ転送する、
請求項1に記載のデータ提供システム。 - 前記データ保安装置は、前記測定値の検証が合格した前記適用データと、当該適用データについてのメッセージ認証符号とを前記インタフェース部により前記車載コンピュータに送信する、
請求項1又は2のいずれか1項に記載のデータ提供システム。 - 前記メッセージ認証符号は、前記測定値の検証が合格した前記適用データを格納して前記車載コンピュータに伝送するパケットに関するメッセージ認証符号である、
請求項3に記載のデータ提供システム。 - 前記データ保安装置は、前記測定値の検証が合格した前記適用データを複数のブロックに分割し、該ブロック毎に前記メッセージ認証符号を計算し、該ブロックと該メッセージ認証符号とを前記インタフェース部により前記車載コンピュータに送信する、
請求項3又は4のいずれか1項に記載のデータ提供システム。 - 車両に搭載されるデータ保安装置であり、
前記データ保安装置の外部の装置とデータを送受するインタフェース部と、
前記インタフェース部によりデータ提供装置から受信した適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した期待値に基づいて該測定値を検証する測定部と、を備え、
前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車両に搭載される車載コンピュータに送信する、
データ保安装置。 - データ提供装置と、車両に搭載されるデータ保安装置とを備えるデータ提供システムのデータ提供方法であって、
前記データ提供装置が、前記車両に搭載される車載コンピュータに適用される適用データの期待値を計算し、
前記データ提供装置が、前記適用データ及び前記期待値を、前記車両とデータを送受する車両インタフェースにより前記車両に送信し、
前記データ保安装置が、前記データ保安装置の外部の装置とデータを送受するインタフェース部により前記データ提供装置から受信した前記適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した前記期待値に基づいて該測定値を検証し、
前記データ保安装置が、前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車載コンピュータに送信する、
データ提供方法。 - 車両に搭載されるデータ保安装置のコンピュータに、
前記データ保安装置の外部の装置とデータを送受するインタフェース部によりデータ提供装置から受信した適用データの測定値を計算し、前記インタフェース部により前記データ提供装置から受信した期待値に基づいて該測定値を検証し、
前記測定値の検証が合格した前記適用データを前記インタフェース部により前記車両に搭載される車載コンピュータに送信する、
処理を実行させるコンピュータプログラム。
Priority Applications (3)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| CN201780035235.6A CN109314644B (zh) | 2016-08-10 | 2017-03-28 | 数据提供系统、数据保护装置、数据提供方法以及存储介质 |
| US16/307,414 US10970398B2 (en) | 2016-08-10 | 2017-03-28 | Data provision system, data security device, data provision method, and computer program |
| EP17838969.8A EP3499792A4 (en) | 2016-08-10 | 2017-03-28 | DATA PROVIDING SYSTEM, DATA SECURITY DEVICE, DATA PROVIDING METHOD AND COMPUTER PROGRAM |
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2016158121 | 2016-08-10 | ||
| JP2016-158121 | 2016-08-10 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2018029893A1 true WO2018029893A1 (ja) | 2018-02-15 |
Family
ID=61161945
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/JP2017/012720 Ceased WO2018029893A1 (ja) | 2016-08-10 | 2017-03-28 | データ提供システム、データ保安装置、データ提供方法、及びコンピュータプログラム |
Country Status (4)
| Country | Link |
|---|---|
| US (1) | US10970398B2 (ja) |
| EP (1) | EP3499792A4 (ja) |
| CN (1) | CN109314644B (ja) |
| WO (1) | WO2018029893A1 (ja) |
Cited By (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2023505251A (ja) * | 2019-12-06 | 2023-02-08 | アッサ アブロイ アーベー | セキュアな要素をセキュアに更新するための方法及びプロセス |
| JP7698119B1 (ja) | 2024-08-20 | 2025-06-24 | レノボ・シンガポール・プライベート・リミテッド | 情報処理システム、情報処理装置、及びデータ通信方法 |
| JP7891106B1 (ja) * | 2025-04-01 | 2026-07-15 | 財団法人車輌研究測試中心 | 不正なデータ変更を防止できる更新システム及び不正なデータ変更を防止できる更新方法 |
Families Citing this family (7)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN110383755B (zh) * | 2017-01-05 | 2022-04-19 | 皇家飞利浦有限公司 | 网络设备和可信第三方设备 |
| US10841284B2 (en) * | 2018-05-30 | 2020-11-17 | Lear Corporation | Vehicle communication network and method |
| JP7003975B2 (ja) * | 2018-08-10 | 2022-01-21 | 株式会社デンソー | 車両情報通信システム,センター装置及びセンター装置のメッセージ送信方法 |
| CN112422595B (zh) * | 2019-08-20 | 2022-10-11 | 华为技术有限公司 | 车载系统安全保护方法及设备 |
| DE102019212958B3 (de) * | 2019-08-28 | 2021-03-04 | Volkswagen Aktiengesellschaft | Verfahren und Vorrichtung zur Erzeugung von kryptographischen Schlüsseln nach einem Schlüsselableitungsmodell sowie Fahrzeug |
| CN111881015B (zh) * | 2020-06-19 | 2024-02-02 | 无锡融卡科技有限公司 | 应用测试方法与应用测试装置 |
| EP4727190A1 (en) * | 2024-10-11 | 2026-04-15 | Nxp B.V. | Architecture, vehicle and method for configuring a vehicle |
Citations (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US20120093312A1 (en) * | 2010-10-15 | 2012-04-19 | Infineon Technologies Ag | Data Transmitter with a Secure and Efficient Signature |
| JP2013192091A (ja) * | 2012-03-14 | 2013-09-26 | Denso Corp | 通信システム、中継装置、車外装置及び通信方法 |
| JP2016072675A (ja) * | 2014-09-26 | 2016-05-09 | Kddi株式会社 | 管理装置、車両、管理方法およびコンピュータプログラム |
Family Cites Families (17)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JPH11205308A (ja) | 1997-10-29 | 1999-07-30 | Hitachi Ltd | 認証方法および情報システム |
| US7068147B2 (en) | 1999-12-07 | 2006-06-27 | Denso Corporation | Control information rewriting system |
| US7853336B2 (en) * | 2007-02-27 | 2010-12-14 | Rockwell Automation Technologies, Inc. | Dynamic versioning utilizing multiple controller engine instances to limit complications |
| JP2008239021A (ja) | 2007-03-28 | 2008-10-09 | Denso Corp | 車両制御装置及びそのデータ書換システム |
| US9464905B2 (en) | 2010-06-25 | 2016-10-11 | Toyota Motor Engineering & Manufacturing North America, Inc. | Over-the-air vehicle systems updating and associate security protocols |
| ES2446974T3 (es) | 2011-02-08 | 2014-03-11 | Delphi Technologies Holding S.À.R.L. | Método y aparato para la seguridad de vehículos |
| JP5438051B2 (ja) | 2011-03-07 | 2014-03-12 | 株式会社東海理化電機製作所 | 電子キーシステム |
| BR112013024684B1 (pt) | 2011-03-29 | 2021-08-17 | Volvo Lastvagnar Ab | Pacote de dados de reparo assegurado |
| CN102495601A (zh) | 2011-12-12 | 2012-06-13 | 深圳市航盛电子股份有限公司 | 一种跨网络电控单元的软件刷新系统及方法 |
| DE102013101508B4 (de) | 2012-02-20 | 2024-10-02 | Denso Corporation | Datenkommunikationsauthentifizierungssystem für ein Fahrzeug und Netzkopplungsvorrichtung für ein Fahrzeug |
| US10038565B2 (en) | 2012-12-20 | 2018-07-31 | GM Global Technology Operations LLC | Methods and systems for bypassing authenticity checks for secure control modules |
| JP2014182571A (ja) | 2013-03-19 | 2014-09-29 | Denso Corp | 車載電子制御装置のプログラム書換システム及び車載中継装置 |
| JP5975964B2 (ja) * | 2013-10-18 | 2016-08-23 | 富士通株式会社 | 情報処理プログラム、情報処理方法、情報処理装置、及び情報処理システム |
| CN104579664B (zh) | 2013-10-25 | 2017-12-19 | 成都国恒信息安全技术有限责任公司 | 可有效保障数据安全的移动警务终端及其使用方法 |
| JP5949732B2 (ja) | 2013-11-27 | 2016-07-13 | 株式会社オートネットワーク技術研究所 | プログラム更新システム及びプログラム更新方法 |
| JP6188672B2 (ja) | 2014-10-29 | 2017-08-30 | Kddi株式会社 | 鍵管理システム |
| CN104601329B (zh) * | 2014-12-26 | 2018-10-26 | 深圳市金溢科技股份有限公司 | 车载终端、车辆信息发布系统及方法 |
-
2017
- 2017-03-28 US US16/307,414 patent/US10970398B2/en not_active Expired - Fee Related
- 2017-03-28 CN CN201780035235.6A patent/CN109314644B/zh not_active Expired - Fee Related
- 2017-03-28 EP EP17838969.8A patent/EP3499792A4/en not_active Withdrawn
- 2017-03-28 WO PCT/JP2017/012720 patent/WO2018029893A1/ja not_active Ceased
Patent Citations (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US20120093312A1 (en) * | 2010-10-15 | 2012-04-19 | Infineon Technologies Ag | Data Transmitter with a Secure and Efficient Signature |
| JP2013192091A (ja) * | 2012-03-14 | 2013-09-26 | Denso Corp | 通信システム、中継装置、車外装置及び通信方法 |
| JP2016072675A (ja) * | 2014-09-26 | 2016-05-09 | Kddi株式会社 | 管理装置、車両、管理方法およびコンピュータプログラム |
Non-Patent Citations (3)
| Title |
|---|
| KEISUKE TAKEMORI ET AL.: "Key Managements for ECU and Code Authentications Using Tamper- resistant Secure Element", IEICE TECHNICAL REPORT, vol. 115, no. 366, 10 December 2015 (2015-12-10), pages 227 - 232, XP055586088 * |
| KEISUKE TAKEMORI ET AL.: "Protection for Automotive Control System Using Secure Boot and Authentication", IEICE TECHNICAL REPORT, vol. 114, no. 225, 12 September 2014 (2014-09-12), pages 47 - 54, XP008182241 * |
| See also references of EP3499792A4 * |
Cited By (8)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2023505251A (ja) * | 2019-12-06 | 2023-02-08 | アッサ アブロイ アーベー | セキュアな要素をセキュアに更新するための方法及びプロセス |
| JP7429780B2 (ja) | 2019-12-06 | 2024-02-08 | アッサ アブロイ アーベー | セキュアな要素をセキュアに更新するための方法及びプロセス |
| JP2025016650A (ja) * | 2019-12-06 | 2025-02-04 | アッサ アブロイ アーベー | セキュアな要素をセキュアに更新するための方法及びプロセス |
| US12443717B2 (en) | 2019-12-06 | 2025-10-14 | Assa Abloy Ab | Methods and processes to securely update secure elements |
| JP7785897B2 (ja) | 2019-12-06 | 2025-12-15 | アッサ アブロイ アーベー | セキュアな要素をセキュアに更新するための方法及びプロセス |
| JP7698119B1 (ja) | 2024-08-20 | 2025-06-24 | レノボ・シンガポール・プライベート・リミテッド | 情報処理システム、情報処理装置、及びデータ通信方法 |
| JP2026036400A (ja) * | 2024-08-20 | 2026-03-05 | レノボ・シンガポール・プライベート・リミテッド | 情報処理システム、情報処理装置、及びデータ通信方法 |
| JP7891106B1 (ja) * | 2025-04-01 | 2026-07-15 | 財団法人車輌研究測試中心 | 不正なデータ変更を防止できる更新システム及び不正なデータ変更を防止できる更新方法 |
Also Published As
| Publication number | Publication date |
|---|---|
| CN109314644B (zh) | 2021-08-27 |
| EP3499792A4 (en) | 2020-01-01 |
| US10970398B2 (en) | 2021-04-06 |
| US20190347421A1 (en) | 2019-11-14 |
| EP3499792A1 (en) | 2019-06-19 |
| CN109314644A (zh) | 2019-02-05 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| JP6260067B1 (ja) | 管理システム、鍵生成装置、車載コンピュータ、管理方法、及びコンピュータプログラム | |
| US11265170B2 (en) | Vehicle information collection system, vehicle-mounted computer, vehicle information collection device, vehicle information collection method, and computer program | |
| US10970398B2 (en) | Data provision system, data security device, data provision method, and computer program | |
| US11212109B2 (en) | Data provision system, data security device, data provision method, and computer program | |
| JP6683588B2 (ja) | 再利用システム、サーバ装置、再利用方法、及びコンピュータプログラム | |
| JP6197000B2 (ja) | システム、車両及びソフトウェア配布処理方法 | |
| JP6288219B1 (ja) | 通信システム | |
| WO2017115751A1 (ja) | 車載コンピュータシステム、車両、管理方法、及びコンピュータプログラム | |
| JP2017046038A (ja) | 車載コンピュータシステム、車両、管理方法、及びコンピュータプログラム | |
| JP6260068B1 (ja) | 保守装置、保守方法、及びコンピュータプログラム | |
| JP2018082439A (ja) | 通信システム、車両、サーバ装置、通信方法、及びコンピュータプログラム | |
| JP6299039B2 (ja) | 車両情報収集システム、データ保安装置、車両情報収集方法、及びコンピュータプログラム | |
| JP2018057044A (ja) | 車両情報収集システム、データ保安装置、車両情報収集装置、車両情報収集方法、及びコンピュータプログラム | |
| JP6203798B2 (ja) | 車載制御システム、車両、管理装置、車載コンピュータ、データ共有方法、及びコンピュータプログラム | |
| JP6554704B2 (ja) | データ提供システム及びデータ提供方法 | |
| JP6464466B2 (ja) | 保守装置、保守方法、及びコンピュータプログラム | |
| JP6354099B2 (ja) | データ提供システム及びデータ提供方法 | |
| JP6454919B2 (ja) | 管理システム、データ提供装置、車載コンピュータ、管理方法、及びコンピュータプログラム | |
| WO2018131270A1 (ja) | 通信システム、車両、サーバ装置、通信方法、及びコンピュータプログラム | |
| JP2017225186A (ja) | 車載制御システム、車両、管理装置、車載コンピュータ、データ共有方法、及びコンピュータプログラム | |
| JP2017208731A (ja) | 管理システム、管理装置、車載コンピュータ、管理方法、及びコンピュータプログラム |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 17838969 Country of ref document: EP Kind code of ref document: A1 |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| ENP | Entry into the national phase |
Ref document number: 2017838969 Country of ref document: EP Effective date: 20190311 |