WO2020262456A1 - 実行コード提供方法およびソフトウェア開発システム - Google Patents
実行コード提供方法およびソフトウェア開発システム Download PDFInfo
- Publication number
- WO2020262456A1 WO2020262456A1 PCT/JP2020/024799 JP2020024799W WO2020262456A1 WO 2020262456 A1 WO2020262456 A1 WO 2020262456A1 JP 2020024799 W JP2020024799 W JP 2020024799W WO 2020262456 A1 WO2020262456 A1 WO 2020262456A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- intermediate representation
- execution
- code
- software development
- execution code
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Images


Classifications
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F21/00—Security arrangements for protecting computers, components thereof, programs or data against unauthorised activity
- G06F21/50—Monitoring users, programs or devices to maintain the integrity of platforms, e.g. of processors, firmware or operating systems
- G06F21/51—Monitoring users, programs or devices to maintain the integrity of platforms, e.g. of processors, firmware or operating systems at application loading time, e.g. accepting, rejecting, starting or inhibiting executable software based on integrity or source reliability
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F8/00—Arrangements for software engineering
- G06F8/40—Transformation of program code
- G06F8/41—Compilation
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F8/00—Arrangements for software engineering
- G06F8/60—Software deployment
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F9/00—Arrangements for program control, e.g. control units
- G06F9/06—Arrangements for program control, e.g. control units using stored programs, i.e. using an internal store of processing equipment to receive or retain programs
- G06F9/44—Arrangements for executing specific programs
- G06F9/445—Program loading or initiating
- G06F9/44589—Program code verification, e.g. Java bytecode verification, proof-carrying code
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F2221/00—Indexing scheme relating to security arrangements for protecting computers, components thereof, programs or data against unauthorised activity
- G06F2221/03—Indexing scheme relating to G06F21/50, monitoring users, programs or devices to maintain the integrity of platforms
- G06F2221/033—Test or assess software
Definitions
- This disclosure relates to an execution code providing method and a software development system.
- ICT Information and Communication Technology
- edge devices With the intelligentization of devices used in IoT (also referred to as "edge devices"), various types of application programs can be executed on edge devices. On the other hand, it is not easy to increase the safety of edge devices to the same level as the safety of servers and personal computers due to resource constraints. Therefore, verification of application programs incorporated in edge devices becomes important.
- Patent Document 1 discloses an improvement of a static analysis tool for verifying vulnerabilities of Web applications at the source code level.
- Application programs used in edge devices, etc. are often distributed as intermediate representations before execution code generation, not in the form of source code.
- By adopting such an intermediate representation there is an advantage that the know-how contained in the source code can be concealed and the amount of data can be reduced.
- Patent Document 1 As disclosed in Patent Document 1 described above, it is common to analyze the source code and evaluate security holes and vulnerabilities, but evaluate security holes and vulnerabilities in a format other than the source code. It's not easy.
- a typical purpose of the present disclosure is to provide a solution that can guarantee the security of an application program, which is suitable for edge devices and the like.
- the execution code providing method is a step of creating a source code according to a user operation, a step of generating an intermediate representation from the source code, and verifying whether or not the intermediate representation satisfies a predetermined rule or convention. And the step of realizing the execution of the execution code generated from the intermediate representation when the intermediate representation satisfies a predetermined rule or convention.
- the step of realizing the execution of the execution code may include a step of generating the execution code from the intermediate representation, provided that the intermediate representation satisfies a predetermined rule or convention.
- the step of realizing the execution of the execution code may include a step of permitting the execution of the execution code generated from the intermediate representation, provided that the intermediate representation satisfies a predetermined rule or convention.
- the method of providing the executable code further includes a step of evaluating the validity of the executable code based on the certificate issued in association with the intermediate representation that generated the executable code when the controller in which the executable code is executed is started. You may be.
- the verification step includes issuing a certificate associated with the intermediate representation when the intermediate representation meets certain rules or conventions, and the step allowing execution of the executable code generated from the intermediate representation is It may include a step to decide whether or not to execute based on the certificate.
- the verification step may include a step of notifying the user of the content that does not meet the predetermined rule or rule when the intermediate representation does not meet the predetermined rule or rule.
- a software development system includes a software development device that supports the creation of source code and a verification server that can be accessed from the software development device.
- Software development equipment includes means for generating intermediate representations from source code.
- the verification server includes means for verifying whether the intermediate representation meets a predetermined rule or convention. Execution of the execution code generated from the intermediate representation is realized when the intermediate representation satisfies a predetermined rule or convention.
- the intermediate representation 20 itself generated from the source code 10 is verified, and the corresponding execution code 30 is generated or the generated execution code 30 is generated on condition that the verification result is appropriate. Allow execution of.
- the verification of the intermediate representation 20 it is determined that the intermediate representation 20 is appropriate when it satisfies a predetermined rule or convention.
- the "intermediate representation” is a machine for a specific virtual machine in which source code written in an arbitrary programming language (usually a high-level language) is generated by targeting a specific virtual machine in a compiler platform. Including words.
- the "intermediate representation” does not necessarily have to be in binary format, and may be expressed in a format similar to natural language such as assembler language. Further, the “intermediate representation” may adopt any representation format as long as it is generated by targeting a specific virtual machine.
- the "intermediate representation” is generated independently of the platform and architecture on which the executable code 30 is executed.
- a static compiler may be used to generate the intermediate representation 20 from the source code 10.
- the "intermediate representation” may be compiled as executable code 30 directed to a particular platform and architecture.
- the “intermediate representation” and “execution code” are generated as a set.
- the “intermediate representation” can reduce the amount of data as compared with the original source code, and can also improve the efficiency of the described processing itself.
- the generation of the intermediate representation 20 from the source code 10 is basically a one-way conversion, and it is difficult to completely restore the source code 10 from the intermediate representation 20. It is also possible to convert between the intermediate representation 20 and the execution code 30 in both directions.
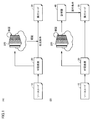
- FIG. 1 is a diagram for explaining an outline of processing in the software development system 1 according to the present embodiment.
- FIG. 1A shows an example in which the successful verification of the intermediate representation 20 generated from the source code 10 is used as the generation condition of the execution code 30.
- FIG. 1B shows an example in which the successful verification of the intermediate representation 20 generated from the source code 10 is used as the execution condition of the execution code 30 generated from the intermediate representation 20.
- the intermediate representation 20 generated from the source code 10 is verified by an arbitrary subject.
- the verification server 200 verifies the intermediate representation 20 is shown, but the present invention is not limited to this, and verification may be performed by any subject.
- the verification server 200 gives authentication to the intermediate representation 20.
- Execution code 30 is generated from the intermediate representation 20 with authentication for the intermediate representation 20 as a generation condition.
- the verification for the intermediate representation 20 may be included in the generation condition of the execution code 30.
- the safety of the generated execution code 30 can be enhanced.
- the verification server 200 issues a certificate 40 including authentication for the intermediate representation 20.
- the execution code 30 is generated from the intermediate representation 20. Execution of the generated execution code 30 may be conditional on the existence of the corresponding certificate 40. In this way, the existence of the certificate 40 for the intermediate representation 20 may be included in the execution condition of the execution code 30. By adopting such an execution condition, it is possible to reduce the possibility that the execution code 30 is executed in a state where the safety is impaired.
- the execution code 30 corresponding to the intermediate representation 20 Authentication is given to allow generation or execution.
- the intermediate representation 20 does not satisfy a predetermined rule or convention (when the verification result is inappropriate)
- authentication is not given and the execution code 30 corresponding to the intermediate representation 20 is generated or executed.
- the intermediate representation 20 satisfies a predetermined rule or convention, the execution of the execution code 30 generated from the intermediate representation 20 is realized.
- the execution code 30 is generated from the intermediate representation 20 on the condition that the intermediate representation 20 satisfies a predetermined rule or convention. Processing may be adopted.
- the execution generated from the intermediate representation 20 is performed on the condition that the intermediate representation 20 satisfies a predetermined rule or convention.
- a process that allows execution of the code 30 may be adopted. At this time, whether or not to permit the execution of the execution code 30 generated from the intermediate representation 20 may be determined based on the certificate 40 associated with the intermediate representation 20. Whether or not execution is possible may be determined by the execution environment of the execution code 30 (processor or microcomputer including the processor).
- the safety included in the application program is determined while the know-how and the like included in the source code 10 are concealed. Risks can be discovered more efficiently. Further, by verifying the intermediate representation 20, it is not necessary to prepare a plurality of verification rule sets according to the type of programming language used in the description of the source code 10, and efficient verification can be realized.
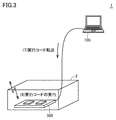
- FIGS. 2 and 3 are diagrams showing an outline of a procedure for generating an execution code 30 from a source code 10 in the software development system 1 according to the present embodiment.
- the software development system 1 includes one or more software development devices 100 and a verification server 200 accessible from the software development device 100 via the Internet 2 or the like.
- the software development device 100 supports the creation of an application program executed by the controller 300 included in the edge device 4.
- the technical scope of the present invention is not limited to the creation of an application program executed by the edge device 4, and can be applied to the creation of an application program executed by any computing device.
- the software development device 100 is provided with an integrated development environment (IDE: Integrated Development Environment), and a user can create an arbitrary application program on the integrated development environment.
- IDE integrated Development Environment
- the controller 300 included in the edge device 4 is an example of a computing device and includes a processor.
- the edge device 4 may be any device, but typically, factory equipment, various household devices, social infrastructure equipment, mobile objects such as vehicles, arbitrary portable devices, and the like are assumed. .. As will be described later, the controller 300 has a processor and can execute an application program from the software development device 100.
- the user creates a source code using the software development device 100 ((1) source code creation). Then, the created source code is compiled in the software development apparatus 100 to generate the intermediate representation 20 ((2) intermediate representation generation).
- the intermediate representation 20 is verified before the execution code 30 is generated from the intermediate representation 20.
- the generated intermediate representation 20 is transmitted to the verification server 200 ((3) intermediate representation verification request).
- the verification server 200 verifies the intermediate representation 20 from the software development device 100 ((4) verification of the intermediate representation).
- the verification server 200 responds to the software development device 100 with the verification result. If the target intermediate representation 20 passes all the verifications, the verification server 200 sends an authentication indicating that the verification results are appropriate to the software development device 100.
- the software development device 100 When the software development device 100 receives the authentication indicating that the verification result is appropriate from the verification server 200 ((5) reception of the verification result (authentication)), the software development device 100 generates the execution code 30 from the intermediate representation 20 ((6)). Execution code generation).
- the software development device 100 transfers the generated execution code 30 to the controller 300 of the edge device 4 ((7) execution code transfer). Then, the controller 300 of the edge device 4 executes the transferred execution code 30 as needed ((8) Execution of the execution code).
- a secure application program can be executed in the controller 300 of the edge device 4 by a series of processes as shown in FIGS. 2 and 3.
- the software development device 100 is typically realized by a general-purpose computer.
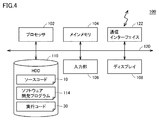
- FIG. 4 is a schematic diagram showing a hardware configuration example of the software development device 100 according to the present embodiment.
- the software development apparatus 100 includes a processor 102, a main memory 104, an input unit 106, a display 108, a hard disk 110, and a communication interface 122 as main components. These components are connected via the internal bus 120.
- the processor 102 is composed of, for example, a CPU (Central Processing Unit) or a GPU (Graphics Processing Unit). A plurality of processors 102 may be arranged, or a processor 102 having a plurality of cores may be adopted.
- a CPU Central Processing Unit
- GPU Graphics Processing Unit
- the main memory 104 is composed of volatile storage devices such as DRAM (Dynamic Random Access Memory) and SRAM (Static Random Access Memory).
- the hard disk 110 holds various programs and various data executed by the processor 102.
- a non-volatile storage device such as an SSD (Solid State Drive) or a flash memory may be adopted.
- the specified program code is expanded on the main memory 104
- the processor 102 is computer-readable instructions included in the program code expanded on the main memory 104. By sequentially executing, various functions as described later are realized.
- the hard disk 110 stores a source code 10 arbitrarily created by the user, a software development program 114 for realizing an integrated development environment, and an execution code 30 generated from the source code 10. .
- the software development program 114 generates an execution code 30 from a source code 10 arbitrarily created by a user via an intermediate representation 20, and includes a module that provides a development environment for an application program. However, the generation or execution of the corresponding execution code 30 is permitted provided that the result of verifying the intermediate representation 20 is appropriate.
- the input unit 106 accepts an input operation of a user who operates the software development device 100.
- the input unit 106 may be, for example, a keyboard, a mouse, a touch panel arranged on the display device, an operation button arranged in the housing of the software development device 100, or the like.
- the display 108 displays the processing result of the processor 102 and the like.
- the display 108 may be, for example, an LCD (Liquid Crystal Display) or an organic EL (Electro-Luminescence) display.
- the communication interface 122 is in charge of exchanging data with the verification server 200.
- the communication interface 122 may include, for example, an Ethernet® port for communication over the Internet.
- the software development device 100 may be realized by using a hard-wired circuit such as an ASIC (Application Specific Integrated Circuit) in which a circuit corresponding to a computer-readable instruction is incorporated. Further, it may be realized by using a circuit corresponding to a computer-readable instruction on FPGA (field-programmable gate array). Further, the processor 102, the main memory, the ASIC, the FPGA, and the like may be combined as appropriate.
- ASIC Application Specific Integrated Circuit
- FPGA field-programmable gate array
- the media may be, for example, an optical media such as a DVD (Digital Versatile Disc), a semiconductor media such as a USB memory, or the like.
- the software development program 114 may not only be installed in the software development device 100 via media, but may also be provided from a distribution server on the network.
- the verification server 200 is also typically realized by a general-purpose computer.
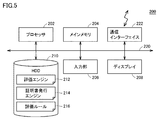
- FIG. 5 is a schematic diagram showing a hardware configuration example of the verification server 200 according to the present embodiment.
- the verification server 200 includes one or more processors 202, a main memory 204, an input unit 206, a display 208, a hard disk 210, and a communication interface 222 as main components. These components are connected via an internal bus 220.
- the processor 202 is composed of, for example, a CPU or a GPU.
- a plurality of processors 202 may be arranged, or a processor 202 having a plurality of cores may be adopted.
- the main memory 204 is composed of a volatile storage device such as DRAM or SRAM.
- the hard disk 210 holds various programs and various data executed by the processor 202. Instead of the hard disk 210, a non-volatile storage device such as an SSD or a flash memory may be adopted.
- the specified program code is expanded on the main memory 204, and the processor 202 sequentially executes computer-readable instructions included in the program code expanded on the main memory 204. , Realize various functions as described later.
- the hard disk 210 has an evaluation engine 212 for executing evaluation processing in response to an external request and a certificate issuing engine 214 for issuing a certificate according to the evaluation result by the evaluation engine 212.
- the evaluation rule 216 used for the evaluation process by the evaluation engine 212 are stored.
- the evaluation engine 212 verifies whether or not the intermediate representation 20 satisfies a predetermined rule or convention.
- the certificate issuing engine 214 issues the certificate 40 associated with the intermediate representation 20 when the intermediate representation 20 satisfies a predetermined rule or convention. Details such as the operation and data structure of these elements will be described later.
- the input unit 206 accepts an input operation of a user who operates the controller 300.
- the display 208 displays the processing result of the processor 202 and the like.
- the communication interface 222 is in charge of exchanging data with the software development device 100.
- the communication interface 222 may include, for example, an Ethernet® port for communication over the Internet.
- the verification server 200 may be realized by using a hard-wired circuit such as an ASIC in which a circuit corresponding to a computer-readable instruction is incorporated. Further, it may be realized by using a circuit corresponding to a computer-readable instruction on the FPGA. Further, the processor 202, the main memory, the ASIC, the FPGA and the like may be appropriately combined and realized.
- the program required for execution may not only be installed on the verification server 200 via media, but may also be provided from a distribution server on the network.
- the verification of the intermediate representation 20 in the present embodiment includes a process of determining whether or not the intermediate representation 20 satisfies a predetermined rule or convention.
- the prescribed provisions or rules include conditions for the application program (intermediate representation 20 and corresponding execution code 30) to be safe.
- Typical conditions for such safety include the following.
- the undefined behavior in (2) above includes procedures and functions for which processing is not defined in the code.
- the error handling syntax of (3) above includes a description that defines the processing when an exception occurs.
- the disordered error handling in (4) above includes excessive error handling when an exception occurs.
- the predetermined provisions or rules include that the application program (intermediate representation 20 and the corresponding execution code 30) does not have a so-called backdoor.
- a backdoor is a function or connection port for a (usually malicious) third party to access the application program in a way that the user of the application program does not recognize.
- the access route from the outside is included in the intermediate representation 20.
- the verification process as described above may be realized by referring to the evaluation rule 216 (FIG. 5) including a predetermined rule or convention, or by using machine learning such as so-called AI (Artificial Intelligence).
- AI Artificial Intelligence
- the verification model for realizing the verification process may be updated sequentially.
- the verification process in the software development system 1 may be executed by the verification server 200 or may be executed by the software development device 100. When executing on the verification server 200, it may be implemented in the form of cloud computing. Further, when the verification process is executed in the software development device 100, the evaluation rule 216 certified by an external certification body may be used.
- the user or the like may be notified of the details of the contents determined not to satisfy the predetermined provisions or regulations.
- FIG. 6 is a flowchart showing an example of a processing procedure in the software development system 1 according to the present embodiment.
- the process executed by the software development device 100 shown in FIG. 6 may be typically realized by the processor 102 of the software development device 100 executing the software development program 114.
- the process executed by the verification server 200 may be typically realized by the processor 202 of the verification server 200 executing a necessary program.
- the software development device 100 creates the source code 10 according to the user operation (step S100). After creating the source code 10, the software development device 100 compiles the source code 10 according to the user operation and generates the intermediate representation 20 from the source code 10 (step S102).
- the software development device 100 requests the verification server 200 to verify the generated intermediate representation 20 (step S104), and waits for a response from the verification server 200 (step S106). In response to the verification request from the software development device 100, the verification server 200 verifies the requested intermediate representation 20 (step S200).
- steps S104 and S200 a process of verifying whether or not the intermediate representation 20 satisfies a predetermined rule or convention is executed.
- step S202 If the verification result is appropriate (YES in step S202), the software development device 100 responds to the software development device 100 with the authentication for the intermediate representation 20 (step S204). On the other hand, if the verification result is not appropriate (NO in step S202), the software development device 100 does not give authentication to the intermediate representation 20 and responds to the software development device 100 that the verification result is inappropriate (step). S206).
- the software development device 100 When the verification server 200 responds with the authentication for the intermediate representation 20 (YES in step S108), the software development device 100 generates the execution code 30 from the target intermediate representation 20 (step S110). Then, the software development device 100 transfers the generated execution code 30 to the target controller 300 (step S112). Then, the process ends.
- step S108 the software development device 100 informs the user that the source code 10 or the intermediate representation 20 does not satisfy a predetermined rule or convention. Notify (step S114).
- a process of notifying the user of the content that does not meet the predetermined rule or rule may be adopted. Then, the process ends.
- the execution code 30 generated in the software development system 1 according to the present embodiment is preferably stored in a secure area of a processor or a microcomputer constituting the distribution destination controller 300. That is, it is preferable to take some measures in the execution environment so that the execution code 30 generated on the condition that the intermediate representation 20 is authenticated is not tampered with.
- the generated hash value may be embedded, provided that the corresponding certificate 40 exists.
- the process of confirming the match between the signature included in the execution code 30 and the signature included in the corresponding certificate 40. May be implemented.
- the evaluation (judgment of validity) of whether or not to execute the execution code 30 may be performed at any timing, but typically, when the controller 300, which is the execution environment, is started ( It may be performed during the firmware startup or immediately after the startup (before the application execution starts). That is, when the controller 300 in which the execution code 30 is executed is started, the validity of the execution code 30 is evaluated based on the certificate 40 issued in association with the intermediate representation 20 that generated the execution code 30. You may. By confirming that the execution code 30 of the application program is authenticated when the controller 300 is started, it is possible to avoid a situation in which an unfavorable process is executed by the controller 300 or the like.
- the target intermediate representation 20 may be encrypted. As a result, it is possible to prevent falsification of the intermediate representation 20 exchanged between the software development device 100 and the verification server 200.
- the certificate 40 issued by the verification server 200 may be given a signature from a certificate authority or the like. As a result, fraudulent acts such as falsification of the certificate 40 issued by the verification server 200 can be prevented.
- the framework of verification of the intermediate representation 20 according to the present embodiment and issuance of a certificate 40 showing the verification result can also be applied to a mechanism for selling or distributing an application.
- an application developer uploads an application program (execution code 30) to an application distribution server
- the application is distributed by requesting that the corresponding intermediate representation 20 and / or certificate 40 be uploaded together.
- the execution code 30 to be distributed can be directly or indirectly verified on the server side. In this way, by introducing a mechanism according to the present embodiment, it is possible to avoid a situation in which an application program having a backdoor or the like is distributed.
- 1 Software development system 2 Internet, 4 Edge device, 10 Source code, 20 Intermediate expression, 30 Execution code, 40 Certificate, 100 Software development device, 102, 202 Processor, 104, 204 Main memory, 106, 206 Input section, 108,208 display, 110,210 hard disk, 114 software development program, 120,220 internal bus, 122,222 communication interface, 200 verification server, 212 evaluation engine, 214 certificate issuance engine, 216 evaluation rule, 300 controller.
Landscapes
- Engineering & Computer Science (AREA)
- Software Systems (AREA)
- Theoretical Computer Science (AREA)
- General Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Physics & Mathematics (AREA)
- General Physics & Mathematics (AREA)
- Computer Hardware Design (AREA)
- Stored Programmes (AREA)
- Devices For Executing Special Programs (AREA)
- Debugging And Monitoring (AREA)
Abstract
Description
まず、本実施の形態に従うソフトウェア開発システム1における処理の概要を説明する。本実施の形態においては、ソースコード10から生成される中間表現20自体を検証し、その検証結果が適切であることを条件に、対応する実行コード30の生成、あるいは、生成された実行コード30の実行を許容する。中間表現20に対する検証において、中間表現20が所定の規定あるいは規約を満たす場合に適切と判断される。
次に、本実施の形態に従うソフトウェア開発システム1を構成する主要装置のハードウェア構成例について説明する。
ソフトウェア開発装置100は、典型的には汎用コンピュータで実現される。
検証サーバ200についても、典型的には汎用コンピュータで実現される。
次に、本実施の形態に従うソフトウェア開発システム1における検証処理について説明する。
(2)コード中に未定義動作が存在しないこと
(3)エラー処理構文が欠如していないこと(エラー処理構文が適切に含まれていること)
(4)無秩序なエラー処理が含まれていないこと
上記(1)の安全性が確認できないメモリ操作(あるいは、危険なメモリ操作)は、システム領域やセキュア領域に対するメモリアクセスや、メモリ領域に対するブロック消去やブロック書き込みなどのメモリ操作を含む。
上記(4)の無秩序なエラー処理は、例外が発生した場合の過度なエラー処理などを含む。
次に、本実施の形態に従うソフトウェア開発システム1における処理手順について説明する。
本実施の形態に従うソフトウェア開発システム1において生成された実行コード30は、配布先のコントローラ300を構成するプロセッサあるいはマイクロコンピュータのセキュア領域に格納されることが好ましい。すなわち、中間表現20に対する認証を条件として生成された実行コード30に対して、何らかの改ざん行為が行われないように、実行環境において何らかの対処を行うことが好ましい。
ソフトウェア開発装置100から検証サーバ200へ中間表現20の検証を依頼する際には、対象の中間表現20を暗号化してもよい。これによって、ソフトウェア開発装置100と検証サーバ200との間で遣り取りされる中間表現20に対する改ざんなどを防止できる。
本実施の形態においては、ソースコード10ではなく中間表現20に対する検証を行うことで、ソースコード10に含まれるノウハウなどを秘匿化した状態で、アプリケーションプログラムに含まれる安全性についてのリスクをより効率的に発見できる。また、中間表現20に対する検証を行うことで、ソースコード10の記述に用いられたプログラミング言語の種類に応じた複数の検証ルールセットなどを用意する必要がなく、効率的な検証を実現できる。
Claims (7)
- ユーザ操作に従ってソースコードを作成するステップと、
前記ソースコードから中間表現を生成するステップと、
前記中間表現が所定の規定あるいは規約を満たしているか否かを検証するステップと、
前記中間表現が前記所定の規定あるいは規約を満たしている場合に、前記中間表現から生成される実行コードの実行を実現するステップとを備える、実行コード提供方法。 - 前記実行コードの実行を実現するステップは、前記中間表現が前記所定の規定あるいは規約を満たしていることを条件として、前記中間表現から前記実行コードを生成するステップを含む、請求項1に記載の実行コード提供方法。
- 前記実行コードの実行を実現するステップは、前記中間表現が前記所定の規定あるいは規約を満たしていることを条件として、前記中間表現から生成された前記実行コードの実行を許可するステップを含む、請求項1に記載の実行コード提供方法。
- 前記検証するステップは、前記中間表現が前記所定の規定あるいは規約を満たしている場合に、前記中間表現に関連付けられる証明書を発行するステップを含み、
前記中間表現から生成された前記実行コードの実行を許可するステップは、前記証明書に基づいて実行の可否を判断するステップを含む、請求項3に記載の実行コード提供方法。 - 前記実行コードが実行されるコントローラの起動時に、当該実行コードを生成した中間表現に関連付けて発行された証明書に基づいて、当該実行コードの正当性を評価するステップをさらに備える、請求項3または4に記載の実行コード提供方法。
- 前記検証するステップは、前記中間表現が前記所定の規定あるいは規約を満たしていない場合に、前記所定の規定あるいは規約を満たしていない内容をユーザに通知するステップを含む、請求項1~5のいずれか1項に記載の実行コード提供方法。
- ソフトウェア開発システムであって、
ソースコードの作成を支援するソフトウェア開発装置と、
前記ソフトウェア開発装置からアクセス可能な検証サーバとを備え、
前記ソフトウェア開発装置は、前記ソースコードから中間表現を生成する手段を備え、
前記検証サーバは、前記中間表現が所定の規定あるいは規約を満たしているか否かを検証する手段を備え、
前記中間表現が前記所定の規定あるいは規約を満たしている場合に、前記中間表現から生成される実行コードの実行が実現される、ソフトウェア開発システム。
Priority Applications (3)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| EP20833083.7A EP3992777B1 (en) | 2019-06-26 | 2020-06-24 | Execution code provision method and software development system |
| US17/622,573 US12332994B2 (en) | 2019-06-26 | 2020-06-24 | Execution code provision method and software development system |
| US19/216,372 US20250284793A1 (en) | 2019-06-26 | 2025-05-22 | Execution code provision method and software development system |
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2019119106A JP7672041B2 (ja) | 2019-06-26 | 2019-06-26 | 情報処理方法および情報処理システム |
| JP2019-119106 | 2019-06-26 |
Related Child Applications (2)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| US17/622,573 A-371-Of-International US12332994B2 (en) | 2019-06-26 | 2020-06-24 | Execution code provision method and software development system |
| US19/216,372 Continuation US20250284793A1 (en) | 2019-06-26 | 2025-05-22 | Execution code provision method and software development system |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2020262456A1 true WO2020262456A1 (ja) | 2020-12-30 |
Family
ID=74060407
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/JP2020/024799 Ceased WO2020262456A1 (ja) | 2019-06-26 | 2020-06-24 | 実行コード提供方法およびソフトウェア開発システム |
Country Status (5)
| Country | Link |
|---|---|
| US (2) | US12332994B2 (ja) |
| EP (1) | EP3992777B1 (ja) |
| JP (2) | JP7672041B2 (ja) |
| TW (2) | TWI842920B (ja) |
| WO (1) | WO2020262456A1 (ja) |
Families Citing this family (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP7672041B2 (ja) * | 2019-06-26 | 2025-05-07 | 久利寿 帝都 | 情報処理方法および情報処理システム |
| CN116028057A (zh) * | 2021-10-27 | 2023-04-28 | 北京字节跳动网络技术有限公司 | 代码管理的方法和装置 |
| CN116055556B (zh) * | 2021-10-27 | 2025-08-19 | 北京字节跳动网络技术有限公司 | 用于数据交换的方法、系统、装置和设备 |
Citations (5)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JPH04312130A (ja) * | 1991-04-10 | 1992-11-04 | Nec Corp | 言語処理プログラム |
| JP2001075814A (ja) * | 1999-08-19 | 2001-03-23 | Internatl Business Mach Corp <Ibm> | コンパイル装置およびその方法 |
| JP2003122730A (ja) * | 2001-10-12 | 2003-04-25 | Ntt Comware Corp | 情報処理方法、エージェントシステム、エージェントシステムプログラム及びエージェントシステムプログラムが記録された記録媒体 |
| JP2006522972A (ja) * | 2003-04-14 | 2006-10-05 | ジェムプリュス | リプログラマブル・オンボード・システムにダウンロードされた実行可能コードを管理するための方法 |
| JP2014174577A (ja) | 2013-03-05 | 2014-09-22 | Ntt Data Corp | 検証装置、検証方法、及びプログラム |
Family Cites Families (20)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US5748964A (en) * | 1994-12-20 | 1998-05-05 | Sun Microsystems, Inc. | Bytecode program interpreter apparatus and method with pre-verification of data type restrictions |
| US6128774A (en) * | 1997-10-28 | 2000-10-03 | Necula; George C. | Safe to execute verification of software |
| KR20010072477A (ko) | 1998-08-13 | 2001-07-31 | 썬 마이크로시스템즈, 인코포레이티드 | 가상 머신 환경에서 네이티브 코드를 변환하고 실행하는방법 및 장치 |
| WO2000022549A1 (en) | 1998-10-09 | 2000-04-20 | Koninklijke Philips Electronics N.V. | Automatic inquiry method and system |
| US6154842A (en) | 1998-10-13 | 2000-11-28 | Motorola, Inc. | Method and system for reducing time and power requirements for executing computer-readable instruction streams in an execution environment having run-time security constraints |
| US6560774B1 (en) * | 1999-09-01 | 2003-05-06 | Microsoft Corporation | Verifier to check intermediate language |
| JP4532810B2 (ja) * | 2002-02-22 | 2010-08-25 | キヤノン株式会社 | 画像処理装置、画像処理装置の制御方法、プログラム、及びコンピュータ読み取り可能な記憶媒体 |
| JP3956112B2 (ja) | 2002-06-12 | 2007-08-08 | インターナショナル・ビジネス・マシーンズ・コーポレーション | コンパイラ、レジスタ割当装置、プログラム、記録媒体、コンパイル方法、及びレジスタ割当方法 |
| JP2004303114A (ja) * | 2003-04-01 | 2004-10-28 | Hitachi Ltd | インタープリタおよびネイティブコード実行方法 |
| US7966610B2 (en) * | 2005-11-17 | 2011-06-21 | The Mathworks, Inc. | Application of optimization techniques to intermediate representations for code generation |
| US7934197B2 (en) * | 2006-12-19 | 2011-04-26 | Telefonaktiebolaget Lm Ericsson (Publ) | Maintaining code integrity in a central software development system |
| US8037466B2 (en) * | 2006-12-29 | 2011-10-11 | Intel Corporation | Method and apparatus for merging critical sections |
| JP5540160B2 (ja) | 2011-11-15 | 2014-07-02 | 独立行政法人科学技術振興機構 | プログラム解析・検証サービス提供システム、その制御方法、制御プログラム、コンピュータを機能させるための制御プログラム、プログラム解析・検証装置、プログラム解析・検証ツール管理装置 |
| JP5867088B2 (ja) * | 2012-01-05 | 2016-02-24 | 富士電機株式会社 | 組込み機器用ソフトウェア作成支援装置およびプログラム |
| US20160004517A1 (en) * | 2014-07-01 | 2016-01-07 | Bank Of America Corporation | SOFTWARE DEVELOPMENT IMPROVEMENT TOOL - iREVIEW |
| TWI791418B (zh) * | 2015-12-08 | 2023-02-11 | 美商飛塔公司 | 用以檢測運作時期所產生碼中之惡意碼的系統及方法、與相關電腦程式產品 |
| US9805200B2 (en) * | 2016-02-01 | 2017-10-31 | Quanta Computer, Inc. | System and method for firmware verification |
| US10423518B2 (en) * | 2016-04-27 | 2019-09-24 | The Mathworks, Inc. | Systems and methods for analyzing violations of coding rules |
| EP3610395B1 (en) * | 2017-05-31 | 2025-02-12 | Shiftleft Inc. | Method for application security profiling |
| JP7672041B2 (ja) * | 2019-06-26 | 2025-05-07 | 久利寿 帝都 | 情報処理方法および情報処理システム |
-
2019
- 2019-06-26 JP JP2019119106A patent/JP7672041B2/ja active Active
-
2020
- 2020-06-24 TW TW109121560A patent/TWI842920B/zh active
- 2020-06-24 EP EP20833083.7A patent/EP3992777B1/en active Active
- 2020-06-24 WO PCT/JP2020/024799 patent/WO2020262456A1/ja not_active Ceased
- 2020-06-24 US US17/622,573 patent/US12332994B2/en active Active
- 2020-06-24 TW TW113114585A patent/TWI899959B/zh active
-
2023
- 2023-12-26 JP JP2023219029A patent/JP7842412B2/ja active Active
-
2025
- 2025-05-22 US US19/216,372 patent/US20250284793A1/en active Pending
Patent Citations (5)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JPH04312130A (ja) * | 1991-04-10 | 1992-11-04 | Nec Corp | 言語処理プログラム |
| JP2001075814A (ja) * | 1999-08-19 | 2001-03-23 | Internatl Business Mach Corp <Ibm> | コンパイル装置およびその方法 |
| JP2003122730A (ja) * | 2001-10-12 | 2003-04-25 | Ntt Comware Corp | 情報処理方法、エージェントシステム、エージェントシステムプログラム及びエージェントシステムプログラムが記録された記録媒体 |
| JP2006522972A (ja) * | 2003-04-14 | 2006-10-05 | ジェムプリュス | リプログラマブル・オンボード・システムにダウンロードされた実行可能コードを管理するための方法 |
| JP2014174577A (ja) | 2013-03-05 | 2014-09-22 | Ntt Data Corp | 検証装置、検証方法、及びプログラム |
Non-Patent Citations (1)
| Title |
|---|
| See also references of EP3992777A4 |
Also Published As
| Publication number | Publication date |
|---|---|
| JP7672041B2 (ja) | 2025-05-07 |
| JP2024023911A (ja) | 2024-02-21 |
| US20250284793A1 (en) | 2025-09-11 |
| US20220269773A1 (en) | 2022-08-25 |
| TW202101200A (zh) | 2021-01-01 |
| TWI842920B (zh) | 2024-05-21 |
| JP7842412B2 (ja) | 2026-04-08 |
| TW202443383A (zh) | 2024-11-01 |
| EP3992777A4 (en) | 2023-07-19 |
| EP3992777C0 (en) | 2026-03-04 |
| TWI899959B (zh) | 2025-10-01 |
| EP3992777B1 (en) | 2026-03-04 |
| JP2021005250A (ja) | 2021-01-14 |
| US12332994B2 (en) | 2025-06-17 |
| EP3992777A1 (en) | 2022-05-04 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| JP5748905B2 (ja) | サンドボックスにリファレンスを保存するシステム及び方法 | |
| JP7842412B2 (ja) | 情報処理方法、情報処理システム、および情報処理プログラム | |
| JP5613259B2 (ja) | 非同期クライアント・サーバ・トランザクションを保護するための方法、システム、およびコンピュータ・プログラム | |
| US9871821B2 (en) | Securely operating a process using user-specific and device-specific security constraints | |
| JP6061364B2 (ja) | アプリケーションのセキュリティ検証のためのクラウド支援された方法及びサービス | |
| CN114175027A (zh) | 基于经验证的主要资产访问的相关资产访问 | |
| WO2015150391A9 (en) | Software protection | |
| KR20160018554A (ko) | 신뢰 및 비신뢰 플랫폼에 걸쳐 인터넷 액세스가능 애플리케이션 상태를 로밍하는 기법 | |
| US20210103651A1 (en) | Registration of dynamically created packaged applications | |
| JP5797666B2 (ja) | 計算リソースの安全な実行 | |
| WO2011096162A1 (ja) | 機密性分析支援システム、方法及びプログラム | |
| US20250272362A1 (en) | Protection-level based mechanism for securing artificial intelligence models | |
| JP7795729B2 (ja) | 情報処理装置、情報処理方法およびプログラム | |
| US12524211B2 (en) | Software use system and software use method | |
| US20260006018A1 (en) | Network authentication service security | |
| JP7335591B2 (ja) | コンピューティングシステムおよび情報処理方法 | |
| KR101440234B1 (ko) | 프로그램 무결성 관리 방법, 시스템 및 그 방법을 컴퓨터 상에서 실행하는 프로그램을 기록한 기록매체 | |
| WO2025178705A1 (en) | Distributed architecture and digital rights management for artificial intelligence models | |
| KR20250066388A (ko) | 서버에 대한 권한을 제어하기 위한 방법 및 장치 | |
| Alders | Formalizing the semantics of a dual-valued functional language in Coq |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 20833083 Country of ref document: EP Kind code of ref document: A1 |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| ENP | Entry into the national phase |
Ref document number: 2020833083 Country of ref document: EP Effective date: 20220126 |
|
| WWG | Wipo information: grant in national office |
Ref document number: 17622573 Country of ref document: US |
|
| WWG | Wipo information: grant in national office |
Ref document number: 2020833083 Country of ref document: EP |