KR20090054774A - 분산 네트워크 환경에서의 통합 보안 관리 방법 - Google Patents
분산 네트워크 환경에서의 통합 보안 관리 방법 Download PDFInfo
- Publication number
- KR20090054774A KR20090054774A KR1020070121627A KR20070121627A KR20090054774A KR 20090054774 A KR20090054774 A KR 20090054774A KR 1020070121627 A KR1020070121627 A KR 1020070121627A KR 20070121627 A KR20070121627 A KR 20070121627A KR 20090054774 A KR20090054774 A KR 20090054774A
- Authority
- KR
- South Korea
- Prior art keywords
- security
- value
- service terminal
- management server
- mutual authentication
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
- 238000007726 management method Methods 0.000 title claims abstract description 120
- 238000000034 method Methods 0.000 claims abstract description 55
- 238000012795 verification Methods 0.000 claims description 50
- 230000008569 process Effects 0.000 claims description 8
- 230000004044 response Effects 0.000 claims description 3
- 238000010586 diagram Methods 0.000 description 7
- 238000004364 calculation method Methods 0.000 description 5
- 238000004891 communication Methods 0.000 description 4
- 230000000694 effects Effects 0.000 description 3
- 238000013475 authorization Methods 0.000 description 2
- 238000012986 modification Methods 0.000 description 2
- 230000004048 modification Effects 0.000 description 2
- 230000003213 activating effect Effects 0.000 description 1
- 230000005540 biological transmission Effects 0.000 description 1
- 238000013461 design Methods 0.000 description 1
- 238000001514 detection method Methods 0.000 description 1
- 238000002474 experimental method Methods 0.000 description 1
- 230000007246 mechanism Effects 0.000 description 1
- 238000012544 monitoring process Methods 0.000 description 1
- 230000008520 organization Effects 0.000 description 1
Images




Classifications
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/08—Access security
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/06—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols the encryption apparatus using shift registers or memories for block-wise or stream coding, e.g. DES systems or RC4; Hash functions; Pseudorandom sequence generators
- H04L9/0618—Block ciphers, i.e. encrypting groups of characters of a plain text message using fixed encryption transformation
- H04L9/0631—Substitution permutation network [SPN], i.e. cipher composed of a number of stages or rounds each involving linear and nonlinear transformations, e.g. AES algorithms
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/32—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/02—Protecting privacy or anonymity, e.g. protecting personally identifiable information [PII]
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04W—WIRELESS COMMUNICATION NETWORKS
- H04W12/00—Security arrangements; Authentication; Protecting privacy or anonymity
- H04W12/06—Authentication
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Computer And Data Communications (AREA)
Abstract
Description


Claims (8)
- 네트워크상의 보안 정책 및 보안 사항을 관리하기 위한 보안관리서버와, 전자상거래 서비스를 제공하기 위한 서비스단말을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법에 있어서,상기 보안관리서버와 서비스단말간 상호인증을 위한 보안에이전트를 생성하는 제1단계;제3의 신뢰기관을 상호인증을 위한 정보교환의 매개로 하여 상기 보안에이전트와 상기 서비스단말간 상호인증을 수행하는 제2단계; 및상기 보안에이전트를 상호인증을 위한 정보교환의 매개로 하여 상기 보안관리서버와 상기 서비스단말간 상호인증을 수행하는 제3단계; 및상기 제3단계에서의 상호인증에 대한 유효성을 검증하는 제4단계를 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 1항에 있어서,상기 서비스단말로부터 서비스를 제공받기 원하는 클라이언트의 서비스 이용 권한정보를 설정하는 제5단계를 더 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 2항에 있어서,상기 제1단계는,상기 제3의 신뢰기관이 상기 보안관리서버의 요청에 따라 상기 보안에이전트를 생성하는 과정;상기 제3의 신뢰기관이 자신이 생성한 제1공개키서명값과, 상기 보안에이전트와 상기 서비스단말간 상호인증을 위한 상기 보안에이전트의 제1상호인증검증값, 및 상기 보안에이전트의 제1식별정보를 상기 보안에이전트에 등록하는 과정;상기 보안에이전트가 상기 제1공개키서명값, 상기 제1상호인증검증값 및 상기 제1식별정보를 자신의 고유코드정보로 하여 상기 보안관리서버에 할당되는 과정;상기 제3의 신뢰기관이 상기 고유코드정보를 상기 보안관리서버의 공개키로 암호화한 제1암호값을 상기 보안관리서버로 전송하는 과정; 및상기 보안관리서버가 상기 제1암호값을 복호화하여 상기 제1공개키서명값을 확보하는 과정을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 3항에 있어서,상기 제2단계는,상기 제3의 신뢰기관이 상기 보안에이전트로부터 상기 고유코드정보를 확보하고, 상기 보안에이전트와 상기 서비스단말간 상호인증을 위한 상기 서비스단말의 제2상호인증검증값을 상기 제3의 신뢰기관의 공개키로 암호화한 제2암호값을 상기 서비스단말로부터 확보하는 과정;상기 제3의 신뢰기관이 상기 보안에이전트와 상기 서비스단말간 상호인증을 위한 자신의 제3상호인증검증값을 상기 서비스단말이 생성한 타임스탬프값과 함께 해쉬한 제1해쉬값을 상기 보안에이전트로 전송하는 과정;상기 제3의 신뢰기관이 상기 제2암호값을 복호화하는 과정;싱기 제3의 신뢰기관이 상기 제3상호인증검증값을 자신이 생성한 타임스탬프값과 함께 해쉬한 제2해쉬값, 및 상기 제2해쉬값과 상기 제3상호인증검증값을 상기 서비스단말의 공개키로 암호화한 제3암호값을 상기 서비스단말로 전송하는 과정;상기 보안에이전트가 상기 제1해쉬값과 상기 제1공개키서명값을 상기 서비스단말로 전송하는 과정;상기 서비스단말이 상기 제2해쉬값을 상기 보안에이전트로 전송하는 과정; 및상기 보안에이전트와 상기 서비스단말이 상기 제1해쉬값 및 제2해쉬값을 통해 상기 제3상호인증검증값에 대한 무결성을 검증하는 과정을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 4항에 있어서,상기 제3단계는,상기 보안관리서버가 상기 보안관리서버 객체를 검증하기 위한 관리서버객체검증값과 상기 보안관리서버의 정보요청메시지를 상기 서비스단말의 공개키로 암호화한 제4암호값을 상기 정보요청메시지와 함께 상기 보안에이전트로 전송하는 과정;상기 보안에이전트가 상기 제1공개키서명값을 자신이 생성한 타임스탬프값과 함께 해쉬한 제3해쉬값과, 상기 제4암호값, 및 상기 제1공개키서명값을 상기 서비스단말로 전송하는 과정;상기 서비스단말이 상기 제3해쉬값을 이용하여 상기 제1공개키서명값의 무결성을 확인하는 과정;상기 서비스단말이 상기 서비스단말 객체를 검증하기 위한 서비스단말객체검증값과 상기 정보요청메시지에 대한 응답메시지를 상기 서비스단말의 공개키로 암호화한 제5암호값을 상기 보안에이전트로 전송하는 과정; 및상기 보안에이전트가 상기 제3해쉬값과, 상기 제5암호값, 및 상기 제1공개키서명값을 상기 보안관리서버로 전송하는 과정을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
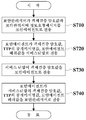
- 제 5항에 있어서,상기 제4단계는,상기 보안관리서버가 상기 보안에이전트로부터 수신한 상기 제5암호값을 복호화하여 확보한 서비스단말객체검증값을 상기 서비스단말로 전송하고, 상기 서비스단말이 상기 보안에이전트로부터 수신한 상기 제4암호값을 복호화하여 확보한 관리서버객체검증값을 상기 보안관리서버로 전송하는 과정; 및상기 보안관리서버가 상기 서비스단말로부터 수신한 관리서버객체검증값과 자신이 생성한 관리서버객체검증값을 비교하고, 상기 서비스단말이 상기 보안관리서버로부터 수신한 서비스단말객체검증값과 자신이 생성한 서비스단말객체검증값을 비교하여 전송되는 정보들의 유효성을 검증하는 과정을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 6항에 있어서,상기 제5단계는,상기 보안관리서버가 상기 클라이언트의 제2식별정보 및 패스워드와, 상기 제1상호인증검증값을 상기 클라이언트로부터 수신하는 과정;상기 보안관리서버가 상기 제1상호인증검증값의 정당성을 검증하는 과정;상기 보안관리서버가 상기 보안에이전트를 생성한 타임스탬프값 및 생성을 요청한 보안관리서버의 정보와, 상기 제1식별정보를 기반으로 상기 서비스 이용 권한정보를 생성하는 과정; 및상기 서비스 이용 권한정보 및 상기 제2식별정보를 상기 서비스단말로 전송하는 과정을 포함하는 분산 네트워크 환경에서의 통합 보안 관리 방법.
- 제 3항 내지 제 7항 중 어느 한 항에 있어서,상기 제1공개키서명값은 상기 제3의 신뢰기관의 개인키와 상기 보안에이전트의 고유값을 기반으로 생성되는 분산 네트워크 환경에서의 통합 보안 관리 방법.
Priority Applications (1)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| KR1020070121627A KR20090054774A (ko) | 2007-11-27 | 2007-11-27 | 분산 네트워크 환경에서의 통합 보안 관리 방법 |
Applications Claiming Priority (1)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| KR1020070121627A KR20090054774A (ko) | 2007-11-27 | 2007-11-27 | 분산 네트워크 환경에서의 통합 보안 관리 방법 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| KR20090054774A true KR20090054774A (ko) | 2009-06-01 |
Family
ID=40986663
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| KR1020070121627A Ceased KR20090054774A (ko) | 2007-11-27 | 2007-11-27 | 분산 네트워크 환경에서의 통합 보안 관리 방법 |
Country Status (1)
| Country | Link |
|---|---|
| KR (1) | KR20090054774A (ko) |
Cited By (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| KR101273285B1 (ko) * | 2011-06-03 | 2013-06-11 | (주)네오위즈게임즈 | 인증 에이전트 장치, 온라인 서비스 인증 방법 및 시스템 |
| KR20180006122A (ko) * | 2016-07-08 | 2018-01-17 | 주식회사 한국스마트카드 | Rf 패드와 cat 단말 간의 상호 인증 방법 |
| CN108512856A (zh) * | 2018-04-11 | 2018-09-07 | 杭州电子科技大学 | 物联网中传感信息虚拟服务的隐私保护方法 |
| KR20210045636A (ko) * | 2019-10-17 | 2021-04-27 | 한국전자인증 주식회사 | 블록체인 기반 사용자 주도의 신뢰된 대상 간 문서 유통 방법 및 시스템 |
| WO2021187782A1 (ko) * | 2020-03-18 | 2021-09-23 | (주)수산아이앤티 | 악성 트래픽 검출 방법 및 그 장치 |
| KR102443713B1 (ko) | 2021-12-30 | 2022-09-16 | 주식회사 제네럴테크놀로지 | 차세대 융합 보안 시스템 |
-
2007
- 2007-11-27 KR KR1020070121627A patent/KR20090054774A/ko not_active Ceased
Cited By (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| KR101273285B1 (ko) * | 2011-06-03 | 2013-06-11 | (주)네오위즈게임즈 | 인증 에이전트 장치, 온라인 서비스 인증 방법 및 시스템 |
| KR20180006122A (ko) * | 2016-07-08 | 2018-01-17 | 주식회사 한국스마트카드 | Rf 패드와 cat 단말 간의 상호 인증 방법 |
| CN108512856A (zh) * | 2018-04-11 | 2018-09-07 | 杭州电子科技大学 | 物联网中传感信息虚拟服务的隐私保护方法 |
| KR20210045636A (ko) * | 2019-10-17 | 2021-04-27 | 한국전자인증 주식회사 | 블록체인 기반 사용자 주도의 신뢰된 대상 간 문서 유통 방법 및 시스템 |
| WO2021187782A1 (ko) * | 2020-03-18 | 2021-09-23 | (주)수산아이앤티 | 악성 트래픽 검출 방법 및 그 장치 |
| KR102443713B1 (ko) | 2021-12-30 | 2022-09-16 | 주식회사 제네럴테크놀로지 | 차세대 융합 보안 시스템 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| US12143476B2 (en) | Method of data transfer, a method of controlling use of data and cryptographic device | |
| CN108432180B (zh) | 用于基于pki的认证的方法和系统 | |
| JP5860815B2 (ja) | コンピューターポリシーを施行するためのシステムおよび方法 | |
| CN103685282B (zh) | 一种基于单点登录的身份认证方法 | |
| CA2357792C (en) | Method and device for performing secure transactions | |
| CN114008968B (zh) | 用于计算环境中的许可授权的系统、方法和存储介质 | |
| IL266535A (en) | A system and method for clear multi-factor authentication and security posture testing | |
| JP2014531163A5 (ko) | ||
| JP2014531163A (ja) | サードパーティーアプリケーションの集中型セキュアマネージメント方法、システム、および対応する通信システム | |
| JP5602165B2 (ja) | ネットワーク通信を保護する方法および装置 | |
| JP2016521029A (ja) | セキュリティ管理サーバおよびホームネットワークを備えるネットワークシステム、およびそのネットワークシステムにデバイスを含めるための方法 | |
| JP5452192B2 (ja) | アクセス制御システム、アクセス制御方法およびプログラム | |
| CN114079645A (zh) | 注册服务的方法及设备 | |
| Tiwari et al. | Design and Implementation of Enhanced Security Algorithm for Hybrid Cloud using Kerberos | |
| KR100970552B1 (ko) | 비인증서 공개키를 사용하는 보안키 생성 방법 | |
| CN114003892B (zh) | 可信认证方法、安全认证设备及用户终端 | |
| KR20150005789A (ko) | 인증서를 이용한 사용자 인증 방법 | |
| Jang | System Access Control Technique for Secure Cloud Computing | |
| CN119382888B (zh) | 用户认证方法、智能业务系统、设备、介质及程序 | |
| CN114996770B (zh) | 基于宿管系统的身份识别方法 | |
| JP2014081887A (ja) | セキュアシングルサインオン方式およびプログラム | |
| Torrellas et al. | An authentication protocol for agent platform security manager | |
| WO2025163753A1 (ja) | 端末、通信システム、通信方法、及びプログラム | |
| HK40071947A (en) | A method of data transfer, a method of controlling use of data and a cryptographic device | |
| HK40068823A (en) | Systems, methods, and storage media for permissioned delegation in a computing environment |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| A201 | Request for examination | ||
| PA0109 | Patent application |
Patent event code: PA01091R01D Comment text: Patent Application Patent event date: 20071127 |
|
| PA0201 | Request for examination | ||
| PG1501 | Laying open of application | ||
| E902 | Notification of reason for refusal | ||
| PE0902 | Notice of grounds for rejection |
Comment text: Notification of reason for refusal Patent event date: 20090908 Patent event code: PE09021S01D |
|
| E601 | Decision to refuse application | ||
| PE0601 | Decision on rejection of patent |
Patent event date: 20100305 Comment text: Decision to Refuse Application Patent event code: PE06012S01D Patent event date: 20090908 Comment text: Notification of reason for refusal Patent event code: PE06011S01I |